
Ethical Hacking Education is best understood as curiosity with a leash: the skill of probing systems for weakness while staying firmly inside permission, scope, and duty of care. The diagram makes that discipline visible. Learners arrive with inputs—technical foundations and realistic scenarios—but they do not “explore freely”; their learning is shaped by controls such as authorization rules, written scope, reporting standards, and ethical expectations that treat people’s data and systems as non-negotiable responsibilities. With mechanisms like guided instruction and sandbox labs, students practice the professional cycle: observe how systems are structured, identify where risk concentrates, test in controlled ways, and then translate what they learn into clear reports and practical fixes. The output is not reckless cleverness, but accountable competence—security testers who can help organizations find problems early, explain them calmly, and strengthen systems without crossing legal or ethical lines.
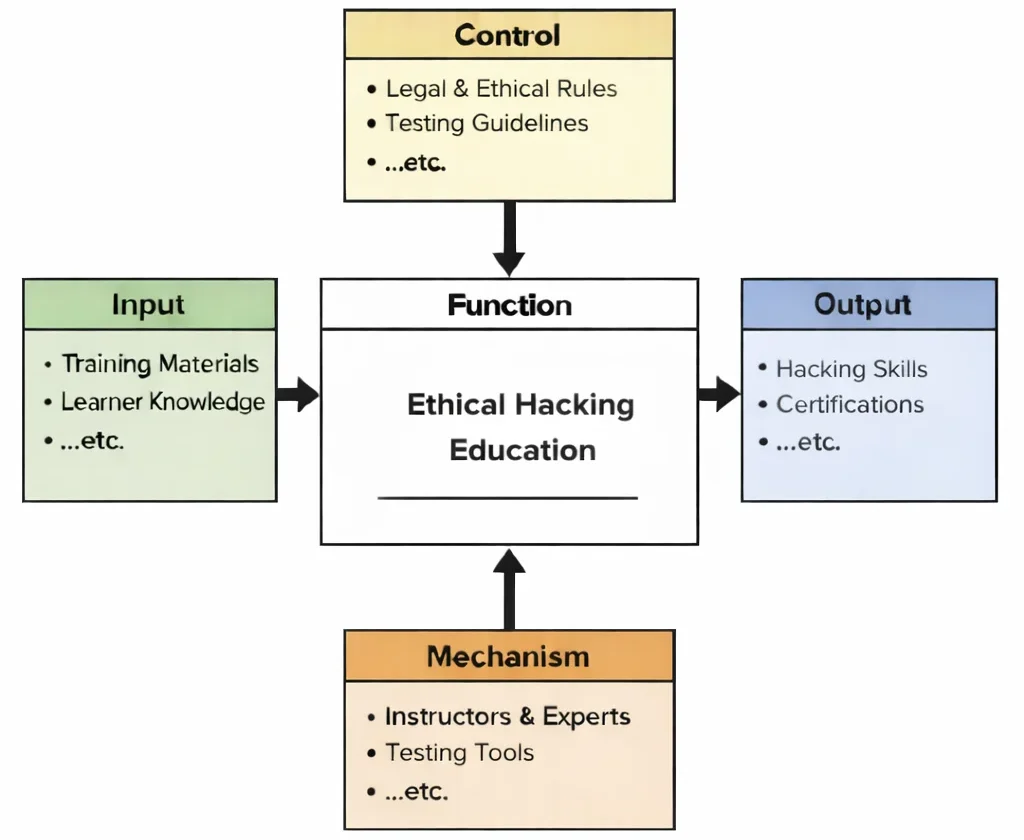
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Ethical Hacking Education as a structured transformation process. Inputs include learning materials, practice scenarios, and baseline knowledge of systems and networks. Controls include legal/ethical boundaries, authorization requirements, policies, scope definitions, and curriculum outcomes that ensure all testing is responsible and permitted. Mechanisms include instructors, lab environments, simulated targets, and approved security tools used for safe experimentation. Outputs include learners who can think like defenders by understanding attacker tactics conceptually, perform authorized security assessments, document findings clearly, and recommend mitigations—often aligned with assessments or certifications.
Interactive Check: Intro & System Concepts
Verify your understanding of how authorized scope, legal boundaries, and offensive simulations strengthen defensive security postures:
Introductory Concept Verification
1. Why is ethical hacking described as “curiosity with a leash”?
Answer: Ethical hackers utilize the same offensive techniques, mindsets, and tools as malicious threat actors to discover system flaws, but operate strictly under legally binding authorization, defined scopes, and professional duties of care to prevent operational disruption or unauthorized data leakage.
2. What is the fundamental output expected from Ethical Hacking Education?
Answer: Accountable competence: security practitioners who can execute authorized penetration tests, analyze exploit chains, document technical findings clearly for stakeholders, and recommend actionable remediation patches without crossing legal or ethical boundaries.
Ethical hacking plays a pivotal role in fortifying digital systems by simulating the tactics of malicious attackers—only with permission and a protective purpose. As a cornerstone of modern cybersecurity strategies, ethical hackers help organizations discover vulnerabilities before adversaries exploit them. These professionals operate at the intersection of offensive testing and defensive hardening, contributing directly to enhanced application security and robust cloud security frameworks.
The scope of ethical hacking has broadened significantly with the rise of complex systems like cyber-physical systems (CPS) and operational technology (OT). Simulating attacks on these interconnected infrastructures requires deep knowledge of system architecture and secure protocol design, often grounded in the principles of cryptography and access control. Moreover, ethical hackers contribute to the development and refinement of cybersecurity policies by identifying gaps and setting benchmarks for preventive measures.
As the threat landscape evolves, ethical hackers increasingly rely on AI and ML in cybersecurity to uncover patterns, automate reconnaissance, and perform risk assessments at scale. These capabilities are especially useful in endpoint security, where dynamic threat detection must account for a wide array of devices and configurations. In parallel, incident response and digital forensics benefit from ethical hacking insights to trace intrusions and uncover their root causes.
A foundational component of effective ethical hacking is identity and access management. Understanding how identities are authenticated and authorized allows ethical hackers to pinpoint potential escalation paths and weaknesses. Additionally, expertise in network security enables the simulation of attack vectors like packet sniffing, spoofing, and lateral movement across systems.
The rise of emerging areas in cybersecurity—such as zero trust architectures and deception technologies—has amplified the need for sophisticated ethical hacking practices. Equally important is cultivating cybersecurity awareness among employees to reduce the success rate of phishing and social engineering attacks, areas where ethical hackers conduct training exercises.
Ethical hacking is also informed by the expanding role of data in security. Fields such as data science and analytics provide powerful methods to assess and visualize system behavior under simulated stress. Tools in data science technologies allow hackers to automate reconnaissance and log analysis. Through data analysis and big data analytics, practitioners can uncover anomalous behaviors that signal underlying flaws.
Just as critical is the role of data cleaning and preprocessing, especially when ethical hackers examine massive log files or behavioral datasets for indicators of compromise. They often leverage insights from domain-specific analytics to tailor attacks and defenses to specific industries like finance, healthcare, or manufacturing. Meanwhile, techniques in data visualization are used to clearly present risk landscapes and exploit chains to both technical and non-technical audiences.
Importantly, ethical hacking must be grounded in ethical and social considerations. Responsible hacking requires not only technical expertise but also a firm understanding of legality, consent, and professional integrity. As a bridge between offense and defense, ethical hackers ensure that systems are resilient, trusted, and aligned with broader societal values.
This image portrays ethical hacking as a disciplined, permission-based form of security testing. A hooded figure at a keyboard symbolizes the “attacker mindset” used in penetration testing, while the prominent padlock and shield icons emphasize defensive goals—protecting systems, not harming them. Surrounding panels of code-like dashboards and security graphics suggest activities such as vulnerability scanning, controlled exploitation, and reporting. The repeated references to “ethical hacking” and “penetration testing” reinforce the idea of legitimate, structured work carried out under clear rules, scope, and authorization. Overall, the visual communicates that ethical hackers help organizations improve security by safely uncovering weaknesses and strengthening safeguards before incidents occur.
Building Cyber Resilience: Ethical Hacking Navigation
Discover how Ethical Hacking and Penetration Testing uncover system vulnerabilities, evaluate defense-in-depth controls, and guide remediation across the Cybersecurity cluster. Each card details vulnerability scanning, exploit verification, black/white/gray box testing, and Rules of Engagement (RoE).
Cybersecurity Overview
Presents the overarching macro-architecture, mapping how offensive penetration testing validates defensive security controls and informs organizational risk models.
Network Security
Examines network port scanning (Nmap), packet sniffing (Wireshark), ARP spoofing simulations, and testing perimeter firewall rules.
Application Security
Focuses on dynamic web application security testing (Burp Suite/OWASP ZAP), probing for SQL injection, XSS, CSRF, and IDOR flaws.
Cloud Security
Details cloud environment auditing (Pacu/ScoutSuite), testing S3 bucket access controls, IAM privilege escalation, and serverless isolation checks.
Endpoint Security
Covers local privilege escalation testing, bypassing EDR anti-tamper controls, evaluating AppLocker rules, and testing AMSI script scanning.
Identity & Access Management
Governs Kerberoasting simulations, password spraying audits, testing MFA bypass vulnerabilities, and evaluating Active Directory privilege trees.
Cryptography
Applies cipher suite weakness audits, testing for weak random number generators, verifying SSL/TLS certificate chains, and analyzing side-channel leaks.
Incident Response & Forensics
Orchestrates Red Team vs. Blue Team purple-teaming exercises, validating SIEM detection rule latency and testing SOC containment response speeds.
Threat Intelligence
Feeds real-world threat actor TTPs (MITRE ATT&CK matrix) into penetration testing playbooks to mimic active advanced persistent threat (APT) campaigns.
Ethical Hacking
Focuses on authorized penetration testing, vulnerability assessment (Nessus/Qualys), Metasploit exploitation, black/gray/white box methodologies, and remediation reporting.
Cybersecurity Awareness
Executes controlled social engineering simulations (phishing, pretexting, tailgating) to evaluate and improve employee security awareness.
Policy & Governance
Codifies formal Rules of Engagement (RoE) agreements, bug bounty policy management, authorization scope documents, and vulnerability disclosure programs.
CPS Security
Protects cyber-physical testbeds, simulating GPS relay attacks, CAN bus injection on autonomous vehicles, and medical device telemetry auditing.
OT Security
Safeguards industrial control networks, executing non-disruptive SCADA/PLC protocol audits without interrupting manufacturing operations.
AI & ML in Security
Leverages AI for automated vulnerability discovery while executing adversarial AI red-teaming (prompt injection, model extraction, data poisoning).
Emerging Areas
Investigates smart contract security auditing (MythX), Web3 protocol vulnerability testing, and zero-knowledge proof verification testing.
Key Topics in Ethical Hacking & Penetration Testing
Ethical hacking follows structured, authorized methodologies to evaluate digital defense posture:
Conducting Vulnerability Assessments
- Discovery & Analysis: Utilizing automated scanners (Nessus, OpenVAS, Qualys) to identify open ports, unpatched software versions, and misconfigured services.
- Prioritization: Ranking discovered vulnerabilities according to CVSS severity scores and exploitability metrics to focus patch remediation.
Exploitation Techniques and Tools
- Controlled Exploitation: Safely executing proof-of-concept exploits to verify vulnerability impact without causing system outages.
- Primary Toolsets: Metasploit Framework for exploit validation, Burp Suite for web application analysis, Nmap for network mapping, and Wireshark for packet capture.
Reporting and Patching Identified Weaknesses
- Executive & Technical Reports: Documenting findings with non-technical executive summaries alongside granular technical step-by-step reproduction proofs and remediation guides.
Types of Penetration Testing Methodologies
Testing engagements vary based on the level of target system knowledge provided:
- Black Box Testing: Testers operate with zero prior internal knowledge, simulating an external adversary probing perimeter defenses.
- White Box Testing: Testers have complete access to system architecture, network diagrams, and source code, allowing deep auditing of complex logic.
- Gray Box Testing: Testers operate with limited knowledge (such as standard user login credentials), simulating an insider threat or compromised user account.
Emerging Trends in Ethical Hacking
Next-generation offensive security paradigms:
- AI-Powered Penetration Testing: Utilizing machine learning models to automate dynamic vulnerability scanning and adapt payload generation in real time.
- Cloud & Container Pen Testing: Evaluating misconfigured S3 buckets, overly permissive IAM execution roles, and container breakout vulnerabilities using tools like Pacu and ScoutSuite.
- Continuous Security Testing: Shifting from annual point-in-time penetration tests to continuous automated breach and attack simulation (BAS) platforms.
Why Study Ethical Hacking
Mastering offensive security techniques provides vital insight for building resilient defenses:
- Thinking Like an Attacker: Teaches engineers to anticipate threat vectors and build proactive, defense-in-depth architectures.
- Hands-On Exploitation Mastery: Provides practical experience with industry-standard security tools (Nmap, Metasploit, Burp Suite) in controlled sandbox labs.
- Professional Ethics & Integrity: Instills strict adherence to legal authorization boundaries, confidentiality agreements, and responsible vulnerability disclosure.
Interactive Quick Review: Ethical Hacking Concepts
Reinforce key concepts regarding rules of engagement, testing methodologies, and vulnerability reporting before reading the FAQ:
Quick Review Verification
1. Why are formal Rules of Engagement (RoE) mandatory prior to starting any penetration test?
Answer: Rules of Engagement establish explicit legal boundaries, authorized target IP ranges, permitted testing hours, excluded sensitive systems (to avoid production outages), and emergency contact channels, protecting both the client and the tester legally and operationally.
2. What is the difference between a Vulnerability Assessment and a Penetration Test?
Answer: A vulnerability assessment identifies and lists potential weaknesses across systems using automated scanners. A penetration test actively executes controlled exploits against those identified flaws to demonstrate real-world impact and lateral movement possibilities.
Ethical Hacking – Frequently Asked Questions
What is ethical hacking in cybersecurity?
Ethical hacking is the authorized practice of probing computer systems, networks, and applications to discover security weaknesses before malicious threat actors can exploit them.
How does ethical hacking differ from malicious hacking?
Ethical hackers operate legally with explicit written permission, defined scope, and protective intent. Malicious hackers breach systems illegally without consent to steal data, cause damage, or extort victims.
What are the typical phases of a penetration test?
1. Planning & Scoping; 2. Reconnaissance & Intelligence Gathering; 3. Vulnerability Scanning; 4. Exploitation; 5. Post-Exploitation & Lateral Movement; 6. Reporting & Remediation.
Is ethical hacking legal, and what permissions are required?
Yes, ethical hacking is fully legal when conducted under written authorization (Rules of Engagement contract) signed by the system owner explicitly detailing allowed scope and dates.
How can students safely practice ethical hacking skills?
In dedicated, isolated sandbox environments: local virtual machine labs (Metasploitable), capture-the-flag (CTF) platforms (Hack The Box, TryHackMe), and university cyber ranges.
What certifications are recognized in ethical hacking?
Offensive Security Certified Professional (OSCP), Certified Ethical Hacker (CEH), GIAC Penetration Tester (GPEN), and CompTIA PenTest+.
Ethical Hacking and Penetration Testing: Conclusion
Ethical hacking and penetration testing are essential components of a comprehensive cybersecurity strategy. By identifying and addressing vulnerabilities, organizations can safeguard their systems, maintain trust, and stay resilient against evolving cyber threats.
- Authorized Scope: Always obtain explicit, signed authorization before conducting security testing.
- Controlled Exploitation: Demonstrate vulnerability impact safely without risking system downtime.
- Actionable Reporting: Provide clear technical remediation paths alongside executive risk summaries.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is ethical hacking and why is it essential in cybersecurity?
Answer: Ethical hacking is the authorized probing of systems to discover and fix vulnerabilities before malicious actors exploit them. It is essential because it proactively identifies security flaws under real-world attack conditions.
2. How does ethical hacking differ from malicious hacking?
Answer: In intent and authorization. Ethical hackers have explicit permission, work within defined boundaries, and document findings to improve security. Malicious hackers act illegally without authorization to harm or steal.
3. What methodologies are commonly used in ethical hacking?
Answer: Penetration Testing Execution Standard (PTES), OWASP Testing Guide, and NIST SP 800-115, governing reconnaissance, scanning, exploitation, and reporting.
4. How do penetration testing and vulnerability assessments complement each other?
Answer: Vulnerability assessments broad-scan systems to identify potential flaws. Penetration tests deep-probe specific vulnerabilities to verify if they can be actively exploited to compromise data.
5. What role do legal and ethical frameworks play in guiding ethical hacking?
Answer: They define explicit operational boundaries, preventing unauthorized access law violations (Computer Fraud and Abuse Act) and ensuring tests preserve data privacy and operational stability.
6. What key tools and techniques are utilized by ethical hackers during security assessments?
Answer: Nmap for port scanning, Nessus for vulnerability scanning, Metasploit for exploit validation, Burp Suite for web API testing, and Wireshark for packet analysis.
7. How do ethical hackers identify and exploit vulnerabilities without causing damage?
Answer: By executing non-destructive proof-of-concept scripts in staging environments, setting rate limits during scans, and avoiding dangerous Denial of Service (DoS) payloads.
8. What is the importance of certifications and formal training in ethical hacking?
Answer: Certifications (OSCP, CEH, GPEN) validate hands-on technical proficiency, verify understanding of legal boundaries, and ensure adherence to professional codes of ethics.
9. How can organizations benefit from incorporating ethical hacking into cybersecurity?
Answer: Reduces data breach risk, validates security control effectiveness, ensures regulatory compliance (PCI DSS/HIPAA), and improves incident response preparedness.
10. What challenges do ethical hackers face during security assessments?
Answer: Complex multi-cloud architectures, strict testing time windows, avoiding disruption to live services, false positives, and navigating ambiguous authorization scopes.
Thought-Provoking Architectural Questions
1. How will the integration of artificial intelligence reshape the methods of ethical hacking?
Answer: AI will automate multi-step exploit generation, dynamically discover complex logic flaws in microservice APIs, and conduct autonomous red-teaming simulations at machine speed.
2. In what ways could the ethical boundaries of hacking be challenged as technology advances?
Answer: Testing invasive technologies like AI deepfakes, employee biometric authentication, or brain-computer interfaces creates ethical tensions between security verification and personal privacy infringement.
3. How can ethical hacking be integrated into broader cybersecurity strategies for proactive defense?
Answer: By adopting continuous Breach and Attack Simulation (BAS) pipelines, conducting regular Purple Team collaborative exercises, and tying penetration test findings directly into automated DevSecOps patch workflows.
4. What potential impact might emerging technologies (IoT, Blockchain) have on ethical hacking techniques?
Answer: Shifts focus toward hardware reverse engineering, radio frequency (RF) protocol fuzzing, smart contract reentrancy auditing, and formal mathematical verification of decentralized ledgers.
5. How might reliance on cloud services transform the role of ethical hacking?
Answer: Testers shift from network port scanning toward auditing cloud API configurations, IAM role privilege escalation paths, container escape vulnerabilities, and serverless execution environments.
6. What are the long-term implications of widespread ethical hacking adoption on global security standards?
Answer: Drives transition toward secure-by-design software development models, mandatory bug bounty programs across software vendors, and higher baseline resilience across critical societal infrastructure.
7. How can ethical hackers ensure findings are effectively communicated to non-technical stakeholders?
Answer: By mapping technical vulnerabilities to business financial impact, using clear risk rating heatmaps, and providing high-level executive summaries alongside remediation cost estimations.
8. What challenges do ethical hackers face when testing highly secure or proprietary systems?
Answer: Advanced EDR anti-tamper controls, custom non-standard network protocols, lack of system documentation, and risk of triggering accidental system lockouts or hardware damage.
9. How might ethical hacking evolve to address complex cyber-physical systems?
Answer: Combines digital network exploitation with control theory modeling, verifying that physical safety interlocks remain functional even if digital controllers are fully compromised.
10. What potential ethical dilemmas arise as ethical hacking becomes more invasive?
Answer: Accessing sensitive employee personal data during social engineering tests or discovering critical zero-day vulnerabilities in third-party software during client assessments.
11. How can cross-industry collaboration foster innovation in ethical hacking?
Answer: Sharing standardized testing frameworks, publishing open-source exploit simulation tools, and collaborating on standardized vulnerability disclosure guidelines.
12. How might the regulatory landscape adapt to support ethical hacking initiatives?
Answer: Enacting explicit legal “safe harbor” protections for good-faith security researchers operating within published bug bounty frameworks and security disclosure policies.
Numerical Engineering Problems & Solutions
Problem 1: Penetration Testing Efficiency & Time Saved
An ethical hacking team performs 3 penetration tests per week, taking 40 hours per test (120 total hours). A new automated scanning tool cuts test execution duration by 30%. Calculate new hours per test, new total weekly hours, and weekly hours saved.
An ethical hacking team performs 3 penetration tests per week, taking 40 hours per test (120 total hours). A new automated scanning tool cuts test execution duration by 30%. Calculate new hours per test, new total weekly hours, and weekly hours saved.
Solution:
- Baseline weekly total = 3 tests × 40 hours = 120 hours/week
- Time reduction per test = 40 hours × 0.30 = 12 hours saved/test
- New execution time per test = 40 – 12 = 28 hours/test
- New weekly total hours = 3 × 28 hours = 84 hours/week
- Weekly time saved = 120 – 84 = 36 hours saved/week
Problem 2: Vulnerability Scanner Network Processing Time
A vulnerability scanner processes 500 IP addresses per hour across a target network of 10,000 IP addresses. Calculate total scan time in hours. If scanner throughput efficiency increases by 50% (750 IPs/hour), calculate new total scan time.
A vulnerability scanner processes 500 IP addresses per hour across a target network of 10,000 IP addresses. Calculate total scan time in hours. If scanner throughput efficiency increases by 50% (750 IPs/hour), calculate new total scan time.
Solution:
- Initial scan duration = 10,000 IPs / 500 IPs/hour = 20 hours
- New throughput rate = 500 × 1.50 = 750 IPs/hour
- New scan duration = 10,000 / 750 ≈ 13.33 hours (13 hours and 20 minutes)
- Time saved = 20 – 13.33 = 6.67 hours saved
Problem 3: Vulnerability Severity Score Reduction
A penetration test uncovers vulnerabilities with a baseline average CVSS severity score of 7.0 out of 10. Patching critical findings lowers the average severity score by 20%. Calculate absolute score reduction and new average severity score.
A penetration test uncovers vulnerabilities with a baseline average CVSS severity score of 7.0 out of 10. Patching critical findings lowers the average severity score by 20%. Calculate absolute score reduction and new average severity score.
Solution:
- Absolute score reduction = 7.0 × 0.20 = 1.4 points reduction
- New average severity score = 7.0 – 1.4 = 5.6 out of 10
Problem 4: Multi-Phase Vulnerability Remediation Tracking
A security audit identifies 120 vulnerabilities. Phase 1 remediation fixes 75% of all vulnerabilities. Phase 2 fixes 50% of the remaining vulnerabilities. Calculate vulnerabilities fixed in Phase 1, remaining after Phase 1, fixed in Phase 2, and final remaining count.
A security audit identifies 120 vulnerabilities. Phase 1 remediation fixes 75% of all vulnerabilities. Phase 2 fixes 50% of the remaining vulnerabilities. Calculate vulnerabilities fixed in Phase 1, remaining after Phase 1, fixed in Phase 2, and final remaining count.
Solution:
- Phase 1 fixed = 120 × 0.75 = 90 vulnerabilities fixed
- Remaining after Phase 1 = 120 – 90 = 30 vulnerabilities
- Phase 2 fixed = 30 × 0.50 = 15 vulnerabilities fixed
- Final remaining vulnerabilities = 30 – 15 = 15 vulnerabilities
Problem 5: Cumulative Vulnerability Discovery Output
A Red Team works 5 days a week, 8 hours per day, discovering an average of 2 vulnerabilities per hour. Calculate weekly discovery volume, monthly volume (4 weeks), and annual discovery volume (52 weeks).
A Red Team works 5 days a week, 8 hours per day, discovering an average of 2 vulnerabilities per hour. Calculate weekly discovery volume, monthly volume (4 weeks), and annual discovery volume (52 weeks).
Solution:
- Daily discoveries = 8 hours × 2 vulnerabilities/hour = 16 vulnerabilities/day
- Weekly discoveries = 16 × 5 days = 80 vulnerabilities/week
- Monthly discoveries = 80 × 4 weeks = 320 vulnerabilities/month
- Annual discoveries = 80 × 52 weeks = 4,160 vulnerabilities/year
Problem 6: Calculating Breach Cost Savings and Penetration Test ROI
An enterprise spends $20,000 on an annual penetration test. The test identifies flaws that reduce annual data breaches from 10 down to 3 incidents. Each breach costs $25,000. Calculate annual breach cost savings, net financial benefit, and Return on Investment (ROI).
An enterprise spends $20,000 on an annual penetration test. The test identifies flaws that reduce annual data breaches from 10 down to 3 incidents. Each breach costs $25,000. Calculate annual breach cost savings, net financial benefit, and Return on Investment (ROI).
Solution:
- Breaches prevented = 10 – 3 = 7 breaches saved/year
- Gross annual breach savings = 7 × $25,000 = $175,000/year
- Net benefit = $175,000 – $20,000 (test cost) = $155,000
- ROI percentage = ($155,000 / $20,000) × 100 = 775.0%
Problem 7: Extension Yield Calculation for Penetration Testing
A 10-day penetration test (6 hours/day = 60 hours total) yields 50 vulnerabilities (0.833 vulnerabilities/hour). Extending the engagement duration by 20% maintains the exact same discovery rate. Calculate new duration in days, new total testing hours, and total vulnerabilities discovered.
A 10-day penetration test (6 hours/day = 60 hours total) yields 50 vulnerabilities (0.833 vulnerabilities/hour). Extending the engagement duration by 20% maintains the exact same discovery rate. Calculate new duration in days, new total testing hours, and total vulnerabilities discovered.
Solution:
- New testing duration = 10 days × 1.20 = 12 days
- New total testing hours = 12 days × 6 hours/day = 72 hours
- Vulnerability rate per day = 50 / 10 = 5 vulnerabilities/day
- Total vulnerabilities discovered = 12 days × 5 vulnerabilities/day = 60 vulnerabilities
Problem 8: Log Analytics Processing Throughput
A log parsing script processes 1,000 log entries per minute over a 3-hour continuous run (180 minutes). Calculate initial logs processed. An algorithm optimization improves processing efficiency by 40% (1,400 logs/min). Calculate new total logs processed in the same 3-hour window.
A log parsing script processes 1,000 log entries per minute over a 3-hour continuous run (180 minutes). Calculate initial logs processed. An algorithm optimization improves processing efficiency by 40% (1,400 logs/min). Calculate new total logs processed in the same 3-hour window.
Solution:
- Total run duration in minutes = 3 hours × 60 = 180 minutes
- Original logs processed = 1,000 × 180 = 180,000 log entries
- New processing throughput = 1,000 × 1.40 = 1,400 log entries/min
- New total logs processed = 1,400 × 180 = 252,000 log entries
Problem 9: Incident Response Mitigation Success Rate Increase
A SOC mitigates incident breaches with an 85% success rate across 40 annual incidents (34 successful mitigations). Hands-on Red Team training raises mitigation success rate to 95%. Calculate pre-training mitigations, post-training mitigations, and additional successful mitigations.
A SOC mitigates incident breaches with an 85% success rate across 40 annual incidents (34 successful mitigations). Hands-on Red Team training raises mitigation success rate to 95%. Calculate pre-training mitigations, post-training mitigations, and additional successful mitigations.
Solution:
- Pre-training successful mitigations = 40 × 0.85 = 34 incidents
- Post-training successful mitigations = 40 × 0.95 = 38 incidents
- Net additional incidents mitigated = 38 – 34 = 4 additional incidents
Problem 10: Financial Payback Period for an Ethical Hacking Program
An ethical hacking program costs $50,000 annually. The program reduces annual breach occurrences from 10 down to 3 incidents. Each breach incurs $25,000 in recovery costs. Calculate pre-program annual loss, post-program annual loss, annual savings, and program payback period in years.
An ethical hacking program costs $50,000 annually. The program reduces annual breach occurrences from 10 down to 3 incidents. Each breach incurs $25,000 in recovery costs. Calculate pre-program annual loss, post-program annual loss, annual savings, and program payback period in years.
Solution:
- Pre-program annual loss = 10 × $25,000 = $250,000/year
- Post-program annual loss = 3 × $25,000 = $75,000/year
- Annual gross savings = $250,000 – $75,000 = $175,000/year
- Payback period = $50,000 / $175,000 ≈ 0.2857 years (approx. 3.4 months)
Problem 11: System Vulnerability Remediation Breakdown
A simulation finds 60% of 200 tested systems vulnerable (120 vulnerable systems). Deploying an emergency patch fixes 80% of identified vulnerable systems. Calculate initial vulnerable systems, systems patched, and remaining vulnerable systems.
A simulation finds 60% of 200 tested systems vulnerable (120 vulnerable systems). Deploying an emergency patch fixes 80% of identified vulnerable systems. Calculate initial vulnerable systems, systems patched, and remaining vulnerable systems.
Solution:
- Initial vulnerable systems = 200 × 0.60 = 120 systems
- Systems patched = 120 × 0.80 = 96 systems fixed
- Remaining vulnerable systems = 120 – 96 = 24 systems
Problem 12: Time Saved via Automated Security Testing Scripts
Manual security testing requires 200 hours per month. Developing automated testing scripts cuts manual testing effort by 35%. Calculate new monthly testing hours required, monthly hours saved, and total annual hours saved (12 months).
Manual security testing requires 200 hours per month. Developing automated testing scripts cuts manual testing effort by 35%. Calculate new monthly testing hours required, monthly hours saved, and total annual hours saved (12 months).
Solution:
- Monthly hours saved = 200 hours × 0.35 = 70 hours saved/month
- New monthly testing hours required = 200 – 70 = 130 hours/month
- Total annual hours saved = 70 hours × 12 months = 840 hours/year
Ethical Hacking and Penetration Testing — Summary & Wrap-Up
Ethical hacking and penetration testing provide essential offensive validation for enterprise security strategies. By conducting authorized simulations, adhering to strict Rules of Engagement, utilizing specialized exploit frameworks, and delivering actionable technical reports, security testers empower organizations to identify and remediate vulnerabilities before real-world adversaries exploit them.