
Threat Intelligence Education is an education in meaning: how to move from scattered signals to conclusions that can guide action. The diagram shows this conversion clearly. Learners begin with inputs—curated resources, baseline security knowledge, and realistic examples—then work within controls such as collection standards and analytical frameworks that prevent “interesting data” from becoming unreliable speculation. Mechanisms like expert guidance and exposure to threat feeds create a practical setting where students can practice the essential cycle: collect, filter, enrich, compare, and interpret. What emerges as output is not noise, but intelligence products—briefs, indicators, hypotheses, and recommendations that help teams prioritize risk, spot campaigns, and respond earlier. In this sense, the function at the center is a kind of disciplined translation: translating raw information into decisions that a security team can actually trust.
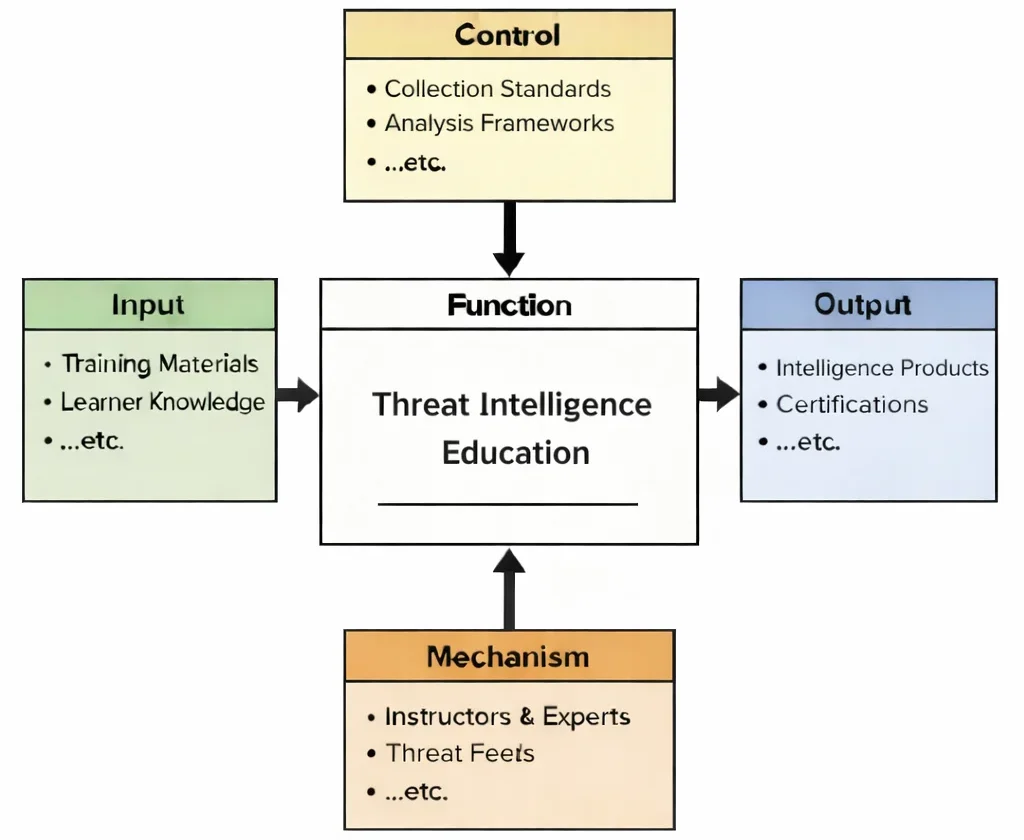
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Threat Intelligence Education as a structured transformation process. Inputs include training materials and learner knowledge. Controls include collection standards, analysis frameworks, and related guidance that shape how information is gathered, validated, and interpreted. Mechanisms include instructors and experts, along with access to threat feeds and practice environments that support hands-on work. Outputs include intelligence products and learner credentials, reflecting the ability to convert raw signals into actionable insight for security operations and decision-making.
Interactive Check: Intro & System Concepts
Verify your understanding of how raw telemetry is converted into validated intelligence products:
Introductory Concept Verification
1. Why is Threat Intelligence described as a “disciplined translation” rather than just collecting interesting data?
Answer: Raw telemetry and indicator feeds are filled with noise and unverified speculation. Collection standards and analysis frameworks act as controls to filter, enrich, and validate signals, transforming scattered data into actionable intelligence products (briefs, hypotheses, and indicators) that security teams can trust to prioritize risk.
2. What constitutes the primary operational output of Threat Intelligence Education?
Answer: Actionable intelligence products and analytical competence: learners who can execute the collect-filter-enrich-interpret cycle to spot adversary campaigns and guide security operations earlier in the attack lifecycle.
Threat Intelligence serves as a cornerstone in modern cybersecurity practices by providing actionable insights about potential and existing threats. It involves collecting, analyzing, and contextualizing data from various sources to anticipate cyberattacks and develop informed defense strategies. This proactive approach complements traditional application security and cloud security measures by enabling organizations to stay ahead of malicious actors through intelligence-led decision-making.
A key dimension of threat intelligence is integrating AI and ML in cybersecurity to identify patterns in massive data sets, facilitating faster and more accurate threat detection. The intelligence gathered is crucial in refining incident response and forensics operations, allowing teams to trace the origins of an attack and understand its scope. Effective analysis also relies on secure data gathering practices underpinned by cryptography to ensure data integrity.
Threat intelligence is relevant across domains—from industrial systems secured under Operational Technology (OT) Security to highly dynamic environments addressed in endpoint security. It also informs risk assessments that guide cybersecurity policies and compliance strategies. These insights are vital for sectors handling critical infrastructure and cyber-physical systems (CPS), where breaches could result in significant physical and economic damage.
Beyond technical implementation, building a strong culture of cybersecurity awareness ensures that individuals can interpret intelligence indicators and react responsibly. Ethical hacking plays a complementary role, simulating attacks to test how threat intelligence informs defense readiness. Meanwhile, access governance through identity and access management ensures that only authorized users interact with sensitive systems.
In fast-evolving threat landscapes, emerging areas in cybersecurity like zero-trust architectures and adversarial AI must be continuously monitored. Threat intelligence helps anticipate shifts, while network security protocols adjust dynamically based on intelligence alerts. These adaptations are increasingly powered by data science and analytics, which translate raw threat data into usable insights.
The data pipeline supporting threat intelligence involves data collection and storage, data cleaning and preprocessing, and advanced data analysis. These steps make it possible to extract trends from both structured and unstructured information. Insights are often delivered through intuitive data visualization tools that help security teams grasp and act on threats quickly.
To refine these insights, security professionals often apply domain-specific analytics tailored to unique operational environments. The effectiveness of such analytics hinges on the appropriate use of tools and technologies in data science. While automation enhances efficiency, ethical considerations must be addressed, particularly in how threat intelligence data is collected and used, as highlighted in ethical and social aspects of analytics.
The rise of advanced persistent threats (APTs) and cyber-espionage has elevated the importance of threat intelligence as a strategic asset. Organizations must integrate it with every layer of their security infrastructure to prevent, detect, and neutralize attacks. As the digital domain grows more complex, threat intelligence remains essential for anticipating and countering the next wave of cyber risks.
This image portrays threat intelligence as a process of “zooming in” on a complex global threat landscape. At the center, a magnifying glass over the Earth symbolizes investigation, attribution, and pattern-finding across regions and networks. Around it, warning triangles, hazard symbols, and digital icons suggest indicators of compromise, malware families, phishing campaigns, and attacker tactics. Analysts seated at multiple monitors represent security teams correlating data from logs, feeds, and reports, while dashboard charts and radar-like graphics imply continuous monitoring and prioritization. The colorful ringed platform beneath the globe conveys layered visibility—bringing many weak signals into a clearer, organized picture. Overall, the artwork communicates that threat intelligence helps organisations anticipate attacks, focus defenses, and respond faster with better context.
Building Cyber Resilience: Threat Intelligence Navigation
Discover how Threat Intelligence correlates Indicators of Compromise (IoCs), maps adversary TTPs, and analyzes malware binaries across the Cybersecurity cluster. Each card details threat hunting, MITRE ATT&CK frameworks, STIX/TAXII feeds, and reverse engineering.
Cybersecurity Overview
Presents the overall system architecture, mapping how strategic and technical threat intelligence feeds direct proactive enterprise defense-in-depth postures.
Network Security
Examines blocking malicious C2 command-and-control IP addresses and suspicious domain blacklists at perimeter firewalls based on live intelligence feeds.
Application Security
Focuses on tracking zero-day web exploits (CVEs), prioritizing vulnerability patch backlogs, and defending APIs against active exploit campaigns.
Cloud Security
Details monitoring cloud control-plane telemetry for IOC matches, tracking threat actor groups targeting misconfigured cloud storage, and IAM token theft.
Endpoint Security
Covers ingesting file hashes (SHA-256) into EDR agents to automatically block executing malware binaries and stop zero-day ransomware variants.
Identity & Access Management
Governs credential stuffing defense, tracking leaked corporate credentials on dark web forums, and forcing automated password resets for compromised accounts.
Cryptography
Applies cryptographic hash validation for malware sample integrity and analyzes proprietary encryption algorithms utilized by advanced ransomware syndicates.
Incident Response & Forensics
Orchestrates rapid IOC correlation during active breaches, establishing adversary attribution and reconstructing attacker lateral movement timelines.
Threat Intelligence
Focuses on threat hunting, MITRE ATT&CK adversary frameworks, STIX/TAXII machine-readable sharing, static/dynamic malware analysis, and dark web monitoring.
Ethical Hacking & Pen Testing
Utilizes threat intelligence reports to construct realistic red-team adversary emulation scenarios, testing whether security controls detect specific APT campaigns.
Cybersecurity Awareness
Translates active phishing lure campaigns and social engineering TTPs into timely awareness training updates and simulated phishing tests.
Policy & Governance
Informs risk assessment models, regulatory reporting requirements, and enterprise security policy updates based on evolving macroeconomic threat landscapes.
CPS Security
Protects cyber-physical infrastructure by tracking threat actor campaigns targeting smart grids, water treatment pumps, and automated manufacturing lines.
OT Security
Secures industrial control environments by monitoring ICS-specific malware signatures (Industroyer, Triton) and SCADA protocol anomalies.
AI & ML in Security
Leverages machine learning to correlate massive multi-source threat feeds, identify hidden behavioral anomalies, and automate indicator enrichment.
Emerging Areas
Investigates dark web AI exploit development, post-quantum cryptographic intelligence, and emerging Web3 decentralized finance threat vectors.
Key Topics in Threat Intelligence
Proactive frameworks and analytical methodologies for anticipating cyber threats:
Threat Hunting and Analysis
- Proactive Hunting: Hypothesis-driven and data-driven searches for hidden compromises across network logs and endpoint telemetry before alerts fire.
- Indicators of Compromise (IoCs): Tracking malicious IP addresses, file hashes, and C2 domains using SIEM platforms (Splunk, QRadar, Elastic Security).
Cyber Threat Intelligence Frameworks
- MITRE ATT&CK: Mapping observed adversary Tactics, Techniques, and Procedures (TTPs) to a standardized knowledge base.
- Diamond Model & Kill Chain: Structuring adversary-victim relationships and attack lifecycles to disrupt operations.
- STIX/TAXII: Exchanging machine-readable intelligence feeds collaboratively across organizations.
Malware Analysis and Reverse Engineering
- Static Analysis: Inspecting file properties and code strings in sandboxed or offline environments.
- Dynamic Analysis: Executing malware in controlled sandboxes (Cuckoo Sandbox, VirusTotal) to observe C2 traffic and API calls.
Applications of Threat Intelligence
Practical deployment of intelligence in operational security:
Identifying Emerging Threats and Vulnerabilities
- Tracking CVE disclosures and monitoring dark web forums for leaked credentials and zero-day exploit chatter.
Strengthening Organizational Defenses Based on Threat Insights
- Updating firewall rules, refining SIEM detection logic, and tailoring employee awareness campaigns around active phishing campaigns.
Emerging Trends in Threat Intelligence
Advanced methodologies shaping the future of intelligence operations:
- AI-Powered Threat Correlation: Automating multi-source feed aggregation and anomaly identification using machine learning (Darktrace).
- Real-Time Intelligence Feeds: Integrating continuous commercial feeds (Recorded Future, CrowdStrike) for instant operational action.
- Collaborative ISACs: Sharing sector-specific intelligence across financial, healthcare, and energy Information Sharing and Analysis Centers.
Why Study Threat Intelligence
Mastering threat intelligence equips security professionals to anticipate attacks before they strike:
- Strategic Foresight: Teaches analysts to understand adversary motives, campaign patterns, and TTPs rather than reacting blindly to alerts.
- Data Collection & Filtering: Provides practical experience in filtering noise, validating OSINT sources, and utilizing Threat Intelligence Platforms (TIPs).
- Proactive Defense: Informs vulnerability management, risk assessments, and incident response planning with real-world threat data.
Interactive Quick Review: Threat Intelligence Concepts
Reinforce key concepts regarding IoCs, TTPs, and threat intelligence frameworks before reading the FAQ:
Quick Review Verification
1. What is the key operational distinction between an Indicator of Compromise (IoC) and a TTP (Tactics, Techniques, and Procedures)?
Answer: An IoC is a specific, observable technical artifact (such as a file hash or IP address) that is easily changed by attackers. A TTP describes *how* attackers operate behaviorally (such as credential dumping or lateral movement via WMI), which is much harder for adversaries to alter quickly and provides more durable detection value.
2. How does the MITRE ATT&CK framework assist security analysts during an investigation?
Answer: MITRE ATT&CK provides a standardized taxonomy of real-world adversary behaviors. Analysts map observed log anomalies to specific techniques, allowing them to understand the attacker’s methodology, anticipate next steps, and build robust behavioral detection rules.
Threat Intelligence – Frequently Asked Questions
What is threat intelligence in cybersecurity?
Threat intelligence is the collection, analysis, and contextualization of data regarding existing or emerging cyber threats, turning raw indicators into actionable defensive insights.
What are the main types of threat intelligence?
Strategic (high-level trends for executives), Tactical (adversary TTPs for defenders), Operational (specific active campaigns), and Technical (concrete IoCs like IP hashes for blocking).
How are STIX and TAXII used in threat intelligence sharing?
STIX provides a standardized, machine-readable language for describing threat data, while TAXII is the transport protocol used to securely exchange STIX feeds between organizations.
What is the difference between static and dynamic malware analysis?
Static analysis examines malware code properties without execution (strings, headers). Dynamic analysis executes the malware in an isolated sandbox (Cuckoo) to observe runtime behavior and C2 traffic.
What challenges do security teams face with threat feeds?
Data overload from noisy or outdated feeds, ensuring intelligence relevance to the organization’s specific asset profile, and integrating feeds smoothly into SIEM/EDR tools.
How does threat hunting differ from standard security monitoring?
Standard monitoring relies on automated alert rules to catch known attacks. Threat hunting is a proactive, analyst-driven search through historical telemetry to uncover sophisticated hidden compromises.
Threat Intelligence: Conclusion
Threat intelligence is a vital component of modern cybersecurity, enabling organizations to stay ahead of adversaries and protect their assets proactively. By integrating threat intelligence into security operations, organizations can build a robust and adaptive defense against evolving cyber threats.
- Actionable Insight: Filter and enrich raw telemetry into reliable, decision-grade intelligence products.
- Behavioral Detection: Focus on MITRE ATT&CK TTPs rather than easily evaded single Indicators of Compromise.
- Proactive Defense: Use threat hunting and dynamic malware analysis to anticipate adversary campaigns before incidents occur.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is threat intelligence and how does it support cybersecurity strategies?
Answer: Threat intelligence is the collection, analysis, and dissemination of data about cyber threats to enable proactive defense. It supports strategies by providing actionable insights that anticipate and mitigate attacks.
2. How do threat intelligence feeds contribute to effective cyber defense?
Answer: They deliver real-time data on emerging threats and vulnerabilities directly to security systems, enabling rapid detection and response.
3. What are the key components of a comprehensive threat intelligence program?
Answer: Data collection, rigorous analysis, intelligence dissemination, and seamless integration with existing security operations (SIEM, EDR).
4. How does data analysis enhance the value of threat intelligence?
Answer: It transforms raw data into strategic insight by identifying behavior patterns, trends, and anomalies in cyber threat activity.
5. Why is real-time threat intelligence critical for incident response?
Answer: It provides immediate awareness of active attacks, enabling swift containment, reducing adversary dwell time, and minimizing operational impact.
6. How do threat intelligence tools integrate with security operations centers (SOCs)?
Answer: By feeding real-time IOCs and alerts directly into SIEM platforms, allowing analysts to correlate threat data with internal events automatically.
7. What challenges do organizations face in collecting and utilizing threat intelligence?
Answer: Data overload from noisy feeds, ensuring relevance to specific enterprise asset profiles, data accuracy validation, and tool integration complexity.
8. How can proactive threat intelligence improve an organization’s overall security posture?
Answer: By enabling anticipatory actions (threat hunting, patching KEV vulnerabilities) rather than reactive scrambling after an intrusion occurs.
9. What is the role of collaboration in effective threat intelligence sharing?
Answer: Pooling threat telemetry across ISACs and industry peers builds a collective defense, accelerating the distribution of actionable intelligence globally.
10. How can organizations measure the success of their threat intelligence initiatives?
Answer: Tracking incident detection rates, reduced dwell times, volume of actionable insights, and reduction in successful cyber attacks over time.
Thought-Provoking Architectural Questions
1. How will the integration of AI and machine learning redefine the future of threat intelligence?
Answer: AI will autonomously ingest, cluster, and enrich petabytes of multi-source threat data, spotting zero-day campaign patterns at machine speed.
2. In what ways can threat intelligence be used to predict and prevent future cyber attacks?
Answer: By analyzing adversary prepositioning, pre-attack reconnaissance chatter on dark web forums, and exploiting trending exploit vectors before targets are breached.
3. What are the ethical implications of collecting and using threat intelligence data?
Answer: Monitoring dark web forums and collecting intelligence can inadvertently scrape private PII or cross legal surveillance boundaries, requiring strict data minimization.
4. How can cross-industry collaboration enhance the quality and effectiveness of threat intelligence?
Answer: Sharing sector-specific attack data via STIX/TAXII allows organizations in finance, energy, and healthcare to defend against coordinated multi-sector APT campaigns.
5. What role does continuous monitoring play in maintaining an effective threat intelligence program?
Answer: Continuous network telemetry monitoring supplies the internal context required to match external threat feed indicators against live enterprise traffic.
6. How might the increasing use of cloud services impact threat intelligence operations?
Answer: Cloud-native multi-tenant environments require intelligence platforms to ingest cloud control-plane API logs and track threat actors targeting cloud misconfigurations.
7. What are the potential limitations of automated threat intelligence systems?
Answer: High false positive rates from unvetted feeds, lack of contextual business understanding, and susceptibility to adversarial data poisoning.
8. How can threat intelligence be integrated into broader cybersecurity frameworks?
Answer: By embedding threat intelligence directly into SIEM detection rules, firewall blocking policies, vulnerability management SLAs, and incident response playbooks.
9. What role does threat intelligence play in executive-level strategic decision-making?
Answer: Informs board-level risk management, capital budgeting for security controls, cyber insurance policy terms, and mergers and acquisitions (M&A) risk due diligence.
10. How might the evolution of threat intelligence impact cyber warfare and national security?
Answer: Enables sovereign nation-states to conduct rapid attribution of state-sponsored cyber attacks and execute coordinated preemptive defensive cyber operations.
11. What are the benefits and risks of open-source intelligence versus commercial feeds?
Answer: OSINT offers cost-free community data but high noise and variable quality; commercial feeds offer curated, high-confidence attribution but incur significant subscription expenses.
12. How can organizations future-proof their threat intelligence programs?
Answer: By adopting flexible TIP architectures, embracing machine learning log enrichment, investing in skilled threat hunting analysts, and participating in automated STIX/TAXII sharing ISACs.
Numerical Engineering Problems & Solutions
Problem 1: Confirmed Threat Volume from High-Volume Intelligence Feeds
A threat intelligence platform collects 10,000,000 data points per day. Telemetry indicates that 0.01% (0.0001) of these data points indicate confirmed threats. Calculate confirmed threats per day, per month (30 days), and per year (365 days).
A threat intelligence platform collects 10,000,000 data points per day. Telemetry indicates that 0.01% (0.0001) of these data points indicate confirmed threats. Calculate confirmed threats per day, per month (30 days), and per year (365 days).
Solution:
- Confirmed threats per day = 10,000,000 × 0.0001 = 1,000 confirmed threats/day
- Confirmed threats per month (30 days) = 1,000 × 30 = 30,000 threats/month
- Confirmed threats per year (365 days) = 1,000 × 365 = 365,000 threats/year
Problem 2: Annual Breach Cost Savings from Threat Intelligence Systems
A company invests $100,000 in a threat intelligence system that reduces breach incidents by 70%. Baseline breach frequency was 20 incidents per year at $50,000 per breach ($1,000,000 annual loss). Calculate annual breach cost before and after implementation, and net annual savings.
A company invests $100,000 in a threat intelligence system that reduces breach incidents by 70%. Baseline breach frequency was 20 incidents per year at $50,000 per breach ($1,000,000 annual loss). Calculate annual breach cost before and after implementation, and net annual savings.
Solution:
- Annual breach cost before = 20 breaches × $50,000 = $1,000,000/year
- Breaches prevented = 20 × 0.70 = 14 breaches saved/year
- Remaining breaches per year = 20 – 14 = 6 breaches
- Annual breach cost after = 6 × $50,000 = $300,000/year
- Net annual savings = $1,000,000 – $300,000 (loss) – $100,000 (system cost) = $600,000 net savings
Problem 3: Commercial Threat Feed Cost per Confirmed Threat
A commercial threat feed costs $0.0005 per data point and delivers 15,000,000 data points per month. Calculate monthly feed cost and annual feed cost. If 0.005% (0.00005) of data points are confirmed threats, calculate annual confirmed threats and cost per confirmed threat.
A commercial threat feed costs $0.0005 per data point and delivers 15,000,000 data points per month. Calculate monthly feed cost and annual feed cost. If 0.005% (0.00005) of data points are confirmed threats, calculate annual confirmed threats and cost per confirmed threat.
Solution:
- Monthly feed cost = 15,000,000 data points × $0.0005 = $7,500/month
- Annual feed cost = $7,500 × 12 months = $90,000/year
- Confirmed threats per month = 15,000,000 × 0.00005 = 750 threats/month
- Annual confirmed threats = 750 × 12 = 9,000 threats/year
- Cost per confirmed threat = $90,000 / 9,000 threats = $10.00 per confirmed threat
Problem 4: Detection Accuracy Gain Across Monthly Threat Events
A threat intelligence system upgrades its detection accuracy from 90% (0.90) to 98% (0.98) across a baseline volume of 500 threat events per month. Calculate threats detected at 90% accuracy, threats detected at 98% accuracy, and net additional threats detected monthly.
A threat intelligence system upgrades its detection accuracy from 90% (0.90) to 98% (0.98) across a baseline volume of 500 threat events per month. Calculate threats detected at 90% accuracy, threats detected at 98% accuracy, and net additional threats detected monthly.
Solution:
- Threats detected at 90% accuracy = 500 × 0.90 = 450 threats detected
- Threats detected at 98% accuracy = 500 × 0.98 = 490 threats detected
- Net additional threats detected = 490 – 450 = 40 additional threats detected monthly
Problem 5: Incident Response Triage Time Acceleration
A security team reduces incident response triage time from 40 minutes down to 25 minutes per incident using threat intelligence enrichment. For an organization handling 100 incidents per year, calculate time saved per incident and total annual time saved in minutes and hours.
A security team reduces incident response triage time from 40 minutes down to 25 minutes per incident using threat intelligence enrichment. For an organization handling 100 incidents per year, calculate time saved per incident and total annual time saved in minutes and hours.
Solution:
- Time saved per incident = 40 min – 25 min = 15 minutes saved/incident
- Total annual time saved in minutes = 100 incidents × 15 minutes = 1,500 minutes/year
- Convert minutes to hours = 1,500 / 60 = 25.0 hours saved per year
Problem 6: Threat Log Ingestion and Processing Volume Metrics
An organization processes 250,000 threat logs per day. Telemetry indicates that 0.2% (0.002) are confirmed threats. Calculate threat logs per day, weekly (7 days), and annual (365 days).
An organization processes 250,000 threat logs per day. Telemetry indicates that 0.2% (0.002) are confirmed threats. Calculate threat logs per day, weekly (7 days), and annual (365 days).
Solution:
- Threat logs per day = 250,000 × 0.002 = 500 threat logs/day
- Threat logs per week (7 days) = 500 × 7 = 3,500 threat logs/week
- Threat logs per year (365 days) = 500 × 365 = 182,500 threat logs/year
Problem 7: Phishing Email Reporting Rate Improvement
A phishing detection awareness program improves employee suspicious email reporting rates from 10% (0.10) to 25% (0.25) across a daily email volume of 200,000 emails. Calculate daily reports before and after improvement, and net additional reports per day.
A phishing detection awareness program improves employee suspicious email reporting rates from 10% (0.10) to 25% (0.25) across a daily email volume of 200,000 emails. Calculate daily reports before and after improvement, and net additional reports per day.
Solution:
- Daily reports before training = 200,000 × 0.10 = 20,000 emails reported/day
- Daily reports after training = 200,000 × 0.25 = 50,000 emails reported/day
- Net additional reports = 50,000 – 20,000 = 30,000 additional reports/day
Problem 8: Vulnerability Scanner Throughput & Acceleration
A vulnerability scanner processes 600 devices in 3 hours (180 minutes), resulting in 0.3 minutes per device. Calculate time required to scan 3,000 devices. Calculate new scan duration and time saved if scanning speed increases by 40% (1.4x throughput).
A vulnerability scanner processes 600 devices in 3 hours (180 minutes), resulting in 0.3 minutes per device. Calculate time required to scan 3,000 devices. Calculate new scan duration and time saved if scanning speed increases by 40% (1.4x throughput).
Solution:
- Time required to scan 3,000 devices = 3,000 devices × 0.3 minutes/device = 900 minutes (15 hours)
- New scan duration with 40% speed increase = 900 minutes / 1.40 ≈ 642.86 minutes (approx. 10.71 hours)
- Time saved = 900 – 642.86 ≈ 257.14 minutes saved (approx. 4.29 hours)
Problem 9: Alert Noise Reduction via Threat Intelligence Filtering
A SIEM network receives 4,000 threat alerts per day. A threat intelligence filtering system reduces alert noise by 60%. Calculate remaining daily alerts and total annual alert reduction (365 days).
A SIEM network receives 4,000 threat alerts per day. A threat intelligence filtering system reduces alert noise by 60%. Calculate remaining daily alerts and total annual alert reduction (365 days).
Solution:
- Alerts eliminated per day = 4,000 × 0.60 = 2,400 alerts/day
- Remaining daily alerts = 4,000 – 2,400 = 1,600 alerts/day
- Total annual alert reduction = 2,400 alerts/day × 365 days = 876,000 alerts reduced/year
Problem 10: Threat Intelligence Platform Availability & Downtime Calculation
A threat intelligence platform operates 24/7 with an availability uptime of 99.95%. Calculate total annual operating minutes (365 days) and total annual downtime in minutes.
A threat intelligence platform operates 24/7 with an availability uptime of 99.95%. Calculate total annual operating minutes (365 days) and total annual downtime in minutes.
Solution:
- Total annual operating minutes = 365 days × 24 hours × 60 minutes = 525,600 minutes/year
- Downtime percentage = 100% – 99.95% = 0.05% (0.0005)
- Total annual downtime in minutes = 525,600 minutes × 0.0005 = 262.8 minutes/year
Problem 11: Multi-Source Threat Feed Aggregation Metrics
A threat intelligence platform aggregates data from 40 separate sources, each providing 100,000 data points per month. Calculate total monthly data points. If 0.01% (0.0001) of aggregated data points are confirmed threats, calculate confirmed threats and threat percentage.
A threat intelligence platform aggregates data from 40 separate sources, each providing 100,000 data points per month. Calculate total monthly data points. If 0.01% (0.0001) of aggregated data points are confirmed threats, calculate confirmed threats and threat percentage.
Solution:
- Total monthly data points = 40 sources × 100,000 points/source = 4,000,000 data points/month
- Confirmed threats = 4,000,000 × 0.0001 = 400 confirmed threats/month
- Threat percentage = (400 / 4,000,000) × 100 = 0.01%
Problem 12: Threat Intelligence Investment ROI Calculation
A threat intelligence investment costs $300,000 and reduces breach incidents by 80% from a baseline average of 12 breaches per year. Each breach costs $100,000. Calculate annual breach cost before and after, annual savings, and Return on Investment (ROI) percentage.
A threat intelligence investment costs $300,000 and reduces breach incidents by 80% from a baseline average of 12 breaches per year. Each breach costs $100,000. Calculate annual breach cost before and after, annual savings, and Return on Investment (ROI) percentage.
Solution:
- Annual breach cost before = 12 breaches × $100,000 = $1,200,000/year
- Remaining breaches after 80% reduction = 12 × (1 – 0.80) = 12 × 0.20 = 2.4 (approx. 2 breaches)
- Annual breach cost after = 2 breaches × $100,000 = $200,000/year
- Annual gross savings = $1,200,000 – $200,000 = $1,000,000/year
- ROI percentage = ($1,000,000 / $300,000 investment) × 100 ≈ 333.33%
Threat Intelligence — Summary & Wrap-Up
Threat intelligence transforms raw telemetry, dark web chatter, and multi-source feed indicators into decision-grade defensive insight. By operationalizing threat hunting, mapping adversary TTPs to the MITRE ATT&CK framework, analyzing malware binaries via static and dynamic sandboxing, and integrating actionable feeds directly into SIEM/EDR platforms, security teams move from reactive firefighting to proactive, intelligence-led cyber defense.