
Network Security in Cybersecurity Education teaches an often-overlooked truth: most attacks are not “mystical”—they are simply traffic finding the easiest path. The diagram captures how learners are trained to close those paths thoughtfully. Inputs (resources, examples, foundational knowledge) enter the learning process, but they are shaped by controls that impose discipline: policies, standards, and rules that define what must be protected and what “good security” looks like in practice. Mechanisms—expert guidance and networking tools—turn abstract ideas into concrete skill: mapping network boundaries, segmenting systems, controlling flows, and reading network behavior through logs and signals. The output is a learner who can design connectivity without surrendering control—someone who understands that a secure network is not a single device or a single setting, but a coherent set of choices that make communication reliable for users and costly for attackers.
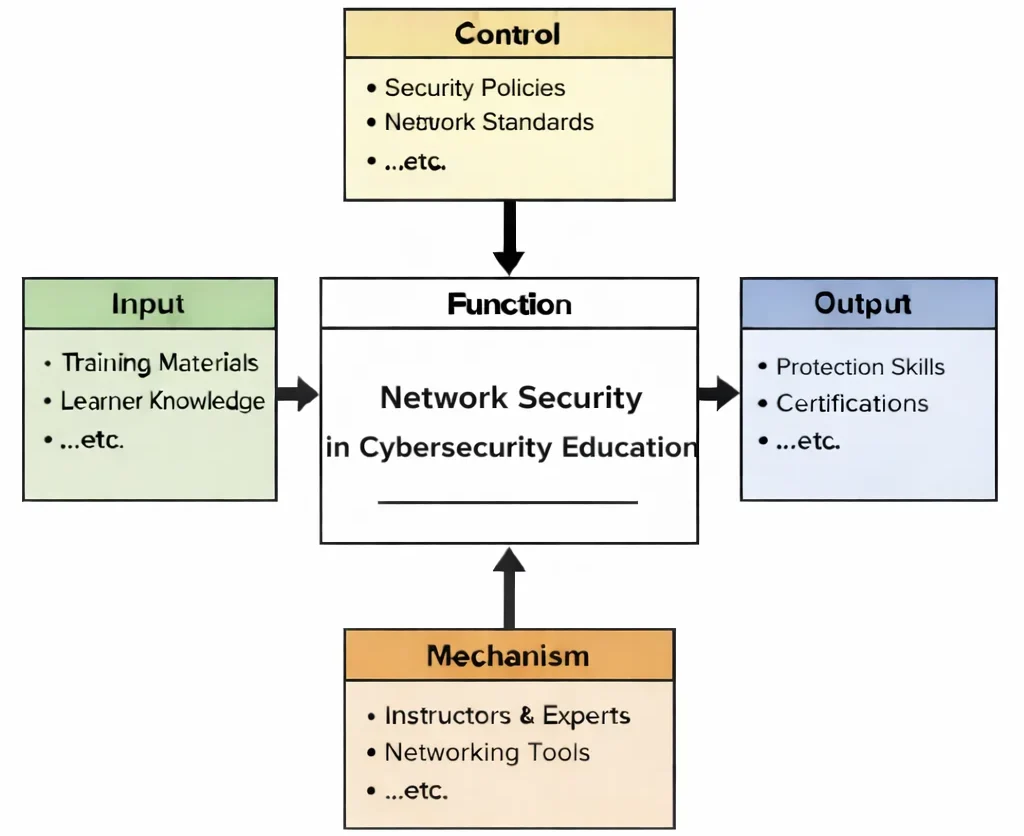
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Network Security in Cybersecurity Education as a structured learning transformation. Inputs include training materials and learner knowledge that feed the central function. Controls—such as security policies and networking standards—set the rules for safe design and evaluation. Mechanisms such as instructors/experts and networking tools enable hands-on practice in a controlled environment. Outputs include practical network protection skills and demonstrable competency (often aligned with assessments or certifications), reflecting the ability to design, secure, monitor, and troubleshoot networks with security as a first-class requirement.
Interactive Check: Intro & System Concepts
Verify your understanding of how network boundaries, segmentation policies, and telemetry control traffic flow:
Introductory Concept Verification
1. Why is network security described as ensuring traffic does not simply “find the easiest path”?
Answer: Attackers do not rely on magic; they exploit flat networks, default-allow firewall rules, and missing segmentation to move laterally. Network security establishes strict boundaries and least-privilege flows so that communication is reliable for legitimate users and costly or impossible for attackers.
2. What constitutes the primary operational output expected from Network Security Education?
Answer: Practical network protection skill: learners who can design connectivity, enforce default-deny firewall policies, segment multi-tier architectures, and interpret flow and packet telemetry without surrendering operational control.
Network security is the front line of modern cybersecurity, protecting the confidentiality, integrity, and availability of data as it moves across interconnected systems. As organizations deliver services, handle sensitive information, and operate distributed teams, securing networks against insider misuse and sophisticated external threats has never been more critical.
Effective defenses are layered. Signals from AI & ML in cybersecurity power predictive detection and adaptive filtering at scale, while strong application security prevents web and API exploits from becoming network footholds. Combined with robust cryptography for data in transit and at rest, these controls create a resilient fabric that limits exposure and slows attackers down.
Identity is the new perimeter: identity and access management (MFA, least privilege, just-in-time access) constrains who can reach what, while continuous security awareness reduces social-engineering risk. When incidents occur, disciplined incident response & forensics contain impact, preserve evidence, and feed lessons learned into stronger policies and playbooks.
Today’s estates span cloud, on-prem, and roaming endpoints—and increasingly include safety-critical OT and CPS. That expanded attack surface demands Zero-Trust-style segmentation, egress controls, and high-quality telemetry (DNS/HTTP, flow, IDS) to see and stop lateral movement. Defenders track evolving tradecraft via threat intelligence and analyze patterns with data analysis and visualization—backed by scalable collection & storage, modern tools, and big-data analytics.
Finally, sound monitoring respects people. Ethical guardrails and social considerations help teams balance visibility with privacy. Red-teaming and ethical hacking validate assumptions, while domain-specific analytics tailor detections to each industry. Done well, network security blends engineering, strategy, and data-driven insight to keep infrastructures reliable and worthy of trust.
Building Cyber Resilience: Network Security Navigation
Discover how Network Security establishes perimeter defense, micro-segmentation, firewall filtering, and flow telemetry across the Cybersecurity cluster. Each card details stateful inspection, IDS/IPS rules, VPN tunnels, and zero-trust data plane controls.
Cybersecurity Overview
Presents the overall system architecture, mapping how network perimeter controls and flow telemetry integrate into enterprise defense-in-depth strategies.
Network Security
Focuses on Next-Gen Firewalls (NGFW), stateful packet inspection, IDS/IPS monitoring, VPN tunnels, zero-trust micro-segmentation, and network flow telemetry.
Application Security
Examines L7 Web Application Firewalls (WAF), API gateway rate-limiting, and inspecting HTTP/HTTPS payloads for injection exploits.
Endpoint Security
Covers host-based firewalls, VPN client posture checks, and securing remote endpoints against rogue Wi-Fi interception.
Cloud Security
Details Virtual Private Cloud (VPC) subnets, Security Groups, Azure NSGs, GCP firewall rules, and PrivateLink PaaS endpoints.
Identity & Access Management
Governs identity-aware network access control (802.1X), ZTNA brokers, and dynamic VPN authentication policies.
Cryptography
Applies TLS 1.2/1.3 protocol encryption, IPsec VPN tunneling, and certificate authority hygiene to protect data in transit.
Incident Response & Forensics
Orchestrates network traffic anomaly isolation, blocking malicious IP egress channels, and analyzing NetFlow packet captures during intrusions.
Threat Intelligence
Feeds malicious C2 IP blacklists and suspicious domain reputation feeds directly into firewall blocklists.
Ethical Hacking & Pen Testing
Executes network port scans (Nmap), ARP spoofing simulations, VLAN hopping tests, and perimeter firewall rule audits.
Cybersecurity Awareness
Educates users on avoiding insecure public Wi-Fi networks and recognizing rogue wireless access points.
Policy & Governance
Enforces network security policies, firewall rule review schedules, and regulatory compliance standards for traffic isolation.
CPS Security
Protects cyber-physical network links, securing telemetry streams across smart grids and connected transportation assets.
OT Security
Applies Purdue Model network zoning, industrial firewalls, and data diodes to isolate SCADA control loops from corporate IT.
AI & ML in Security
Leverages machine learning for predictive network anomaly detection, automated traffic classification, and adaptive DDoS mitigation.
Emerging Areas
Investigates zero-trust network access (ZTNA), eBPF kernel packet filtering, SASE architecture, and securing 5G network slices.
Key Topics in Network Security
Core hardware and software mechanisms governing network traffic flow:
Firewalls
- Stateful & Next-Gen Firewalls (NGFW): Inspecting connection states, layer-7 applications, and deep packet contents to enforce access policies.
Intrusion Detection and Prevention Systems (IDS/IPS)
- Signature & Anomaly Detection: Monitoring traffic against known attack patterns while flagging behavioral deviations in real time.
Virtual Private Networks (VPNs) & Transport Security
- Encrypted Tunnels: Securing remote access and site-to-site connectivity using TLS/SSL and IPsec protocols.
Interactive Quick Review: Network Controls
Reinforce key concepts regarding firewalls, IDS/IPS, and network segmentation before reading the FAQ:
Quick Review Verification
1. What is the operational difference between an IDS and an IPS?
Answer: An Intrusion Detection System (IDS) is a passive monitoring tool that analyzes traffic and alerts administrators when suspicious activity is detected. An Intrusion Prevention System (IPS) operates inline to actively block or drop malicious packets in real time.
2. How does network segmentation limit the blast radius of a security breach?
Answer: Segmentation divides a large enterprise network into isolated zones and subnets separated by internal firewalls. If an attacker breaches one segment, firewalls prevent lateral movement into sensitive database or crown-jewel application zones.
Network Security – Frequently Asked Questions
What is network security in cybersecurity?
Network security protects data confidentiality, integrity, and availability as it moves across computer networks using hardware, software, and policy controls.
What are the main types of network security threats?
Malware, phishing, DoS/DDoS attacks, Man-in-the-Middle (MitM) interception, unauthorized access via stolen credentials, and software vulnerability exploitation.
How do firewalls protect a network?
Firewalls filter incoming and outgoing traffic based on defined security rules, inspecting source/destination IPs, ports, and protocols to enforce least privilege.
What is the difference between IDS and IPS?
An IDS monitors traffic and generates alerts upon detecting suspicious patterns, while an IPS actively blocks or drops malicious packets in real time.
Why is network segmentation important?
Segmentation splits networks into smaller isolated zones, restricting lateral movement and containing malware blast radiuses if an initial breach occurs.
How do VPNs contribute to network security?
VPNs create encrypted tunnels over untrusted public networks (like public Wi-Fi), protecting data in transit from eavesdropping and man-in-the-middle attacks.
Cybersecurity for Networks: Summing Up
Network security is never “done”—it’s a living program that blends layered controls, identity-centric access, high-quality telemetry, and disciplined response. In complex, hybrid environments, the winning posture is Zero-Trust aware: authenticate and authorize every request, encrypt by default, segment aggressively, and assume breach to limit blast radius and dwell time.
- Prevent: least-privilege access, hardened configs, micro-segmentation, strong DNS/TLS hygiene.
- Detect: rich telemetry (DNS/HTTP, flow, IDS), baselines, prioritized alerts mapped to MITRE ATT&CK.
- Respond & recover: practiced runbooks, containment steps, forensics, and measurable RTO/RPO.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is network security and why is it essential for modern organizations?
Answer: Network security is the practice of protecting network infrastructure and transmitted data from unauthorized access, misuse, or disruption, safeguarding critical business operations.
2. What are the primary components of a robust network security strategy?
Answer: Firewalls, IDS/IPS, encryption protocols (TLS/IPsec), secure architecture, network segmentation, and continuous log monitoring.
3. How do firewalls contribute to network security?
Answer: By acting as barriers that filter traffic based on security rules, blocking unauthorized connections, and segmenting network zones.
4. What role do IDS and IPS play in protecting networks?
Answer: IDS monitors traffic and flags anomalies, while IPS actively blocks detected attacks in real time to stop intrusions before damage occurs.
5. How does encryption help secure network communications?
Answer: By encoding transmitted data into unreadable ciphertext, ensuring confidentiality and integrity even if packets are intercepted over public networks.
6. What are some common network threats and vulnerabilities that organizations face?
Answer: Malware, phishing, DDoS attacks, misconfigurations, unpatched software vulnerabilities, and weak credentials.
7. How does network segmentation improve overall security posture?
Answer: By dividing networks into isolated zones, limiting lateral movement and containing malware blast radiuses during a breach.
8. What is the importance of regular network monitoring and vulnerability assessments?
Answer: They provide real-time visibility into traffic anomalies and identify infrastructure weaknesses before attackers can exploit them.
9. How do policies and user education contribute to network security?
Answer: Policies set behavioral baselines, while education programs help users recognize phishing and avoid human-error security breaches.
10. What future trends are expected to shape network security strategies?
Answer: Artificial intelligence automation, cloud-native security integration, and Zero Trust Architecture (ZTA) expansion.
Thought-Provoking Architectural Questions
1. How might the integration of artificial intelligence transform network security defenses in the future?
Answer: AI will autonomously detect complex multi-vector anomalies and execute real-time mitigation rules at machine speed across distributed hybrid networks.
2. What impact could quantum computing have on current network encryption methods?
Answer: Quantum algorithms (Shor’s) will break RSA and ECC asymmetric key exchanges used in TLS/IPsec, necessitating migration to post-quantum cryptography.
3. In what ways can network segmentation be optimized to enhance security and efficiency?
Answer: Through micro-segmentation and software-defined networking (SDN), isolating individual workloads based on identity and service type without rigid VLAN boundaries.
4. How might the rise of IoT devices challenge traditional network security models?
Answer: Unmanaged, resource-constrained IoT nodes expand the attack surface, requiring specialized micro-gateways and behavioral anomaly profiling.
5. What role does user behavior analytics play in modern network security?
Answer: Establishes baseline user activity profiles to detect credential compromise and insider threats when account behavior deviates from normal patterns.
6. How can continuous network monitoring transform incident response strategies?
Answer: Provides real-time packet and flow telemetry, drastically reducing Mean Time to Detect (MTTD) and supplying forensic data for rapid containment.
7. What are the potential benefits and risks of adopting a zero-trust network security model?
Answer: Benefits include elimination of implicit trust and containment of lateral movement; risks include increased operational complexity and potential user friction.
8. How might advancements in cloud security influence network security architectures?
Answer: Shifts focus from hardware firewalls to cloud-native virtual firewalls, SASE architectures, and software-defined perimeter gateways.
9. In what ways can incident response teams improve collaboration with digital forensics experts?
Answer: By sharing real-time PCAP captures, automated alert telemetry, and maintaining joint runbooks from the earliest stages of triage.
10. How could blockchain and distributed ledger systems enhance the integrity of forensic evidence?
Answer: By providing immutable, tamper-proof logging of evidence acquisition steps and maintaining a verifiable chain of custody.
11. What strategies can organizations adopt to balance rapid incident response with thorough forensic analysis?
Answer: Employing a dual-track approach where automated scripts capture volatile evidence immediately while response teams execute short-term containment.
12. How might the evolution of regulatory requirements shape future incident response and forensics?
Answer: Imposing strict breach notification timelines and mandatory forensic logging standards across critical sectors.
Numerical Engineering Problems & Solutions
Problem 1: Intrusion Block Rate & Annual Breach Volume
A company experiences 200 network intrusion attempts per day. Its security system blocks 98% (0.98) of these attempts. Calculate blocked attempts per day, successful intrusions per day, and annual successful intrusion count (365 days).
A company experiences 200 network intrusion attempts per day. Its security system blocks 98% (0.98) of these attempts. Calculate blocked attempts per day, successful intrusions per day, and annual successful intrusion count (365 days).
Solution:
- Blocked attempts per day = 200 × 0.98 = 196 blocked attempts/day
- Successful intrusions per day = 200 – 196 = 4 successful intrusions/day
- Annual successful intrusions = 4 × 365 = 1,460 intrusions/year
Problem 2: Firewall Volumetric DDoS Packet Surge Metrics
A firewall processes 500,000 packets per minute. A volumetric DDoS attack increases network traffic by 150%. Calculate new packet rate per minute, extra packets per hour (60 minutes), and extra packets per day (24 hours).
A firewall processes 500,000 packets per minute. A volumetric DDoS attack increases network traffic by 150%. Calculate new packet rate per minute, extra packets per hour (60 minutes), and extra packets per day (24 hours).
Solution:
- Increased packet rate = 500,000 × 1.50 = 750,000 extra packets per minute (total rate = 1,250,000 packets/min)
- Extra packets per hour = 750,000 extra packets/min × 60 minutes = 45,000,000 packets/hour
- Extra packets per day = 45,000,000 × 24 hours = 1,080,000,000 packets/day
Problem 3: Network Monitoring Critical Event Volume Metrics
A network monitoring system logs 2,000 events per minute. Telemetry indicates that 0.25% (0.0025) of events are flagged as critical. Calculate critical events per minute, per hour, and per day.
A network monitoring system logs 2,000 events per minute. Telemetry indicates that 0.25% (0.0025) of events are flagged as critical. Calculate critical events per minute, per hour, and per day.
Solution:
- Critical events per minute = 2,000 × 0.0025 = 5 critical events/minute
- Critical events per hour = 5 × 60 = 300 critical events/hour
- Critical events per day = 300 × 24 = 7,200 critical events/day
Problem 4: IDS False Positive Reduction via Rule Tuning
An IDS has a false positive rate of 0.5% (0.005) over 1,000,000 network events. Calculate initial false positives. An upgrade reduces the false positive rate by 80%. Calculate new false positive count and total false positives eliminated.
An IDS has a false positive rate of 0.5% (0.005) over 1,000,000 network events. Calculate initial false positives. An upgrade reduces the false positive rate by 80%. Calculate new false positive count and total false positives eliminated.
Solution:
- Initial false positives = 1,000,000 × 0.005 = 5,000 false positives
- New false positive rate = 0.5% × (1 – 0.80) = 0.1% (0.001)
- New false positive count = 1,000,000 × 0.001 = 1,000 false positives
- Total reduction = 5,000 – 1,000 = 4,000 fewer false positives
Problem 5: Network Vulnerability Scanner Throughput & Delay Impact
A network security tool scans 10,000 IP addresses in 30 minutes. Calculate scanning rate per minute. Calculate time required to scan 100,000 IP addresses. Calculate new scan time and percentage time increase if scanning speed drops by 20% due to network throttling.
A network security tool scans 10,000 IP addresses in 30 minutes. Calculate scanning rate per minute. Calculate time required to scan 100,000 IP addresses. Calculate new scan time and percentage time increase if scanning speed drops by 20% due to network throttling.
Solution:
- Scanning rate = 10,000 IPs / 30 minutes = 333.33 IPs per minute
- Time for 100,000 IPs = 100,000 / 333.33 = 300 minutes (5 hours)
- With a 20% slower speed, new time = 300 minutes × 1.20 = 360 minutes (6 hours)
- Percentage time increase = 20.0%
Problem 6: Classical Brute-Force Key Search Feasibility for 256-Bit Encryption
A secure network uses 256-bit encryption (2^256 key space). A cracking cluster tests 10^9 keys per second. Calculate total time required in seconds and convert to years using 3.15 × 10^7 seconds per year.
A secure network uses 256-bit encryption (2^256 key space). A cracking cluster tests 10^9 keys per second. Calculate total time required in seconds and convert to years using 3.15 × 10^7 seconds per year.
Solution:
- Total keys = 2^256 ≈ 1.1579 × 10^77 keys
- Time in seconds = (1.1579 × 10^77) / 10^9 = 1.1579 × 10^68 seconds
- Time in years = (1.1579 × 10^68) / (3.15 × 10^7) ≈ 3.676 × 10^60 years
Problem 7: Blast Radius Reduction via Network Segmentation
A network segmentation project divides an enterprise network into 8 segments, reducing lateral movement risk by 70%. If an initial unsegmented breach could potentially affect 1,000 devices, calculate potential devices affected after segmentation and absolute device reduction.
A network segmentation project divides an enterprise network into 8 segments, reducing lateral movement risk by 70%. If an initial unsegmented breach could potentially affect 1,000 devices, calculate potential devices affected after segmentation and absolute device reduction.
Solution:
- Expected devices affected after segmentation = 1,000 devices × (1 – 0.70) = 1,000 × 0.30 = 300 devices
- Absolute device reduction = 1,000 – 300 = 700 devices protected from lateral spread
Problem 8: Network Audit Vulnerability Remediation Metrics
A network security audit finds 120 vulnerabilities in a system. A remediation plan fixes 85% (0.85) of them. Calculate number of fixed vulnerabilities, remaining vulnerabilities, and reduction percentage.
A network security audit finds 120 vulnerabilities in a system. A remediation plan fixes 85% (0.85) of them. Calculate number of fixed vulnerabilities, remaining vulnerabilities, and reduction percentage.
Solution:
- Fixed vulnerabilities = 120 × 0.85 = 102 vulnerabilities fixed
- Remaining vulnerabilities = 120 – 102 = 18 vulnerabilities
- Reduction percentage = (102 / 120) × 100 = 85.0%
Problem 9: AI Threat Detection Flagging Volume Metrics
A network monitoring tool generates 800,000 logs per day. An AI anomaly detection system flags 0.1% (0.001) of logs as potential threats. Calculate flagged logs per day, weekly (7 days), and monthly (30 days).
A network monitoring tool generates 800,000 logs per day. An AI anomaly detection system flags 0.1% (0.001) of logs as potential threats. Calculate flagged logs per day, weekly (7 days), and monthly (30 days).
Solution:
- Flagged logs per day = 800,000 × 0.001 = 800 flagged logs/day
- Flagged logs per week (7 days) = 800 × 7 = 5,600 logs/week
- Flagged logs per month (30 days) = 800 × 30 = 24,000 logs/month
Problem 10: Firewall Latency Reduction & Aggregate Time Saved
A firewall upgrade reduces network latency by 15% from an initial baseline of 100 ms latency. Calculate new latency per request, time saved per 1,000 requests, and total time saved for 1,000,000 requests in seconds.
A firewall upgrade reduces network latency by 15% from an initial baseline of 100 ms latency. Calculate new latency per request, time saved per 1,000 requests, and total time saved for 1,000,000 requests in seconds.
Solution:
- New latency per request = 100 ms × (1 – 0.15) = 85 ms per request
- Time saved per request = 100 ms – 85 ms = 15 ms saved/request
- Time saved per 1,000 requests = 1,000 × 15 ms = 15,000 ms = 15.0 seconds
- Total time saved for 1,000,000 requests = 1,000,000 × 15 ms = 15,000,000 ms = 15,000 seconds (250 minutes)
Problem 11: Network Access Control (NAC) Unauthorized Attempt Reduction
A Network Access Control (NAC) system enforces policies across 5,000 devices. Before NAC, unauthorized access attempts averaged 2% (0.02) per device per day. NAC enforcement reduces unauthorized access attempts by 90%. Calculate daily unauthorized attempts before and after NAC enforcement, and total daily reduction.
A Network Access Control (NAC) system enforces policies across 5,000 devices. Before NAC, unauthorized access attempts averaged 2% (0.02) per device per day. NAC enforcement reduces unauthorized access attempts by 90%. Calculate daily unauthorized attempts before and after NAC enforcement, and total daily reduction.
Solution:
- Unauthorized attempts per day before = 5,000 devices × 0.02 = 100 attempts/day
- Unauthorized attempts per day after (90% reduction) = 100 × (1 – 0.90) = 10 attempts/day
- Total daily reduction = 100 – 10 = 90 fewer unauthorized attempts/day
Problem 12: Incident Response Drill Recovery Time Optimization
An incident response drill reduces recovery time from 50 minutes down to 20 minutes per incident. An organization conducts 12 drills per year. Calculate time saved per drill and total annual time saved in minutes.
An incident response drill reduces recovery time from 50 minutes down to 20 minutes per incident. An organization conducts 12 drills per year. Calculate time saved per drill and total annual time saved in minutes.
Solution:
- Time saved per drill = 50 min – 20 min = 30 minutes saved/drill
- Total annual time saved = 12 drills × 30 minutes = 360 minutes/year (6 hours)
Network Security — Summary & Wrap-Up
Network security forms the foundational perimeter of enterprise cybersecurity architectures. By implementing stateful Next-Generation Firewalls, intrusion prevention systems, encrypted IPsec/TLS tunnels, Zero-Trust micro-segmentation, and comprehensive flow telemetry, security professionals ensure that data transport remains confidential, integral, and available while stopping lateral movement in its tracks.