Prepare for University Studies & Career Advancement
Endpoint Security
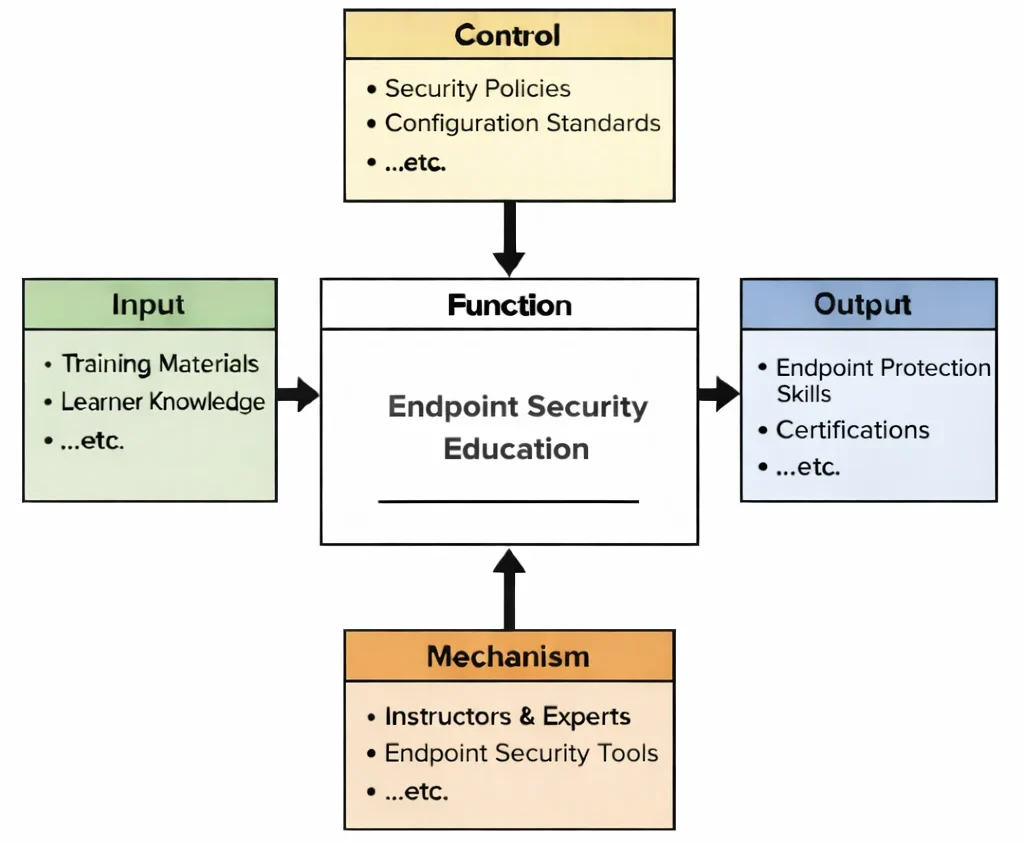
Endpoint Security Education is about defending the places where real people actually work: laptops, phones, tablets, and all the “small doors” into larger systems. The diagram shows how this defense is taught as a disciplined craft. Learners bring in inputs—foundational knowledge and practical examples—while controls such as policies and configuration standards insist on consistency: patching cannot be optional, privileges cannot be casual, and settings must be explainable rather than accidental. With mechanisms like labs and security tools, students practice what it means to harden a device, manage updates, reduce attack surface, detect suspicious behavior, and respond without panic when alerts appear. The output is not merely a checklist mindset, but an operational readiness: learners who can keep endpoints healthy, predictable, and monitored—so everyday devices become reliable participants in a secure environment instead of the easiest point of entry.
Endpoint Security Education in IDEF0 form: standards and policies guide tool-enabled learning into endpoint protection skills.
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Endpoint Security Education as a structured transformation. Inputs include training materials and learner baseline knowledge of operating systems, device usage, and basic security concepts. Controls include security policies, configuration standards, and required practices that define how endpoints should be hardened, monitored, and managed. Mechanisms include instructors, experts, lab environments, and endpoint security tools (such as EDR/antimalware, patching systems, and device management platforms) that enable hands-on practice. Outputs include learners who can apply endpoint protection techniques, follow secure configuration baselines, respond to device-level alerts, and demonstrate competence through assessments or certifications.
Interactive Check: Intro & System Concepts
Verify your understanding of how endpoint hardening and continuous telemetry transform user devices into resilient defense barriers:
Introductory Concept Verification
1. Why are user endpoints described as the “small doors” into larger corporate networks?
Answer: Endpoints (laptops, mobile phones, workstations) directly interact with external networks, personal emails, and public Wi-Fi. Because human users operate them daily, attackers exploit endpoint vulnerabilities via spear-phishing or unpatched software to harvest credentials and establish initial footholds into internal enterprise systems.
2. What distinguishes an operational readiness mindset from a simple checklist approach in endpoint defense?
Answer: A checklist mindset treats security as a static one-time setup. Operational readiness integrates real-time behavioral monitoring (EDR/XDR), automated patch management, zero-trust posture checks, and rapid incident response playbooks to keep devices continuously monitored and resilient under active threat.
Endpoint security is a core pillar of cybersecurity because laptops, mobiles, servers, VMs, containers, and IoT devices are the first—and often weakest—line of defense. With remote work and heterogeneous device fleets, protecting endpoints is no longer optional: it’s foundational to preventing malware, credential theft, ransomware, and data loss.
Modern endpoint protection blends identity-aware controls with continuous monitoring. It works in concert with identity & access management (MFA, least privilege), cryptography (device/file encryption, secure transport), application security (safe-by-default configs), and network security (micro-segmentation, zero-trust access). Increasingly, AI & ML in cybersecurity augment detection and response by spotting behavioral anomalies at scale.
Because endpoints are provisioned and updated continuously, defenses must plug into DevOps/Infrastructure-as-Code and CI/CD: golden images, device baselines, agent health checks, and policy as code. When issues arise, tight loops with incident response & forensics and threat intelligence speed containment, triage, and learning.
The rise of edge devices and constrained hardware (see edge computing) expands the attack surface. Endpoint Detection & Response (EDR) and XDR provide real-time telemetry and control, while data science & analytics help prioritize signals and reduce noise—balanced with privacy-by-design and clear data handling practices.
Compliance and readiness matter, too: controls aligned to security & identity management frameworks, ongoing security awareness, and routine exercises improve resilience. In safety-critical domains such as cyber-physical systems and OT, robust endpoint posture is essential to prevent physical-world impact.
As organizations adopt zero-trust and XDR architectures, endpoint security anchors the strategy: verify identity and device health continuously, limit blast radius, and automate rapid recovery. Done well, it protects users and data without getting in the way of productivity.
Endpoint security protects laptops, desktops, and connected devices—the everyday “front doors” into a network.
This illustration visualizes endpoint security as a protective layer wrapped around the many devices people use to work and connect online. A central shield-and-lock emblem suggests strong defense, while surrounding laptops, monitors, and IoT-style symbols represent endpoints such as personal computers, mobile devices, and smart connected equipment. The radiating rings and network lines imply continuous monitoring, policy enforcement, and rapid response—key ideas in endpoint protection, detection, and containment. Overall, the image communicates that safeguarding individual devices is essential because attacks often begin at the edge of a system, where users and hardware meet the wider network.
Building Cyber Resilience: Endpoint Security Navigation
Discover how Endpoint Security enforces device posture checks, real-time EDR detection, disk encryption, and automated patch rollouts across the Cybersecurity cluster. Each card details host hardening, mobile device management (MDM), zero-trust device attestation, and ransomware containment.
Presents the overall system architecture, mapping how device-level endpoint controls serve as the frontline defense complementing network and cloud security.
Investigates hardware Root of Trust attestation, post-quantum endpoint disk encryption, and autonomous self-healing endpoint agents.
Key Topics in Endpoint Security
Modern endpoint defense shifts focus from static antivirus scans to real-time behavioral containment and device posture management:
Antivirus and Antimalware Solutions
Signature-Based vs. Behavioral Analysis: Moving beyond legacy signature databases toward real-time behavioral heuristics that detect zero-day exploits and polymorphic code.
Limitations: Static signatures fail against fileless malware; solutions must integrate with EDR platforms for comprehensive protection.
Endpoint Detection and Response (EDR/XDR) Systems
Continuous Telemetry: Recording process executions, command-line arguments, network sockets, and registry edits across entire device fleets (CrowdStrike, SentinelOne, Defender).
Automated Containment: Instantly isolating compromised endpoints from the local network via EDR software commands to prevent lateral ransomware spread.
Securing Bring Your Own Device (BYOD) & Mobile Fleets
Mobile Device Management (MDM): Utilizing Intune or Jamf to enforce full-disk encryption, remote wipe controls, and work-profile containerization on personal devices.
Conditional Access: Requiring verified device health attestation before granting user access to enterprise SaaS and cloud resources.
Applications of Endpoint Security
Production practices for hardening operating systems and containing active threats:
Deploying Device Encryption and Secure Boot
Full-Disk Encryption: Protecting stored disk volumes with TPM-backed BitLocker (Windows), FileVault (macOS), or LUKS (Linux) to prevent offline data extraction if hardware is stolen.
Secure Boot: Cryptographically validating bootloaders and OS kernel signatures during startup to block bootkits and unauthorized firmware.
Monitoring for Suspicious Device Behavior
Tracking living-off-the-land (LOLBin) executions, such as Microsoft Office applications launching PowerShell or command prompts.
Endpoint Hardening Baselines & Playbooks
Cross-platform quick wins for establishing a secure configuration baseline:
Windows 10/11 Hardening Quick Wins
Enable BitLocker with TPM, XTS-AES-256, and escrow recovery keys in Active Directory / Azure AD.
Turn on Defender Cloud-Delivered Protection, Tamper Protection, and Attack Surface Reduction (ASR) rules.
Disable SMBv1, legacy NTLM, and unsigned macros; enforce LAPS for local administrator rotation.
macOS Hardening Quick Wins
Enable FileVault full-disk encryption and escrow recovery keys via Jamf / MDM.
Enforce Gatekeeper and Apple Notarization checks; block unsigned kernel extensions.
Turn on Application Firewall in stealth mode; restrict screen lock timeout to ≤ 5 minutes.
Linux (Ubuntu/RHEL) Hardening Quick Wins
Encrypt root and swap partitions with LUKS during OS provisioning.
Configure ufw or firewalld with a default-deny inbound posture.
Enable auditd rules for /etc/sudoers, auth logs, and binary execution monitoring.
Interactive Quick Review: Endpoint Defenses
Reinforce key concepts regarding EDR detection, disk encryption, and mobile device management before reading the FAQ:
Quick Review Verification
1. How does Attack Surface Reduction (ASR) prevent ransomware execution on Windows endpoints?
Answer: ASR blocks common attack paths at the operating system level, such as preventing Microsoft Office applications from launching child processes (PowerShell/CMD), blocking credential stealing from LSASS memory, and stopping untrusted executables from writing to protected user folders.
2. Why is full-disk encryption (BitLocker/FileVault) insufficient on its own if an endpoint is powered on and logged in?
Answer: Full-disk encryption protects data at rest when a device is powered off or stolen. Once an endpoint boots up and the user logs in, the storage volume is transparently decrypted in memory, requiring secondary controls (EDR, EPP, least-privilege IAM, and app allow-listing) to protect active files from malware or network exploits.
Endpoint Security – Frequently Asked Questions
What is endpoint security in cybersecurity?
Endpoint security is the practice of protecting individual user devices (laptops, desktops, smartphones, servers, IoT) connecting to a network. It monitors devices for malware, anomalous behavior, and unpatched vulnerabilities.
How does endpoint security differ from traditional antivirus?
Traditional antivirus relies on static file signature matching. Modern endpoint security platforms incorporate real-time behavioral analytics, Endpoint Detection and Response (EDR), automated network containment, and device posture attestation.
Why is endpoint security critical in remote work environments?
Remote devices connect from home networks and public Wi-Fi outside corporate network perimeters. Securing the endpoint ensures that data encryption, MFA, and access controls travel with the device wherever the user logs in.
What are common attack types targeting endpoints?
Phishing attachments, fileless PowerShell malware, ransomware encryptors, drive-by web downloads, credential-harvesting tools (LSASS dumpers), and unpatched browser vulnerabilities.
How does endpoint security fit into a Zero Trust model?
Zero Trust requires continuous verification. Endpoint security supplies continuous device health attestation (patch state, disk encryption, EDR status) before granting permission to corporate SaaS applications or VPN tunnels.
What safe habits improve endpoint security for users?
Enabling automatic OS updates, utilizing password managers with unique passphrases, enabling Multi-Factor Authentication (MFA), avoiding untrusted downloads, and locking screens when leaving workstations unattended.
Endpoint Security: Conclusion
Endpoint security anchors a zero-trust posture: continuously verify user identity and device health, minimize blast radius, and automate rapid recovery. Done well, it protects laptops, mobiles, servers, containers, and IoT/OT devices without getting in the way of work.
Continuous Assurance: Posture checks, MFA, least privilege, and policy-as-code.
Defense in Depth: Hardening + patching, EDR/XDR telemetry and containment, app control, and resilient backups.
Fast Response: Tight integration with IR playbooks, isolation workflows, and auto-remediation to cut MTTR.
Privacy & Performance: Data-minimizing telemetry, clear retention, and lightweight agents that respect users.
Complete Coverage: Consistent baselines across Windows/macOS/Linux, iOS/Android, cloud/edge, and OT environments.
1. What is endpoint security and why is it important for modern organizations?
Answer: Endpoint security refers to protecting individual user devices connecting to enterprise networks. It is important because user endpoints are the primary targets for malware, ransomware, and credential theft attempts.
2. What are the primary components of a robust endpoint security strategy?
3. How do endpoint security solutions help prevent data breaches?
Answer: By continuously monitoring process execution, enforcing disk encryption, isolating compromised hosts automatically, and preventing unauthorized executables from exfiltrating sensitive files.
4. What role does employee behavior play in the effectiveness of endpoint security?
Answer: Human behavior dictates whether phishing links are clicked, devices are locked, or software updates are applied promptly. Informed users complement technical controls to form a resilient defense.
5. How do Endpoint Detection and Response (EDR) tools enhance security monitoring?
Answer: EDR tools capture process trees, command lines, and network socket connections in real time, executing behavioral anomaly analysis to isolate compromised hosts automatically.
6. What challenges are associated with managing endpoint security in large, diverse networks?
Answer: Managing heterogeneous operating systems (Windows, macOS, Linux, iOS, Android), ensuring patch compliance across remote workforces, preventing performance degradation from heavy security agents, and handling BYOD privacy concerns.
7. How does patch management contribute to effective endpoint security?
Answer: Timely patch management remediates known software vulnerabilities (CVEs) in operating systems, web browsers, and applications before threat actors can weaponize them.
8. What is the significance of encryption in endpoint security?
Answer: Full-disk encryption (BitLocker/FileVault) protects offline data confidentiality, ensuring that sensitive corporate data remains unreadable if a physical device is lost or stolen.
9. How can organizations measure the effectiveness of their endpoint security measures?
Answer: By tracking device patch compliance percentages, measuring EDR coverage rates, evaluating Mean Time to Detect (MTTD) and Contain (MTTR), and auditing local administrator privilege counts.
10. What future trends are expected to shape the field of endpoint security?
Answer: AI-driven autonomous agent response, post-quantum disk encryption, hardware Root of Trust attestation, Zero Trust Network Access (ZTNA) integration, and Unified Endpoint Management (UEM).
Thought-Provoking Architectural Questions
1. How will the increasing complexity of endpoint devices influence future cybersecurity strategies?
Answer: Forces a shift from perimeter-based firewalls to device-centric Zero Trust models, requiring continuous cryptographic attestation of device posture before granting microservice API access.
2. What impact will artificial intelligence have on the evolution of endpoint security measures?
Answer: On-device ML models will analyze high-frequency process telemetry in real time, executing millisecond containment actions against previously unseen zero-day ransomware without waiting for cloud lookup roundtrips.
3. In what ways could the rise of remote work reshape endpoint security requirements for organizations?
Answer: Mandates cloud-native endpoint management (MDM), SASE/ZTNA encrypted tunnels replacing corporate office firewalls, and strict BYOD work-profile containerization to isolate personal activities from corporate data.
4. How can the integration of endpoint security with cloud services enhance an organization’s overall security posture?
Answer: Cloud XDR platforms correlate endpoint process logs with cloud API logs (CloudTrail/Azure AD), enabling security teams to trace an attack from a initial spear-phishing click on a laptop all the way to cloud S3 bucket exfiltration.
5. What ethical considerations should organizations address when implementing advanced endpoint security measures?
Answer: Respecting employee privacy on BYOD/corporate devices by enforcing strict telemetry minimization, excluding personal keystrokes or screen captures, and publishing transparent data retention policies.
6. How might advancements in endpoint security technology affect the future of cyber attack methodologies?
Answer: As EDR agents block binary executables, adversaries shift to living-off-the-land techniques (LOLBins), memory-only fileless attacks, driver vulnerabilities (BYOVD), and targeting unmanaged smart IoT peripherals.
7. What role does user training play in complementing technological advancements in endpoint security?
Answer: Prevents initial access compromise. While EDR catches execution attempts, user awareness stops employees from entering credentials into phishing sites or approving unauthorized MFA push notifications.
8. How can endpoint security solutions be adapted to protect emerging technologies like wearable devices?
Answer: By deploying lightweight security micro-runtimes, network micro-segmentation, and enforcing hardware cryptographic attestation via Bluetooth/BLE gateway proxies.
9. What are the potential economic implications for organizations that fail to implement effective endpoint security?
Answer: Million-dollar ransomware extortion costs, business operational downtime, regulatory non-compliance fines (GDPR/HIPAA), customer churn, and elevated cyber insurance premiums.
10. How might the evolution of endpoint security shape the future of regulatory compliance?
Answer: Compliance standards (SOC 2, ISO 27001) will shift from static annual policy documentation toward mandatory real-time automated proof of endpoint encryption and automated patch compliance telemetry.
11. What challenges do organizations face when integrating endpoint security with legacy systems?
Answer: Unsupported legacy operating systems (Windows XP/7) cannot run modern kernel-based EDR agents. Overcome by network micro-segmentation, virtual patching, and placing legacy nodes behind dedicated security gateways.
12. How can cross-industry collaboration enhance next-generation endpoint security solutions?
Answer: By sharing standardized open-source threat detection rules (Sigma) and participating in threat intelligence sharing platforms (ISACs) to distribute new malware IOCs globally in seconds.
Numerical Engineering Problems & Solutions
Problem 1: Infection Volume & Reduction Metrics Across an Endpoint Fleet An organization manages 2,000 endpoints with a reported baseline infection rate of 0.5% (0.005) per month. Calculate expected monthly infected endpoints, total expected annual infections, and new expected annual infections if a new EDR solution cuts the infection rate by 60%.
Answer: Monthly baseline is 10 infections (120/year); the EDR solution reduces annual infections down to 48 endpoints per year.
Problem 2: Net Benefit Analysis for Endpoint Security Expenditure A firm spends $150 per endpoint annually across 1,000 endpoints ($150,000 annual software expense). A new security policy reduces annual security breaches by 70% from a baseline average of 50 breaches per year. If each breach costs $500 in labor, calculate breach savings and net financial benefit.
Solution:
Total annual security expenditure = 1,000 × $150 = $150,000/year
Answer: Breach savings total $17,500, resulting in a net benefit of -$132,500 (demonstrating that low-cost minor breaches alone do not offset basic endpoint software licenses unless major data loss risks are factored into the model).
Problem 3: False Positive Alert Reduction with AI EDR Upgrade An EDR system processes 5,000 events per hour with a false positive rate of 0.2% (0.002). Calculate false positives per hour, daily false positives (24 hours), and new daily false positives after an AI upgrade cuts false positives by 80%.
Answer: Baseline false positives total 240 daily; the AI upgrade reduces false alerts to 48 false alerts per day.
Problem 4: Calculating Potential Data Breach Loss Reduction An endpoint fleet processes 1,200 GB of sensitive data monthly. Before EDR deployment, 5% of monthly data is exposed during security incidents. A breach costs $2,000 per GB of compromised data. Implementing a new solution cuts data breach loss volume by 90%. Calculate potential annual breach cost before and after implementation, and annual savings.
Answer: The solution reduces annual data breach losses from $1,440,000 to $144,000, saving $1,296,000 per year.
Problem 5: Calculating Downtime Savings from Faster Breach Containment An incident response automation playbook reduces endpoint breach containment time from 90 minutes down to 30 minutes. Downtime costs $50 per minute. Calculate resolution cost per incident before and after improvement, and total annual savings for 20 incidents per year.
Solution:
Resolution cost before = 90 minutes × $50/min = $4,500/incident
Resolution cost after = 30 minutes × $50/min = $1,500/incident
Savings per incident = $4,500 – $1,500 = $3,000 saved/incident
Total annual savings across 20 incidents = 20 × $3,000 = $60,000/year
Answer: Cost per incident drops from $4,500 to $1,500, generating $60,000 in total annual savings.
Problem 6: Calculating Deployment ROI for Endpoint Protection Software Deploying an EPP platform across 3,000 devices costs $80 per device ($240,000 total). Baseline breach losses average 40 incidents per year at $10,000 per breach ($400,000 annual loss). The platform reduces breaches by 75%. Calculate annual breach cost savings and Return on Investment (ROI) percentage.
Solution:
Total deployment cost = 3,000 devices × $80 = $240,000
ROI percentage = ($300,000 / $240,000) × 100 = 125.0%
Answer: The platform saves $300,000 per year, achieving an ROI of 125%.
Problem 7: Patch Management Vulnerability Decrease Metrics An automated patch management system reduces endpoint software vulnerabilities by 85% from an initial fleet average of 200 vulnerabilities per device. Calculate vulnerabilities remaining, number of vulnerabilities fixed, and percentage decrease.
Answer: System identifies 400 daily threat logs, totaling 146,000 threat logs per year.
Problem 9: Calculating Additional Secured Endpoints from Detection Upgrade An EDR software upgrade raises detection accuracy from 92% to 98% across an enterprise network of 10,000 endpoints. Calculate correctly secured endpoints before and after the upgrade, and net additional endpoints secured.
Solution:
Endpoints secured before = 10,000 × 0.92 = 9,200 endpoints
Endpoints secured after = 10,000 × 0.98 = 9,800 endpoints
Answer: Accuracy gain secures 600 additional endpoints (bringing total secured devices to 9,800).
Problem 10: Risk Assessment Expected Loss Savings Risk modeling indicates an 8% (0.08) annual breach probability across 5,000 endpoints, with an average breach remediation cost of $1,500. A new protection agent cuts breach probability by 50% down to 4% (0.04). Calculate expected annual loss before and after mitigation, and annual dollar savings.
Solution:
Expected annual loss before = 5,000 endpoints × 0.08 × $1,500 = $600,000/year
New breach probability = 8% × 0.50 = 4% (0.04)
Expected annual loss after = 5,000 endpoints × 0.04 × $1,500 = $300,000/year
Annual dollar savings = $600,000 – $300,000 = $300,000/year
Answer: Mitigation reduces expected loss from $600,000 to $300,000, saving $300,000 per year.
Problem 11: Calculating Labor Time Saved via Automated Endpoint Patching An automated system reduces manual OS patch time from 20 minutes to 5 minutes per endpoint. For 4,000 endpoints, calculate time saved per weekly update cycle in hours, monthly time saved (4 weekly cycles), and annual time saved in days (24 hours/day).
Solution:
Time saved per endpoint = 20 min – 5 min = 15 minutes saved
Time saved per cycle (4,000 endpoints) = 4,000 × 15 = 60,000 minutes = 1,000 hours/cycle
Answer: Firewall filtering eliminates 1,050 malicious events daily, reducing malicious events down to 450 per day.
Endpoint Security — Summary & Wrap-Up
Endpoint security anchors modern cybersecurity defense across user devices, remote laptops, cloud virtual machines, and IoT hardware. By combining full-disk encryption, OS hardening baselines, automated patch management, real-time EDR behavioral analytics, and zero-trust device posture checks, security teams transform vulnerable user endpoints into resilient, well-governed digital assets.