
Operational Technology (OT) Security Education teaches a different rhythm of security—one where “just patch it now” is often the wrong reflex. The diagram shows why. Learners bring in inputs such as foundational knowledge and training resources, but OT learning is shaped by strong controls: industrial regulations and safety policies that treat stability, uptime, and human safety as first principles. Mechanisms like expert-led labs and OT security tooling let students practice realistic decisions: segmenting networks without disrupting control loops, monitoring quietly without adding fragility, designing access so maintenance is possible without turning every engineer into an administrator, and planning incident response when “shut it down” may be the most dangerous option. The output is practical judgment—learners who can protect systems that run factories, utilities, transport, and critical infrastructure, balancing cybersecurity needs with the uncompromising demands of safety and continuous operation.
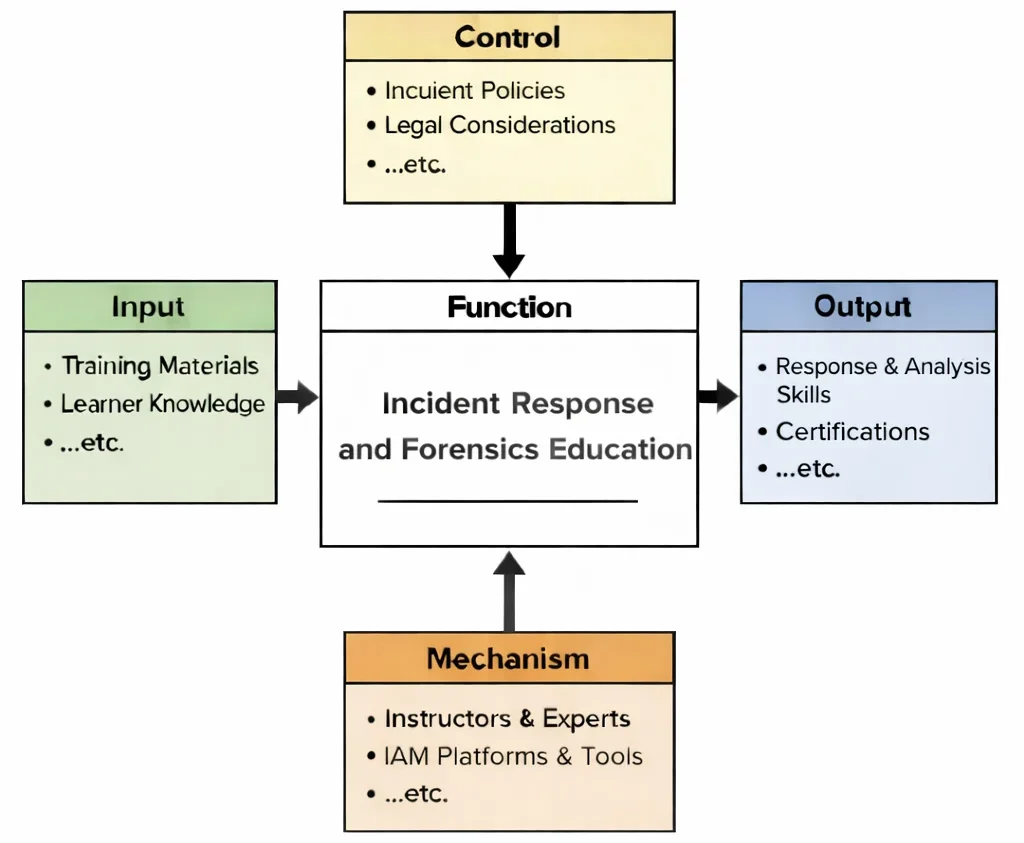
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Operational Technology (OT) Security Education as a structured transformation. Inputs include training materials and learner knowledge of industrial systems and basic security concepts. Controls include industrial regulations, safety policies, standards, and governance requirements that constrain what can be changed and how risk is managed in OT environments. Mechanisms include instructors, experts, OT security tools, lab environments, and realistic scenarios involving PLCs, SCADA concepts, segmentation, monitoring, and incident handling. Outputs include learners who develop OT protection skills—able to prioritize safety, understand operational constraints, and apply security measures that fit the realities of industrial reliability and uptime.
Interactive Check: Intro & System Concepts
Verify your understanding of how industrial safety priorities, uptime constraints, and physical process control shape OT security:
Introductory Concept Verification
1. Why is the reflex to “just patch it now” often dangerous in Operational Technology environments?
Answer: Unlike IT systems where software patches can be applied instantly and rebooted, OT systems control physical machinery (power plants, chemical valves, assembly lines). Immediate, un-tested patching or unexpected device reboots can destabilize control loops, trigger emergency shutdowns, or create physical safety hazards.
2. What is the fundamental priority hierarchy in OT environments compared to traditional IT?
Answer: In OT, human safety and continuous operational availability are primary (Safety > Availability > Integrity > Confidentiality), whereas traditional IT typically prioritizes Confidentiality first, followed by Integrity and Availability.
Operational Technology (OT) Security is a specialized field of cybersecurity focused on protecting systems that manage industrial operations—such as power plants, water treatment facilities, and manufacturing lines. Unlike IT environments that prioritize data, OT systems control physical processes, making their failure or compromise potentially catastrophic. As digital connectivity expands, the convergence of IT and OT increases exposure to cyber threats, necessitating robust and tailored defense mechanisms.
One critical aspect of OT security is managing the interface between industrial systems and cloud infrastructure. As cloud security becomes central to infrastructure management, secure integration with OT systems is essential. At the same time, advanced monitoring tools using AI and ML in cybersecurity can detect subtle anomalies in operational data streams, helping to identify threats before they escalate.
The challenges of securing OT environments are intensified by legacy systems that were not designed with modern security principles in mind. Here, fundamental disciplines like cryptography and identity and access management must be adapted to work reliably within the real-time constraints of industrial networks. Preventing unauthorized access to control systems is as important as educating personnel through cybersecurity awareness programs that address both digital hygiene and operational safety.
When threats breach defenses, timely incident response and forensics ensure that disruptions are minimized and vulnerabilities are identified. Industrial forensics requires deep understanding of process control logic and sensor networks, overlapping with domains such as CPS security. In highly regulated sectors, compliance and governance are shaped by robust cybersecurity policies tailored to operational risk.
Network segmentation and real-time monitoring play a central role in network security for OT systems. They are supported by application security techniques adapted to industrial software and hardware. To proactively identify system weaknesses, organizations often employ ethical hacking strategies, simulating attacks in controlled environments.
The rise of emerging areas in cybersecurity further expands the threat landscape for OT, with sophisticated attacks now targeting critical infrastructure. Integrating threat intelligence feeds allows teams to detect attack trends and adjust defenses accordingly. These insights are increasingly refined using data analysis and visualization tools to make complex patterns more interpretable.
OT Security also benefits from broader data science and analytics applications, which aggregate sensor data and system logs for deeper insights. Supporting techniques such as data cleaning and preprocessing help improve the quality of these insights, while data collection and storage mechanisms provide long-term visibility over equipment behavior. Using advanced tools and technologies, professionals are equipped to automate responses and maintain operational continuity.
As industrial systems evolve, they increasingly rely on domain-specific analytics to detect unusual process behavior, adding another layer of protection. However, implementing these technologies must also consider ethical and social aspects, particularly when automation decisions impact safety or employment. OT Security is therefore not just a technical challenge, but also a multidimensional discipline with operational, societal, and economic implications.
With its convergence of industrial control and cyber defense, Operational Technology Security is central to safeguarding the systems that sustain modern civilization. As technologies advance and threats evolve, this domain demands continuous learning, cross-disciplinary collaboration, and strategic foresight to ensure resilient and secure operations.
This image depicts OT security as the protective layer around real-world industrial operations. On the left, factory towers, tanks, and process equipment represent physical infrastructure controlled by sensors and automated systems. In the center, a large shield with a padlock signals secure control of critical assets, while the surrounding network lines suggest interconnected controllers, HMIs, and field devices. On the right, screens and control-room consoles symbolize monitoring, alarms, and operational oversight, and the presence of power lines highlights links to critical utilities. Small warning triangles and alert symbols convey the risk of disruptions—from cyber intrusions to unsafe system changes. Overall, the picture communicates that OT security is about keeping industrial systems safe, reliable, and resilient while they continue running in real time.
Building Cyber Resilience: Operational Technology (OT) Security Navigation
Discover how Operational Technology Security protects industrial control systems, SCADA networks, and physical critical infrastructure across the Cybersecurity cluster. Each card details ISA/IEC 62443 zones and conduits, PLC hardening, industrial firewalls, and air-gapped monitoring.
Cybersecurity Overview
Presents the overarching macro-architecture, mapping how IT-to-OT convergence boundaries require safety-first defensive controls distinct from traditional IT.
Network Security
Examines industrial network zoning (Purdue Model), data diode unidirectional gateways, and deep packet inspection for SCADA protocols (Modbus, DNP3).
Application Security
Focuses on securing proprietary HMI software, vendor engineering workstation binaries, and industrial firmware validation.
Endpoint Security
Covers hardening SCADA operator terminals, restricting USB media on plant floors, and deploying specialized industrial EDR agents.
Cloud Security
Details secure IT/OT cloud telemetry conduits, preventing direct internet exposure of SCADA historians, and hybrid cloud monitoring gateways.
Identity & Access Management
Governs plant floor engineer jump-box authentication, multi-factor authentication for remote vendor access, and role-based access for control room operators.
Cryptography
Applies secure communication tunnels between remote terminal units (RTUs) and master control stations, protecting telemetry packets against tampering.
Incident Response & Forensics
Orchestrates safety-first OT incident containment playbooks, ensuring emergency network isolation never disrupts physical plant safety interlocks.
Threat Intelligence
Tracks APT campaigns targeting industrial control systems (e.g., Industroyer, Triton), analyzing ICS-specific malware signatures and TTPs.
Ethical Hacking & Pen Testing
Executes non-disruptive penetration testing on simulated industrial control testbeds, probing PLC logic and HMI communication pathways.
Cybersecurity Awareness
Trains plant operators and maintenance engineers in industrial cybersecurity hygiene, social engineering defense, and USB drop awareness.
Policy & Governance
Enforces industrial compliance frameworks (IEC 62443, NERC CIP), safety policies, and mandatory governance rules for critical infrastructure.
CPS Security
Protects the broader cyber-physical control loops spanning smart grids, water treatment pumps, and automated manufacturing robotics.
OT Security
Focuses on industrial control systems (ICS), SCADA, PLCs, Purdue Model segmentation, legacy system hardening, IEC 62443 standards, and operational continuity.
AI & ML in Security
Leverages unsupervised machine learning to baseline industrial sensor signals, detecting subtle physical process anomalies and sensor spoofing.
Emerging Areas
Investigates 5G-enabled industrial networking security, network slicing for OT traffic, and quantum-safe control protocols.
Key Topics in OT Security
Operational Technology security safeguards the physical machinery and control networks powering critical infrastructure:
Protecting Critical Infrastructure
- Scope: Securing energy grids, water treatment plants, transportation networks, and healthcare facilities where cyber disruption causes real-world harm.
- Threats: State-sponsored attacks on power grids (Industroyer) and ransomware paralyzing fuel pipelines (Colonial Pipeline).
Securing Industrial Control Systems (ICS)
- Components: SCADA systems, Distributed Control Systems (DCS), and Programmable Logic Controllers (PLCs) managing physical processes.
- Strategies: Purdue Model network segmentation, rigorous patch testing during scheduled maintenance windows, and OT-tailored incident response.
Industrial IoT (IIoT) & Sensor Security
- Hardening smart sensors, cameras, and actuators via device certificates, mutual authentication, and TLS/IPsec transport encryption.
Applications of OT Security
Real-world operational safeguards across industrial sectors:
- Preventing Manufacturing Plant Attacks: Deploying OT-specific firewalls, application control, and intrusion detection systems to shield legacy machinery from ransomware and sensor spoofing.
- Enhancing Grid & Utility Resilience: Implementing hardware redundancy, rapid failover systems, and rigorous OT penetration testing to maintain continuous power distribution.
Why Study Operational Technology Security
Mastering OT security equips engineers to defend the physical infrastructure sustaining modern society:
- Securing Physical World Systems: Teaches how computational controls govern real-world industrial machinery, energy grids, and manufacturing lines.
- Navigating Unique Constraints: Prepares professionals to operate within legacy hardware limitations where safety and uptime override immediate patching.
- Complying with Industrial Standards: Equips learners to apply ISA/IEC 62443 and NERC CIP compliance frameworks across critical infrastructure projects.
Interactive Quick Review: Industrial Control Security
Reinforce key concepts regarding Purdue Model segmentation, legacy constraints, and IEC 62443 standards before reading the FAQ:
Quick Review Verification
1. How does the Purdue Model of Industrial Control System Network Architecture assist in OT segmentation?
Answer: The Purdue Model stratifies industrial networks into hierarchical levels (from enterprise IT at Level 4/5 down to physical field sensors and PLCs at Level 0). This hierarchical segmentation allows security architects to place industrial firewalls and data diodes between levels, preventing corporate IT threats from cascading into plant-floor control loops.
2. What are compensating controls, and why are they vital when managing unpatchable legacy OT systems?
Answer: Compensating controls are alternative security measures (such as strict network isolation, protocol-aware firewalls, enhanced monitoring, and restricted jump-box access) deployed to protect legacy devices that cannot be rebooted or patched without violating plant uptime and safety requirements.
OT Security – Frequently Asked Questions
What is OT security and how does it differ from IT security?
OT security protects industrial control systems (ICS, SCADA, PLCs) managing physical processes. Unlike IT security which prioritizes data confidentiality, OT security prioritizes human safety and continuous uptime.
Why is OT security critical for critical infrastructure?
Critical infrastructure supplies essential services (power, water, transport). Cyberattacks on OT can cause catastrophic physical damage, environmental contamination, or widespread public disruption.
What are common cyber threats facing OT environments?
Targeted ICS malware (Stuxnet, Industroyer), ransomware locking manufacturing lines, compromised VPN remote access, and unpatched boundary server vulnerabilities.
How does network segmentation improve OT security?
Segmentation divides IT enterprise networks from OT control floors using firewalls and data diodes, restricting lateral movement and malware propagation.
What standards govern OT security compliance?
The primary international standard is ISA/IEC 62443, alongside NERC CIP for North American bulk electric power systems and NIST SP 800-82 guidelines.
How are legacy OT systems secured when patching is impossible?
Through compensating controls: strict network isolation, industrial intrusion detection systems (IDS), rigorous monitoring, and secure jump-box engineering access.
Operational Technology Security: Conclusion
Operational Technology security is vital for protecting the backbone of modern industries and critical infrastructure. As the OT environment becomes more interconnected, implementing robust and adaptive security measures will be essential to address evolving risks and ensure the safety and reliability of industrial operations.
- Safety-First Priority: Design security controls that never compromise human safety or industrial process uptime.
- Purdue Model Zoning: Enforce strict hierarchical network segmentation between IT enterprise systems and OT control floors.
- Compensating Controls: Protect unpatchable legacy PLCs and SCADA nodes with protocol-aware firewalls and passive anomaly monitoring.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is OT security and why is it important for industrial environments?
Answer: OT security protects industrial control systems (ICS/SCADA) governing physical processes. It is vital because breaches endanger human safety, cause environmental hazards, and disrupt critical societal services.
2. How do OT environments differ from traditional IT systems in terms of security requirements?
Answer: OT prioritizes safety and high availability (uptime), whereas IT prioritizes data confidentiality. OT must accommodate legacy hardware, proprietary protocols, and strict real-time response constraints.
3. What are the common threats faced by operational technology systems?
Answer: Targeted malware (Industroyer, Triton), ransomware disrupting manufacturing, unpatched boundary vulnerabilities, and insecure remote vendor access.
4. How does risk management contribute to effective OT security?
Answer: Identifies physical and digital vulnerabilities, prioritizes safeguards based on safety impact, and aligns security investments with industrial operational continuity.
5. What role does network segmentation play in enhancing OT security?
Answer: Isolates plant floor networks from business IT networks using industrial firewalls and data diodes, preventing malware lateral movement and containing threat blast radiuses.
6. How do patch management and system updates impact the security of OT systems?
Answer: Patching closes known software vulnerabilities, but in OT requires careful staging and scheduled maintenance windows to prevent unexpected control loop downtime.
7. What are the challenges of integrating OT security with traditional IT security measures?
Answer: Legacy hardware incompatibility, conflicting operational priorities (uptime vs confidentiality), and the risk that active IT vulnerability scanning tools can crash sensitive PLCs.
8. How do compliance and regulatory requirements influence OT security practices?
Answer: Standards like IEC 62443 and NERC CIP establish mandatory security baselines, risk assessments, and auditing frameworks that critical infrastructure operators must enforce.
9. What strategies can organizations implement to improve threat detection in OT environments?
Answer: Deploying passive industrial intrusion detection systems (IDS) tuned for Modbus/DNP3 protocols and utilizing machine learning for process anomaly baselining.
10. What future trends are expected to shape the evolution of OT security?
Answer: IT/OT convergence, AI-driven predictive threat analytics, Zero Trust industrial micro-segmentation, and secure 5G cellular industrial networking.
Thought-Provoking Architectural Questions
1. How might the convergence of IT and OT networks redefine security strategies in industrial environments?
Answer: Requires unified Zero Trust architectures that bridge enterprise IT identity management with plant-floor industrial firewalls, ensuring corporate compromises cannot propagate into physical control loops.
2. What role can artificial intelligence play in enhancing threat detection and response in OT security?
Answer: AI baselines repetitive industrial sensor loops, instantly spotting subtle command manipulation or physical tampering that static signature rules fail to identify.
3. How might the increasing adoption of IoT devices in industrial settings impact OT security measures?
Answer: Proliferation of IIoT sensors expands the attack surface, requiring automated device certificate enrollment, mutual authentication, and lightweight encryption protocols.
4. What challenges do legacy OT systems present in implementing modern security measures, and how can they be overcome?
Answer: Legacy PLCs lack computational capacity for heavy crypto and cannot be rebooted. Overcome using compensating controls like data diodes, passive IDPS monitoring, and restricted engineering jump-boxes.
5. How can regulatory and compliance requirements drive innovation in OT security practices?
Answer: Mandates for critical infrastructure resilience force vendors and asset owners to innovate secure-by-design industrial hardware, automated compliance auditing, and standardized zoning.
6. What ethical considerations arise when deploying advanced monitoring technologies in OT environments?
Answer: Balancing deep packet inspection and operator workstation monitoring with worker privacy rights and operational transparency.
7. How might the integration of blockchain technology enhance the security and integrity of OT networks?
Answer: Provides tamper-proof audit ledgers for recording PLC firmware updates, configuration changes, and supply chain sensor telemetry across distributed industrial nodes.
8. What future trends could redefine the landscape of OT security in the next decade?
Answer: Autonomous cyber-physical self-healing networks, quantum-safe industrial protocols, and widespread adoption of 5G private cellular networks for plant floor automation.
9. How can organizations measure the effectiveness of their OT security programs beyond traditional metrics?
Answer: Measuring physical process resilience, mean time to isolate an anomalous control loop, safety interlock verification frequency, and cyber-physical tabletop drill scoring.
10. What are the potential cost implications of failing to secure OT environments?
Answer: Catastrophic physical equipment destruction, multi-million dollar production downtime, environmental disaster liability, and regulatory penalties.
11. How can cross-industry collaboration drive innovation in OT security solutions?
Answer: Sharing sector-specific ICS threat intelligence through ISACs, contributing to open-source OT protocol dissectors, and standardizing security architectures.
12. How might emerging regulatory changes impact the future development of OT security standards?
Answer: Governments will enforce mandatory cyber incident reporting timelines and baseline security requirements for all critical infrastructure suppliers.
Numerical Engineering Problems & Solutions
Problem 1: Compromised Device Reduction via Security Upgrades
An OT network has 1,500 industrial control devices, with 3% (0.03) compromised due to legacy vulnerabilities. Calculate initial compromised devices. A security upgrade reduces vulnerabilities by 80%. Calculate remaining compromised devices and absolute reduction.
An OT network has 1,500 industrial control devices, with 3% (0.03) compromised due to legacy vulnerabilities. Calculate initial compromised devices. A security upgrade reduces vulnerabilities by 80%. Calculate remaining compromised devices and absolute reduction.
Solution:
- Initial compromised devices = 1,500 × 0.03 = 45 devices
- Remaining compromised devices (80% reduction) = 45 × (1 – 0.80) = 45 × 0.20 = 9 devices
- Absolute reduction = 45 – 9 = 36 devices secured
Problem 2: SCADA Signal Traffic Surge During Attack
A SCADA system processes 200,000 control signals per day. A volumetric DDoS attack increases signal traffic by 25%. Calculate additional signals per day, total signals processed during the attack, and percentage increase.
A SCADA system processes 200,000 control signals per day. A volumetric DDoS attack increases signal traffic by 25%. Calculate additional signals per day, total signals processed during the attack, and percentage increase.
Solution:
- Additional signal traffic = 200,000 × 0.25 = 50,000 additional signals/day
- Total signals during attack = 200,000 + 50,000 = 250,000 signals/day
- Percentage increase = (50,000 / 200,000) × 100 = 25.0%
Problem 3: Vulnerability Scanning Duration & Speed Acceleration
An OT vulnerability scan takes 40 minutes for 500 devices. Calculate scanning rate per device in minutes. Estimate time required to scan 2,000 devices. Calculate new scan duration if an upgraded scanner increases speed by 50% (1.5x throughput) and time saved.
An OT vulnerability scan takes 40 minutes for 500 devices. Calculate scanning rate per device in minutes. Estimate time required to scan 2,000 devices. Calculate new scan duration if an upgraded scanner increases speed by 50% (1.5x throughput) and time saved.
Solution:
- Scanning rate per device = 40 minutes / 500 devices = 0.08 minutes/device (4.8 seconds)
- Time for 2,000 devices = 2,000 × 0.08 = 160 minutes
- New scan time with 50% speed increase = 160 minutes / 1.50 ≈ 106.67 minutes
- Time saved = 160 – 106.67 ≈ 53.33 minutes saved
Problem 4: OT Security Event Log Volume Metrics
An OT security system logs 300 events per minute. Telemetry indicates that 0.5% (0.005) indicate potential security threats. Calculate threat events per minute, per hour (60 minutes), and per day (24 hours).
An OT security system logs 300 events per minute. Telemetry indicates that 0.5% (0.005) indicate potential security threats. Calculate threat events per minute, per hour (60 minutes), and per day (24 hours).
Solution:
- Threat events per minute = 300 × 0.005 = 1.5 threat events/min
- Threat events per hour = 1.5 × 60 = 90 threat events/hour
- Threat events per day = 90 × 24 = 2,160 threat events/day
Problem 5: Annual Downtime Cost Savings from OT Security Measures
An unmitigated OT breach incurs $1,200,000 in annual downtime losses. Investing $500,000 in OT security measures reduces downtime losses by 70%. Calculate annual downtime cost after improvement and net annual savings.
An unmitigated OT breach incurs $1,200,000 in annual downtime losses. Investing $500,000 in OT security measures reduces downtime losses by 70%. Calculate annual downtime cost after improvement and net annual savings.
Solution:
- Downtime cost after 70% reduction = $1,200,000 × (1 – 0.70) = $1,200,000 × 0.30 = $360,000/year
- Gross annual savings = $1,200,000 – $360,000 = $840,000/year
- Net financial savings = $840,000 – $500,000 (security investment) = $340,000
Problem 6: Patch Management Vulnerability Reduction Metrics
A patch management initiative reduces industrial system vulnerabilities by 85% from an initial count of 400 vulnerabilities. Calculate number of vulnerabilities fixed, remaining vulnerabilities, and reduction percentage.
A patch management initiative reduces industrial system vulnerabilities by 85% from an initial count of 400 vulnerabilities. Calculate number of vulnerabilities fixed, remaining vulnerabilities, and reduction percentage.
Solution:
- Vulnerabilities fixed = 400 × 0.85 = 340 vulnerabilities fixed
- Remaining vulnerabilities = 400 – 340 = 60 vulnerabilities
- Reduction percentage = (340 / 400) × 100 = 85.0%
Problem 7: OT Network Security Log Audit Volume
A network security audit reviews 10,000 network logs per day. If 2% (0.02) of logs require further investigation, calculate flagged logs per day, weekly (7 days), and monthly (30 days).
A network security audit reviews 10,000 network logs per day. If 2% (0.02) of logs require further investigation, calculate flagged logs per day, weekly (7 days), and monthly (30 days).
Solution:
- Flagged logs per day = 10,000 × 0.02 = 200 logs/day
- Flagged logs per week (7 days) = 200 × 7 = 1,400 logs/week
- Flagged logs per month (30 days) = 200 × 30 = 6,000 logs/month
Problem 8: Intrusion Detection System Accuracy & Error Rate
An industrial Intrusion Detection System (IDS) maintains an accuracy rate of 95% (0.95) while processing 800,000 network events per day. Calculate accurately processed events, error event count, and daily error rate percentage.
An industrial Intrusion Detection System (IDS) maintains an accuracy rate of 95% (0.95) while processing 800,000 network events per day. Calculate accurately processed events, error event count, and daily error rate percentage.
Solution:
- Accurately processed events = 800,000 × 0.95 = 760,000 events
- Error events = 800,000 – 760,000 = 40,000 error events
- Daily error rate = (40,000 / 800,000) × 100 = 5.0%
Problem 9: Brute-Force Feasibility for 128-Bit Encrypted OT Tunnels
A secure OT network tunnel uses 128-bit encryption (2^128 possible keys). A cracking cluster tests 10^9 keys per second. Calculate total time required in seconds and convert to years using 3.15 × 10^7 seconds per year.
A secure OT network tunnel uses 128-bit encryption (2^128 possible keys). A cracking cluster tests 10^9 keys per second. Calculate total time required in seconds and convert to years using 3.15 × 10^7 seconds per year.
Solution:
- Total possible keys = 2^128 ≈ 3.4028 × 10^38 keys
- Time in seconds = (3.4028 × 10^38) / 10^9 = 3.4028 × 10^29 seconds
- Time in years = (3.4028 × 10^29) / (3.15 × 10^7) ≈ 1.08 × 10^22 years
Problem 10: OT Incident Response Recovery Time Acceleration
An OT incident response team reduces recovery time from 120 minutes to 45 minutes per incident. For 15 incidents per year, calculate total time saved annually in minutes and convert into hours.
An OT incident response team reduces recovery time from 120 minutes to 45 minutes per incident. For 15 incidents per year, calculate total time saved annually in minutes and convert into hours.
Solution:
- Time saved per incident = 120 min – 45 min = 75 minutes saved/incident
- Total time saved annually = 15 incidents × 75 minutes = 1,125 minutes/year
- Convert minutes to hours = 1,125 / 60 = 18.75 hours/year
Problem 11: Lateral Movement Risk Reduction via Network Segmentation
A network segmentation project divides an OT network into 5 distinct security zones, reducing lateral movement risk by 80%. If an initial unsegmented breach could potentially affect 500 control devices, calculate potential devices affected after segmentation and absolute device reduction.
A network segmentation project divides an OT network into 5 distinct security zones, reducing lateral movement risk by 80%. If an initial unsegmented breach could potentially affect 500 control devices, calculate potential devices affected after segmentation and absolute device reduction.
Solution:
- Expected devices affected after segmentation = 500 devices × (1 – 0.80) = 500 × 0.20 = 100 devices
- Absolute device reduction = 500 – 100 = 400 devices protected from lateral spread
Problem 12: Incident Response Drill Time Optimization
An incident response drill takes 45 minutes per exercise. A company conducts 10 drills per quarter (40 drills per year). Calculate total annual drill time before improvements. If improvements cut drill time by 33%, calculate new drill duration and annual hours saved.
An incident response drill takes 45 minutes per exercise. A company conducts 10 drills per quarter (40 drills per year). Calculate total annual drill time before improvements. If improvements cut drill time by 33%, calculate new drill duration and annual hours saved.
Solution:
- Total drills per year = 10 drills/quarter × 4 quarters = 40 drills/year
- Total annual drill time before = 40 drills × 45 minutes = 1,800 minutes (30 hours)
- New drill duration (33% reduction) = 45 minutes × (1 – 0.33) = 45 × 0.67 = 30.15 minutes/drill
- Total new annual drill time = 40 drills × 30.15 minutes = 1,206 minutes (20.1 hours)
- Annual time saved = 1,800 – 1,206 = 594 minutes saved (9.9 hours/year)
Operational Technology Security — Summary & Wrap-Up
Operational Technology (OT) security safeguards the critical industrial infrastructure that underpins modern civilization—spanning power grids, water treatment plants, smart manufacturing, and transportation networks. By prioritizing human safety and operational availability above all else, enforcing hierarchical Purdue Model network segmentation, deploying protocol-aware firewalls, and managing legacy constraints with robust compensating controls, security professionals ensure that physical industrial systems remain resilient against evolving cyber threats.