
Prepare for University Studies & Career Advancement

CPS Security

Cyber-Physical Systems (CPS) Education is where code learns humility—because here, software touches the physical world. The diagram makes that relationship explicit. Learners bring in inputs such as technical foundations and guided materials, but their work is shaped by controls that are more than “best practice”: safety regulations and security protocols that exist because failures have real consequences. With mechanisms such as expert instruction and simulation tools, students explore how sensors, networks, and controllers cooperate—and how they can also betray one another through delay, noise, misconfiguration, or attack. The output is a learner who can think in systems, not parts: designing feedback loops that remain stable, integrating components without creating hidden hazards, and treating security as a safety issue rather than a separate topic. In short, the function captured here is the formation of sound judgment at the boundary where digital decisions become physical outcomes.
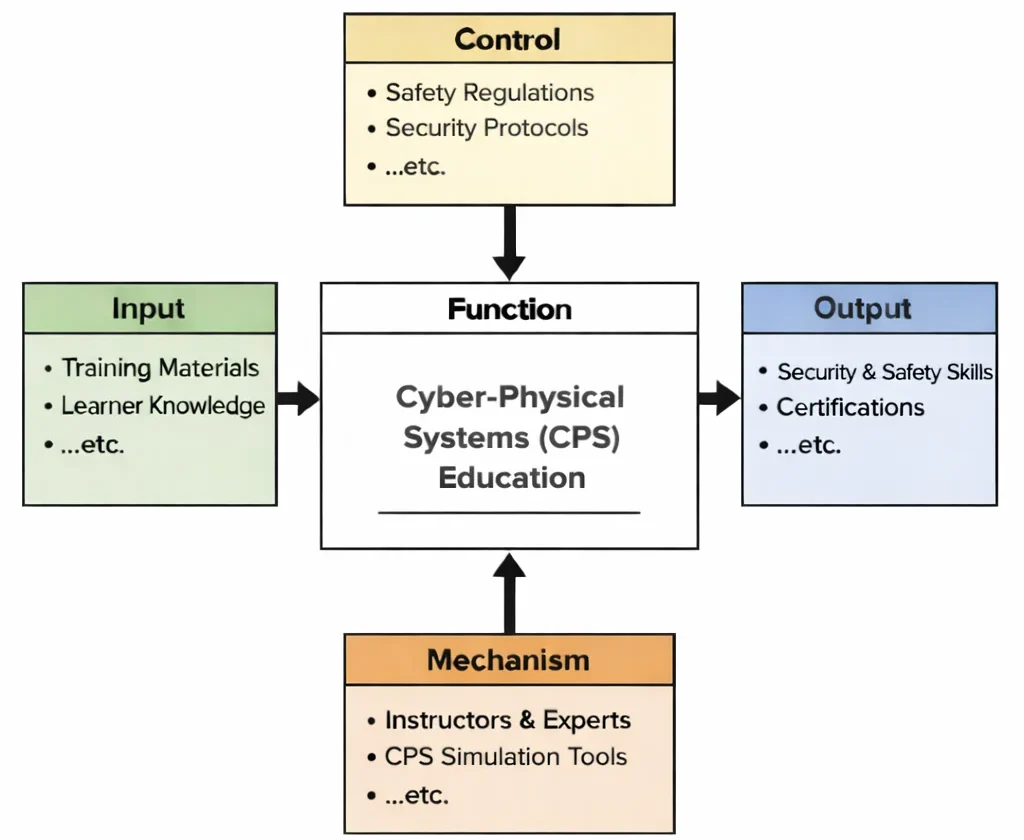
IDEF0 diagram of Cyber-Physical Systems (CPS) Education showing Inputs, Controls, Outputs, and Mechanisms feeding a central “Function” learning process.
Cyber-Physical Systems (CPS) Education in IDEF0 form: regulated, tool-enabled learning that builds safety-and-security thinking for real systems.

This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Cyber-Physical Systems (CPS) Education as a structured transformation process. Inputs include training materials and foundational learner knowledge in computing and physical systems. Controls include safety regulations, security protocols, standards, and curriculum requirements that govern how CPS designs are evaluated. Mechanisms include instructors, experts, and CPS simulation tools or lab environments that support hands-on experimentation with sensors, actuators, feedback loops, and networked control. Outputs include learners who develop practical CPS competence, including safety-aware design, secure integration of cyber and physical components, and the ability to reason about reliability, latency, failure modes, and risk.

Cyber-Physical Systems (CPS) represent the convergence of computational technologies with physical processes, giving rise to interconnected systems found in energy grids, manufacturing plants, medical devices, and transportation networks. These systems are highly reliant on secure networking and robust infrastructure, underscoring the relevance of networking and connectivity in the cloud and principles from security, compliance, and identity management. As the cyber layer grows increasingly complex, cybersecurity practices must adapt to meet the distinct real-time and safety-critical requirements of CPS.

Key to CPS Security is the integration of cryptography and identity and access management, which help ensure data integrity and prevent unauthorized control of physical assets. This becomes especially vital in systems that require continuous availability, emphasizing the importance of performance tuning and high availability infrastructure. Technologies such as serverless computing and containerization offer scalable platforms but introduce new security considerations.

Given that CPS often function in environments with limited direct user interaction, monitoring and adaptive response systems are critical. These include incident response and forensics, threat intelligence, and the deployment of AI and ML in cybersecurity. These advanced analytics tools, grounded in principles from data science and big data analytics, help detect anomalies across sensor networks and control systems.

Securing CPS environments also means reinforcing perimeter defense through specialized domains like endpoint security, network security, and operational technology security. These are essential for mitigating threats in systems that interact with the physical world. Meanwhile, disciplines like application security and DevOps practices must evolve to include security-by-design principles from the earliest stages of CPS deployment.

Because vulnerabilities in CPS can lead to physical harm, it is essential to develop a proactive security culture. Training programs that enhance cybersecurity awareness and adherence to established cybersecurity policies can reduce the risk of human error and insider threats. In parallel, practices such as ethical hacking can be employed to test system resilience and uncover hidden flaws before attackers do.

Emerging trends, including edge computing and new areas in cybersecurity, further complicate the CPS landscape. These technologies offer performance benefits but may expand the attack surface, especially when deployed in remote or industrial environments. Thus, securing CPS involves not only hardening the system’s core but also addressing its evolving ecosystem and digital dependencies.
Futuristic factory and smart-city industrial landscape with robotic arms and connected machines, centered on a glowing shield-and-padlock icon representing cybersecurity for cyber-physical systems.
CPS Security: safeguarding connected factories, sensors, and industrial control systems in the real world.


This illustration portrays cyber-physical systems (CPS) security as the protection of digital networks that directly control physical equipment. A radiant shield with a padlock hovers above an advanced industrial scene—robotic arms, automated production lines, and connected modules—signaling secure control and trusted communication. Streams of light and network nodes suggest data flowing between sensors, controllers, and cloud-like analytics, while the large-scale plants and infrastructure emphasize the high stakes of reliability and safety. The image fits an introductory CPS security page by highlighting the core challenge: defending interconnected machines and industrial operations from intrusion, disruption, and manipulation while keeping systems resilient and continuously monitored.

Table of Contents

Key Topics in CPS Security

  1. Securing Smart Grids:

    • What Are Smart Grids?:
      • Intelligent electrical grids that use sensors, IoT devices, and data analytics to optimize electricity generation, distribution, and consumption.
    • Threats:
      • Cyberattacks targeting power plants, substations, or grid control systems.
      • Examples: Malware (e.g., BlackEnergy), ransomware attacks, or unauthorized access.
    • Security Measures:
      • Implement robust encryption for communication between devices.
      • Use anomaly detection systems to identify unusual grid behavior.
      • Conduct regular penetration testing of grid systems.
  2. Securing Autonomous Vehicles:

    • What It Involves:
      • Protecting the complex systems of self-driving cars, including their sensors (e.g., LiDAR, cameras), GPS modules, and software.
    • Threats:
      • Spoofing attacks on GPS to misdirect vehicles.
      • Malware in vehicle software compromising control systems.
      • Denial of Service (DoS) attacks disabling key functionalities.
    • Security Measures:
      • Use secure communication protocols for vehicle-to-vehicle (V2V) and vehicle-to-infrastructure (V2I) communications.
      • Implement over-the-air (OTA) software updates with authentication mechanisms.
      • Use fail-safe systems to maintain control during cyberattacks.
  3. Securing Medical Devices:

    • What It Involves:
      • Protecting devices like pacemakers, insulin pumps, and diagnostic tools from cyber threats.
    • Threats:
      • Unauthorized access to device settings, potentially harming patients.
      • Data breaches compromising sensitive patient information.
    • Security Measures:
      • Encrypt communication between devices and healthcare networks.
      • Implement strong authentication for accessing device settings.
      • Use real-time monitoring to detect and respond to potential threats.
  4. Ensuring Safety and Reliability in CPS Operations:

    • Importance:
      • Cyberattacks on CPS can lead to physical damage, safety risks, and system failures.
    • Techniques:
      • Redundancy: Use backup systems to maintain operations during attacks.
      • Real-Time Monitoring: Continuously monitor system behavior to detect anomalies.
      • Resilience Engineering: Design systems to recover quickly from disruptions.

Applications of CPS Security

  1. Protecting Self-Driving Cars from Cyber Threats:

    • Challenges:
      • Real-time decision-making requires secure and reliable data inputs from sensors and external sources.
      • The interconnected nature of autonomous vehicles makes them vulnerable to attacks targeting communication systems.
    • Solutions:
      • Use intrusion detection systems (IDS) to monitor vehicle networks for unusual activity.
      • Implement secure boot mechanisms to ensure that only trusted software runs on vehicle systems.
      • Regularly update vehicle software with patches for known vulnerabilities.
  2. Securing Healthcare Devices Like Pacemakers:

    • Challenges:
      • Wireless communication between devices and healthcare providers introduces vulnerabilities.
      • Compromised devices can lead to incorrect functioning or leaks of sensitive patient data.
    • Solutions:
      • Use end-to-end encryption for all device communications.
      • Conduct regular security assessments and vulnerability scans.
      • Train healthcare professionals on best practices for device security.

Emerging Trends in CPS Security

  1. Zero Trust for CPS:

    • What It Entails:
      • A “never trust, always verify” approach to securing CPS environments.
    • Applications:
      • Enforcing strict access controls for every device, user, and system.
      • Using continuous authentication and monitoring.
  2. Artificial Intelligence (AI) in CPS Security:

    • Role of AI:
      • AI systems can analyze large volumes of CPS data to detect patterns of cyberattacks.
      • Machine learning models can predict vulnerabilities and recommend mitigation strategies.
    • Example:
      • AI-powered threat detection in smart grids to prevent power outages caused by cyberattacks.
  3. Blockchain for Secure CPS Communication:

    • How It Helps:
      • Provides a decentralized and tamper-proof method for recording CPS transactions and communication logs.
    • Applications:
      • Securing supply chain data in manufacturing CPS.
      • Enabling trust in autonomous vehicle communications.
  4. Edge Computing for Real-Time CPS Security:

    • Why It’s Important:
      • CPS often require real-time decisions that cloud-based systems may not handle efficiently.
    • Applications:
      • Using edge devices with built-in security features to process data locally and reduce latency.

Challenges in CPS Security

  1. Complexity of CPS:

    • CPS often involve multiple interconnected components, making them difficult to secure comprehensively.
    • Solution: Develop modular security strategies tailored to specific components.
  2. Evolving Threat Landscape:

    • Attackers continually adapt, exploiting new vulnerabilities in CPS.
    • Solution: Regularly update systems and conduct threat intelligence analysis.
  3. Integration of Legacy Systems:

    • Many CPS rely on outdated technology that lacks modern security features.
    • Solution: Use security gateways to shield legacy systems from external threats.
  4. Balancing Security and Performance:

    • Adding security features can impact CPS performance, particularly in real-time systems.
    • Solution: Implement lightweight security protocols designed for CPS.

Tools and Technologies for CPS Security

  1. Intrusion Detection and Prevention Systems:

    • Tools: Snort, Zeek, Suricata.
    • Application: Monitoring traffic in CPS networks for anomalies.
  2. Secure Communication Protocols:

    • Tools: MQTT with TLS, CoAP.
    • Application: Encrypting data transmission between IoT devices and control systems.
  3. Threat Modeling Tools:

    • Tools: Microsoft Threat Modeling Tool, OWASP Threat Dragon.
    • Application: Identifying potential threats during CPS design.
  4. Real-Time Monitoring Solutions:

    • Tools: Splunk, Nagios.
    • Application: Monitoring system health and detecting suspicious behavior.

Benefits of CPS Security

Protects Human Lives:

Prevents cyberattacks on critical systems like healthcare devices and transportation networks.

Ensures Operational Continuity:

Safeguards against downtime caused by cyber incidents.

Enhances Trust and Adoption:

Encourages the adoption of CPS technologies by ensuring robust security.


Why Study CPS Security

Protecting the Integration of Physical and Digital Worlds

Cyber-Physical Systems (CPS) are systems where physical processes are tightly integrated with computational and communication elements. These include critical infrastructures such as smart grids, autonomous vehicles, industrial control systems, and healthcare devices. For students preparing for university, studying CPS security offers vital insight into how the protection of physical systems increasingly depends on robust cybersecurity measures.

Understanding the Unique Challenges of CPS Environments

Unlike traditional IT systems, CPS must maintain real-time responsiveness, reliability, and safety. Students explore how CPS systems are constrained by hardware, exposed to physical tampering, and susceptible to timing attacks and sensor spoofing. Understanding these constraints helps learners design security mechanisms that protect both data and the physical world from malicious interference.

Exploring Real-World Applications and Threat Scenarios

CPS security is crucial in contexts such as energy grids, traffic control systems, robotics, medical devices, and automated manufacturing. Students study real-world attacks like the Stuxnet worm and GPS spoofing, learning how such incidents can cause physical damage or public safety hazards. These case studies highlight the high stakes and real-world impact of cybersecurity in CPS domains.

Developing Interdisciplinary Problem-Solving Skills

CPS security requires knowledge from multiple disciplines including computer science, electrical engineering, control theory, and embedded systems. Students learn to approach problems from both a cyber and physical perspective, combining skills in secure communication, hardware integrity, system modeling, and safety assurance. This interdisciplinary thinking is key to securing increasingly complex and interconnected systems.

Preparing for Emerging Roles in Secure Infrastructure and Automation

A strong foundation in CPS security supports further study in areas such as industrial cybersecurity, embedded systems design, critical infrastructure protection, and autonomous system safety. It also opens doors to careers in sectors like energy, defense, transportation, and healthcare. For university-bound learners, studying CPS security provides the tools to help protect the infrastructure and technologies that modern society depends on.
 

Cyber-Physical Systems Security – Frequently Asked Questions

These FAQs introduce core ideas, threats, defences, and career paths in cyber-physical systems security, helping you connect cybersecurity concepts with real-world infrastructure and control systems.

What is cyber-physical systems (CPS) security?

Cyber-physical systems (CPS) security focuses on protecting systems that tightly integrate computation, communication, and physical processes, such as smart grids, industrial control systems, autonomous vehicles, medical devices, and smart buildings. It covers both cybersecurity of the digital components and safety of the physical processes to ensure that attacks cannot cause equipment damage, service disruption, or harm to people and the environment.

Why is CPS security important in modern infrastructure and industry?

CPS security is crucial because many critical infrastructures now rely on connected control systems to run power grids, transport networks, factories, and healthcare devices. A successful attack on these systems can cause cascading failures, physical damage, safety incidents, and long-lasting service outages, far beyond the data theft typical of traditional IT breaches. Securing CPS protects public safety, economic stability, and the reliability of essential services that societies depend on every day.

How does CPS security differ from traditional IT security?

CPS security extends traditional IT security by considering both digital assets and the physical processes they control. While IT security focuses mainly on confidentiality, integrity, and availability of information, CPS security also emphasises real-time control, safety, reliability, and resilience under strict timing and performance constraints. Defences for CPS must work with legacy industrial protocols, constrained devices, and safety standards, often requiring multidisciplinary knowledge of control engineering, networking, and security.

What are common threats and attack types against cyber-physical systems?

Common CPS threats include unauthorised remote access to controllers, manipulation of sensor readings, command injection into industrial protocols, denial-of-service attacks on control networks, and malware targeting programmable logic controllers (PLCs) or embedded devices. Attackers may try to subtly change setpoints, disable safety interlocks, spoof measurements, or cause equipment to operate outside safe limits. Because CPS directly affect the physical world, these attacks can lead to equipment damage, production losses, safety incidents, and environmental harm if not detected and mitigated quickly.

What security measures are used to protect cyber-physical systems?

CPS protection uses layered security measures such as network segmentation, secure gateways between IT and operational technology (OT), strong authentication for engineers and devices, and encryption for remote access and management channels. Engineers also deploy anomaly detection, safety interlocks, and redundancy in sensors and actuators to detect and limit the impact of malicious or faulty commands. Good security architecture combines traditional controls like firewalls with CPS-specific techniques such as secure control protocols, whitelisting of commands, and continuous monitoring of process behaviour for early warning signs of attack.

How do safety and security interact in cyber-physical systems?

In cyber-physical systems, safety and security are tightly linked because a security breach can turn into a safety incident if physical processes are driven into unsafe states. Engineers must ensure that safety mechanisms, such as emergency stops, alarms, and fail-safe modes, remain effective even if the digital components are compromised. Modern CPS design aims for security-informed safety, where threat modelling, secure communication, and robust control logic are integrated with traditional safety engineering to prevent accidents caused by both faults and deliberate attacks.

What skills do students need to work in CPS security?

Students interested in CPS security benefit from a mix of skills in networking, embedded systems, control theory, operating systems, and cybersecurity fundamentals. They should understand industrial protocols, real-time constraints, and basic control loop behaviour, as well as common security practices such as access control, cryptography, and incident response. Laboratory experience with microcontrollers, industrial simulators, and security tools, combined with coursework in systems engineering, helps prepare graduates for roles in critical infrastructure, manufacturing, transport, and smart city projects.

Which industries and career paths involve cyber-physical systems security?

Cyber-physical systems security plays a central role in sectors such as energy and smart grids, water treatment, manufacturing and industrial automation, transport and autonomous vehicles, healthcare devices, and building management systems. Career paths include OT security engineer, industrial control systems security specialist, critical infrastructure security analyst, CPS researcher, and security architect for smart systems. As more devices and infrastructure become connected, demand is growing for professionals who can understand both the engineering and security aspects of CPS and design robust, resilient systems for the future.

Cyber-Physical Systems (CPS) Security: Conclusion

Cyber-Physical Systems security is vital for the safe and reliable operation of systems that directly impact human lives and critical infrastructure. By implementing advanced security measures and staying ahead of emerging threats, organizations can protect these complex and interconnected systems from evolving cyber risks.
Cyber-Physical Systems (CPS) Education is where code learns humility—because here, software touches the physical world. The diagram makes that relationship explicit. Learners bring in inputs such as technical foundations and guided materials, but their work is shaped by controls that are more than “best practice”: safety regulations and security protocols that exist because failures have real consequences. With mechanisms such as expert instruction and simulation tools, students explore how sensors, networks, and controllers cooperate—and how they can also betray one another through delay, noise, misconfiguration, or attack. The output is a learner who can think in systems, not parts: designing feedback loops that remain stable, integrating components without creating hidden hazards, and treating security as a safety issue rather than a separate topic. In short, the function captured here is the formation of sound judgment at the boundary where digital decisions become physical outcomes.
IDEF0 diagram of Cyber-Physical Systems (CPS) Education showing Inputs, Controls, Outputs, and Mechanisms feeding a central “Function” learning process.
Cyber-Physical Systems (CPS) Education in IDEF0 form: regulated, tool-enabled learning that builds safety-and-security thinking for real systems.
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Cyber-Physical Systems (CPS) Education as a structured transformation process. Inputs include training materials and foundational learner knowledge in computing and physical systems. Controls include safety regulations, security protocols, standards, and curriculum requirements that govern how CPS designs are evaluated. Mechanisms include instructors, experts, and CPS simulation tools or lab environments that support hands-on experimentation with sensors, actuators, feedback loops, and networked control. Outputs include learners who develop practical CPS competence, including safety-aware design, secure integration of cyber and physical components, and the ability to reason about reliability, latency, failure modes, and risk.

Interactive Check: Intro & System Concepts

Verify your understanding of how cyber and physical components interact under strict safety and security constraints:

Introductory Concept Verification

1. Why is security in Cyber-Physical Systems fundamentally a matter of physical safety?
Answer: Unlike traditional IT systems where a security breach compromises data confidentiality or integrity, CPS software directly commands physical machinery (such as power grids, autonomous vehicles, and medical devices). Consequently, a cyber exploit can cause physical equipment destruction, environmental hazards, or human injury.
2. What role do “Controls” play in the IDEF0 CPS Education model?
Answer: Controls—such as safety regulations, real-time control constraints, and industry security protocols—govern how CPS designs are evaluated, ensuring learners design feedback loops that remain stable and hazard-free under attack.

Cyber-Physical Systems (CPS) represent the convergence of computational technologies with physical processes, giving rise to interconnected systems found in energy grids, manufacturing plants, medical devices, and transportation networks. These systems are highly reliant on secure networking and robust infrastructure, underscoring the relevance of networking and connectivity in the cloud and principles from security, compliance, and identity management. As the cyber layer grows increasingly complex, cybersecurity practices must adapt to meet the distinct real-time and safety-critical requirements of CPS.
Key to CPS Security is the integration of cryptography and identity and access management, which help ensure data integrity and prevent unauthorized control of physical assets. This becomes especially vital in systems that require continuous availability, emphasizing the importance of performance tuning and high availability infrastructure. Technologies such as serverless computing and containerization offer scalable platforms but introduce new security considerations.
Given that CPS often function in environments with limited direct user interaction, monitoring and adaptive response systems are critical. These include incident response and forensics, threat intelligence, and the deployment of AI and ML in cybersecurity. These advanced analytics tools, grounded in principles from data science and big data analytics, help detect anomalies across sensor networks and control systems.
Securing CPS environments also means reinforcing perimeter defense through specialized domains like endpoint security, network security, and operational technology security. These are essential for mitigating threats in systems that interact with the physical world. Meanwhile, disciplines like application security and DevOps practices must evolve to include security-by-design principles from the earliest stages of CPS deployment.
Because vulnerabilities in CPS can lead to physical harm, it is essential to develop a proactive security culture. Training programs that enhance cybersecurity awareness and adherence to established cybersecurity policies can reduce the risk of human error and insider threats. In parallel, practices such as ethical hacking can be employed to test system resilience and uncover hidden flaws before attackers do.
Emerging trends, including edge computing and new areas in cybersecurity, further complicate the CPS landscape. These technologies offer performance benefits but may expand the attack surface, especially when deployed in remote or industrial environments. Thus, securing CPS involves not only hardening the system’s core but also addressing its evolving ecosystem and digital dependencies.
CPS Security: safeguarding connected factories, sensors, and industrial control systems in the real world.
This illustration portrays cyber-physical systems (CPS) security as the protection of digital networks that directly control physical equipment. A radiant shield with a padlock hovers above an advanced industrial scene—robotic arms, automated production lines, and connected modules—signaling secure control and trusted communication. Streams of light and network nodes suggest data flowing between sensors, controllers, and cloud-like analytics, while the large-scale plants and infrastructure emphasize the high stakes of reliability and safety. The image fits an introductory CPS security page by highlighting the core challenge: defending interconnected machines and industrial operations from intrusion, disruption, and manipulation while keeping systems resilient and continuously monitored.

Building Cyber Resilience: CPS Security Navigation

Discover how Cyber-Physical Systems (CPS) Security establishes safety interlocks, embedded cryptographic signatures, and real-time sensor validation across the Cybersecurity cluster. Each card details smart grid substation hardening, vehicle-to-everything (V2X) authentication, medical device isolation, and industrial control resilience.

Cybersecurity Overview

Presents the overall system architecture, mapping how digital cybersecurity controls interface directly with physical sensors, actuators, and safety-critical actuators.

Network Security

Examines industrial protocol firewalls (Modbus, DNP3, IEC 60870-5-104), deep packet inspection, and air-gapped network segmentation.

Application Security

Focuses on secure firmware validation, bounds checking on sensor inputs, preventing command injection in embedded HMI software, and signed OTA updates.

Cloud Security

Details securing cloud-based SCADA data historians, IoT telemetry ingestion pipelines, and multi-tenant smart city cloud management platforms.

Endpoint Security

Covers hardening embedded real-time operating systems (RTOS), microcontroller memory protection, and secure boot mechanisms on physical controllers.

Identity & Access Management

Governs cryptographic device certificates (X.509), hardware Trusted Platform Modules (TPM), and strict role-based access for field engineers modifying PLC logic.

Cryptography

Applies lightweight cryptographic ciphers optimized for resource-constrained microcontrollers, secure message authentication codes (MAC), and encrypted sensor buses.

Incident Response & Forensics

Orchestrates emergency physical shutdown playbooks, controller memory dump extraction, and forensic analysis of PLC ladder logic modifications.

Threat Intelligence

Tracks advanced persistent threat (APT) groups targeting critical infrastructure (e.g., Industroyer/CrashOverride), analyzing campaign TTPs against power grids.

Ethical Hacking & Pen Testing

Executes controlled penetration tests on smart grid simulators and connected vehicle testbeds, discovering sensor spoofing and GPS relay vulnerabilities.

Cybersecurity Awareness

Trains plant operators, biomedical engineers, and transit technicians to recognize physical tampering, USB drop attacks, and social engineering targeting SCADA networks.

Policy & Governance

Enforces critical infrastructure security standards (NIST SP 800-82, IEC 62443, NERC CIP), regulatory compliance, and mandatory safety-critical audit logging.

CPS Security

Focuses on smart grid resilience, autonomous vehicle V2X authentication, medical device isolation, safety-critical interlocks, and real-time control loop protection.

OT Security

Secures industrial control system (ICS) hardware, programmable logic controllers (PLCs), distributed control systems (DCS), and manufacturing floor automation.

AI & ML in Security

Leverages real-time machine learning models to detect physical sensor anomaly manipulation, acoustic tampering, and unauthorized actuator overrides.

Emerging Areas

Investigates quantum-safe cryptography for smart grids, blockchain-backed autonomous vehicle ledgers, and edge-AI resilient robotics.

Key Topics in CPS Security

Cyber-Physical Systems (CPS) combine computation, networking, and physical actuators. Protecting them requires addressing distinct industrial verticals:
  1. Securing Smart Grids

    • What Are Smart Grids?: Intelligent electrical grids utilizing IoT sensors and real-time telemetry to optimize power distribution.
    • Threats: Cyberattacks targeting substations or grid control centers (e.g., malware like BlackEnergy, ransomware, unauthorized telemetry tampering).
    • Security Measures: Robust protocol encryption, anomaly detection systems flagging unusual grid frequency behavior, and rigorous penetration testing.
  2. Securing Autonomous Vehicles

    • What It Involves: Protecting self-driving automobile sensor suites (LiDAR, cameras, radar), GPS modules, and drive-by-wire control software.
    • Threats: GPS spoofing attacks misdirecting vehicles, malicious firmware injections, and denial-of-service attacks disrupting braking or steering actuators.
    • Security Measures: Authenticated vehicle-to-vehicle (V2V) and vehicle-to-infrastructure (V2I) protocols, secure OTA firmware updates, and hardware fail-safe overrides.
  3. Securing Medical Devices

    • What It Involves: Protecting embedded healthcare units (pacemakers, insulin pumps, diagnostic monitors) from remote wireless tampering.
    • Threats: Unauthorized wireless access to device pacing settings and data breaches leaking sensitive patient health records.
    • Security Measures: End-to-end device encryption, strong multi-factor authentication for clinical programmers, and real-time wireless telemetry monitoring.
  4. Ensuring Safety and Reliability in CPS Operations

    • Importance: Cyberattacks on CPS can lead to catastrophic physical damage, environmental hazards, and loss of human life.
    • Techniques: Physical hardware redundancy, real-time sensor cross-validation, and resilience engineering designed for rapid fail-safe recovery.

Applications of CPS Security

Real-world implementations of CPS security across critical sectors:
  1. Protecting Self-Driving Cars from Cyber Threats

    • Challenges: Real-time decision-making requires instantaneous, uncorrupted data inputs from diverse physical sensors under strict latency budgets.
    • Solutions: Deploying in-vehicle Intrusion Detection Systems (IDS), hardware secure boot mechanisms, and cryptographically verified firmware patches.
  2. Securing Healthcare Devices Like Pacemakers

    • Challenges: Wireless telemetry interfaces introduce remote attack vectors; compromised devices risk direct physiological harm.
    • Solutions: Implementing short-range authenticated RF communication channels, rigorous vulnerability scanning, and clinical operator security training.

Emerging Trends in CPS Security

Advanced paradigms shaping the future of cyber-physical defense:
  1. Zero Trust for CPS

    • What It Entails: Adopting a strict “never trust, always verify” architecture across all physical sensors, controllers, and network gateways.
  2. Artificial Intelligence (AI) in CPS Security

    • Role of AI: Processing high-frequency physical sensor data streams to detect complex multi-variable cyber-physical attacks and predict hardware failures.
  3. Blockchain for Secure CPS Communication

    • How It Helps: Providing a decentralized, immutable audit log for recording critical CPS operational transactions and component firmware verification.
  4. Edge Computing for Real-Time CPS Security

    • Why It’s Important: Processing security analytics locally on edge gateways eliminates the network latency and vulnerability risks associated with cloud transmission.

Why Study CPS Security

Mastering cyber-physical security equips engineers to safeguard the vital infrastructure underpinning modern society:
  • Protecting the Integration of Physical and Digital Worlds: Offers critical insight into how the defense of physical infrastructure depends on rigorous cybersecurity and control theory.
  • Understanding Unique CPS Constraints: Teaches engineers to design security mechanisms within strict hardware, timing, and safety boundaries.
  • Real-World Threat Analysis: Studies historic incidents like Stuxnet and GPS spoofing to understand the real-world impact of software flaws on physical machinery.
  • Interdisciplinary Problem Solving: Combines computer science, electrical engineering, control theory, and embedded systems design into a unified defensive discipline.

Interactive Quick Review: CPS Security Controls

Reinforce key concepts regarding smart grid defenses, medical device isolation, and industrial safety interlocks before reading the FAQ:

Quick Review Verification

1. Why must security protocols in Cyber-Physical Systems account for strict real-time latency constraints?
Answer: CPS applications like autonomous braking or smart grid frequency stabilization operate on millisecond control loops. Heavy, un-optimized security encryption or lengthy certificate handshakes can introduce unacceptable processing delay, causing physical control loops to become unstable or fail.
2. How do hardware Secure Boot mechanisms protect embedded CPS controllers against firmware tampering?
Answer: Secure Boot uses a hardware Root of Trust (burned into immutable ROM) to cryptographically verify the digital signature of the bootloader and operating system kernel before execution, blocking unauthorized or malicious firmware from running.

Cyber-Physical Systems Security – Frequently Asked Questions

What is cyber-physical systems (CPS) security?

CPS security protects systems that integrate computation, networking, and physical processes (smart grids, automated factories, autonomous cars, medical devices). It safeguards both digital control software and physical safety processes from malicious disruption.

Why is CPS security important in modern infrastructure?

Critical societal infrastructure relies on connected control loops. Successful attacks cause physical destruction, environmental contamination, or human injury—far surpassing traditional IT data theft.

How does CPS security differ from traditional IT security?

While IT security prioritizes data confidentiality and integrity, CPS security prioritizes physical safety, real-time control availability, and system resilience under strict hardware timing constraints.

What are common attack types against cyber-physical systems?

Threats include remote PLC command injection, sensor data spoofing (GPS/LiDAR), denial-of-service on industrial buses, and malicious firmware tampering designed to force equipment outside safe operational thresholds.

What security measures protect cyber-physical systems?

Layered network segmentation, IT/OT security gateways, hardware secure boot, cryptographic message authentication codes (MAC), anomaly detection systems, and physical hardware fail-safe interlocks.

How do safety and security interact in CPS?

They are inextricably linked: a cybersecurity breach can instantly trigger a physical safety disaster. Modern CPS engineering integrates threat modeling with traditional safety interlocks to ensure fail-safe behavior under attack.

Cyber-Physical Systems (CPS) Security: Conclusion

Cyber-Physical Systems security is vital for the safe and reliable operation of systems that directly impact human lives and critical infrastructure. By implementing advanced security measures and staying ahead of emerging threats, organizations can protect these complex and interconnected systems from evolving cyber risks.
  • Safety-Informed Design: Treat cybersecurity as an extension of physical safety engineering.
  • Hardware Root of Trust: Enforce secure boot and cryptographic firmware verification on all controllers.
  • Real-Time Monitoring: Deploy anomaly detection models across sensor buses and industrial protocols.
  • Resilient Interlocks: Maintain hardware fail-safe mechanisms that operate independently of cyber networks.

End-of-Page Exercises: Review, Reflections & Analytics

Review Questions and Answers

1. What is Cyber-Physical Systems (CPS) Security and why is it critical?
Answer: CPS Security protects integrated computational and physical control networks. It is critical because breaches result in physical destruction, environmental disasters, and threats to human life.
2. How do CPS vulnerabilities differ from those in traditional IT systems?
Answer: CPS vulnerabilities impact physical actuators, machinery, and safety processes, whereas IT systems impact data storage. CPS often run on resource-constrained legacy hardware lacking native encryption.
3. What are the key components of a robust CPS security architecture?
Answer: Secure communication protocols, hardened embedded real-time operating systems, physical access controls, real-time anomaly monitoring, and independent hardware safety interlocks.
4. How does real-time monitoring enhance CPS security?
Answer: Continuous oversight of sensor buses and control loops enables instant detection of unauthorized commands or sensor spoofing, allowing automated containment before physical damage occurs.
5. What challenges are associated with securing embedded systems within CPS?
Answer: Limited CPU and RAM capacity restricting heavy cryptographic suites, real-time execution timing constraints, legacy unpatchable firmware, and physical device accessibility.
6. In what ways does risk management play a role in CPS security?
Answer: Risk management evaluates the likelihood of cyber exploits against their physical safety and operational impact, allowing engineers to prioritize safety-critical protective safeguards.
7. How can secure communication protocols be implemented in CPS environments?
Answer: Using lightweight cryptographic ciphers, Message Authentication Codes (MAC), and secure protocol wrappers (MQTT with TLS, CoAP) designed for low-power microcontrollers.
8. What role does physical security play in the context of CPS?
Answer: Prevents direct physical tampering, unauthorized hardware debugging port access, and rogue sensor attachment at remote substations or factory floors.
9. Why is incident response planning essential for CPS environments?
Answer: Prepares operators to execute emergency physical shutdowns, isolate compromised control networks safely, and prevent cascading industrial accidents.
10. How can organizations balance operational performance with strict CPS security measures?
Answer: By deploying hardware-accelerated cryptographic chips, utilizing edge-computing nodes to offload security analytics, and selecting lightweight protocols adhering to strict millisecond latency budgets.

Thought-Provoking Architectural Questions

1. How might the evolution of autonomous systems reshape CPS security strategies?
Answer: Autonomous systems (self-driving fleets, drones) operate without human operators, requiring decentralized, self-healing security mesh architectures that authenticate peer-to-peer V2X communication autonomously in real time.
2. What impact might quantum computing have on the encryption protocols used in CPS?
Answer: Long-lifecycle CPS assets (power plants, aircraft) operate for decades and risk store-now-decrypt-later attacks. They require immediate migration to Post-Quantum Cryptography (PQC) standards.
3. How can artificial intelligence enhance threat detection in CPS environments?
Answer: AI models analyze multi-variable control loop telemetry (pressure, temperature, valve actuation timing), spotting subtle physical process anomalies that static threshold alarms fail to catch.
4. In what ways could blockchain technology be leveraged to secure CPS data integrity?
Answer: Immutable ledgers can record signed firmware hashes and supply chain component provenance, ensuring controllers only load verified, tamper-proof software updates.
5. How can the integration of physical and cyber defenses improve the resilience of CPS?
Answer: By pairing digital firewalls with independent mechanical circuit breakers and hydraulic safety interlocks that operate entirely outside of computer network control.
6. What challenges arise when implementing real-time threat detection in CPS, and how can they be overcome?
Answer: High packet rates and strict timing constraints. Overcome by delegating anomaly detection processing to dedicated hardware edge accelerators rather than core control processors.
7. How might regulatory changes influence CPS security measures in the coming years?
Answer: Mandatory legal standards (such as NERC CIP or IEC 62443) will hold critical infrastructure operators legally liable for failing to implement baseline embedded device security and supply chain provenance.
8. What are the potential consequences of a coordinated cyber-physical attack on critical infrastructure?
Answer: Widespread multi-city power blackouts, clean water contamination, transportation grid collisions, industrial chemical explosions, and extensive loss of human life.
9. How can cross-industry collaboration enhance the security of CPS across various sectors?
Answer: By sharing sector-agnostic threat intelligence (ISACs), standardizing industrial protocol security wrappers, and collaborating on open-source embedded testing tools.
10. In what ways can emerging technologies be integrated to enhance the overall security posture of CPS?
Answer: Combining edge AI analytics, hardware secure boot roots of trust, zero-trust micro-segmentation, and automated incident response orchestration.
11. How can organizations quantify the risk associated with CPS vulnerabilities to justify security investments?
Answer: Utilizing quantitative risk modeling (FAIR framework) to calculate expected financial loss from physical equipment destruction, regulatory fines, and legal liability.
12. What future trends in CPS security might organizations need to prepare for over the next decade?
Answer: Convergence of IT and OT networks, proliferation of unmanaged IoT smart building sensors, autonomous AI-driven weaponized cyber-physical attacks, and mandatory software bill of materials (SBOM) for embedded firmware.

Numerical Engineering Problems & Solutions

Problem 1: Calculating Daily Packet Volume in a CPS Sensor Network
A CPS network comprises 50 sensor nodes where each node transmits 200 telemetry data packets per minute. Calculate total packets transmitted across the network in 24 hours.
Solution:
  1. Packets per minute (all nodes) = 50 nodes × 200 packets/min = 10,000 packets/min
  2. Packets per hour = 10,000 packets/min × 60 minutes = 600,000 packets/hour
  3. Total packets in 24 hours = 600,000 packets/hour × 24 hours = 14,400,000 packets
Answer: The network transmits 14,400,000 packets in 24 hours.
Problem 2: Estimating Brute-Force Feasibility for Embedded Cryptographic Keys
An embedded control system uses a 64-bit encryption key (total space of 2^64 possible keys). A specialized cryptographic cracking rig tests 10^8 keys per second. Calculate total possible keys and verify that brute-force time exceeds centuries.
Solution:
  1. Total key space = 2^64 ≈ 1.844 × 10^19 possible keys
  2. Brute-force duration in seconds = (1.844 × 10^19) / 10^8 = 1.844 × 10^11 seconds
  3. Convert seconds to years (3.15 × 10^7 seconds/year): (1.844 × 10^11) / (3.15 × 10^7) ≈ 5,854 years
Answer: Brute-forcing a 64-bit key at 10^8 keys/sec requires approximately 5,854 years, confirming strong cryptographic infeasibility for legacy 64-bit ciphers (though modern CPS mandates 128/256-bit keys).
Problem 3: Calculating Expected Monthly Security Breaches and Daily Probability
A CPS experiences an average of 5 intrusion attempts per day with a 1% (0.01) success rate per attempt. Calculate expected breaches per 30-day month and the exact probability of experiencing zero breaches on any given day.
Solution:
  1. Expected daily breaches = 5 attempts × 0.01 success rate = 0.05 breaches/day
  2. Expected monthly breaches (30 days) = 0.05 × 30 = 1.5 breaches per month
  3. Probability of zero breaches on a given day = (1 – 0.01)^5 = (0.99)^5 ≈ 0.9510 (95.10%)
Answer: Expected breaches total 1.5 per month, with a 95.10% daily probability of zero breaches.
Problem 4: Calculating Latency Increase from Security Protocol Wrappers
A real-time CPS control loop operates with an original baseline latency of 100 ms. Implementing a secure message authentication wrapper adds a 15% latency processing overhead. Calculate new operational latency in milliseconds.
Solution:
  1. Latency processing overhead = 100 ms × 0.15 = 15 ms added delay
  2. New total operational latency = 100 ms + 15 ms = 115 ms
Answer: The new secured control loop latency is 115 ms.
Problem 5: Estimating Factory Sensor Failure Rates and Probability
A factory automation CPS contains 100 industrial sensors. Each sensor maintains a 0.5% (0.005) failure rate per month. Calculate expected monthly sensor failures and probability that at least one sensor experiences a failure during the month.
Solution:
  1. Expected failures per month = 100 sensors × 0.005 = 0.5 sensor failures
  2. Probability that zero sensors fail = (1 – 0.005)^100 = (0.995)^100 ≈ 0.6058
  3. Probability that at least one sensor fails = 1 – 0.6058 = 0.3942 (39.42%)
Answer: Expected failures average 0.5 per month, with a 39.42% probability of at least one sensor failing.
Problem 6: Calculating Buffer Overflow Time During a DDoS Attack
During a distributed denial-of-service (DDoS) attack, a CPS control server receives 1,000,000 packets over 2 minutes (120 seconds) while processing normal traffic at 5,000 packets per second. If the server input buffer capacity is 200,000 packets, calculate time elapsed before the buffer overflows.
Solution:
  1. Attack packet arrival rate = 1,000,000 packets / 120 seconds ≈ 8,333.33 packets/sec
  2. Net queue accumulation rate = 8,333.33 arrival – 5,000 processing = 3,333.33 packets/sec net queue growth
  3. Time to overflow buffer = Buffer Capacity / Net Accumulation Rate = 200,000 / 3,333.33 ≈ 60.0 seconds
Answer: The input buffer overflows in exactly 60.0 seconds.
Problem 7: Calculating Vulnerability Reduction via Security Patching
A firmware security audit uncovers an initial count of 150 vulnerabilities in an industrial controller. Applying an emergency security patch fixes 80% of identified flaws. Calculate remaining vulnerabilities and absolute reduction count.
Solution:
  1. Vulnerabilities patched = 150 × 0.80 = 120 flaws resolved
  2. Remaining vulnerabilities = 150 – 120 = 30 flaws
Answer: Patching eliminates 120 flaws, leaving 30 remaining vulnerabilities.
Problem 8: Quantifying Expected Annual Financial Loss from CPS Breaches
The average financial impact of a catastrophic CPS security breach is $2,000,000. Quantitative risk modeling estimates the annual probability of occurrence at 3% (0.03). Calculate expected annual financial loss.
Solution:
  1. Expected annual loss = Impact × Annual Probability = $2,000,000 × 0.03 = $60,000/year
Answer: The expected annual financial risk loss is $60,000.
Problem 9: Calculating Monitoring Alert Volume over 24 Hours
A CPS logging gateway records 500 events per hour. Historical baselines indicate that 0.4% (0.004) of these events signify potential intrusion or breach attempts. Calculate expected breach-indicating events over a 24-hour period.
Solution:
  1. Breach events per hour = 500 events × 0.004 = 2 breach events/hour
  2. Total breach events in 24 hours = 2 events/hour × 24 hours = 48 events
Answer: The monitoring system is expected to log 48 breach-indicating events over 24 hours.
Problem 10: Calculating Transmission Time Impact from Secure Protocol Wrappers
A sensor transmits unencrypted telemetry in 50 ms. Adopting a secure industrial protocol wrapper increases transmission time by 10%. Calculate new transmission time in milliseconds.
Solution:
  1. Transmission time increase = 50 ms × 0.10 = 5 ms added delay
  2. New transmission time = 50 ms + 5 ms = 55 ms
Answer: The new secured transmission time is 55 ms.
Problem 11: Calculating Command Error Rate Reduction in Industrial Controllers
An industrial CPS controller processes 10,000 operational commands per day. A firmware security update reduces command error rate from 2% (0.02) to 0.5% (0.005). Calculate errors per day before/after update and total daily error reduction.
Solution:
  1. Original daily errors = 10,000 commands × 0.02 = 200 errors/day
  2. Updated daily errors = 10,000 commands × 0.005 = 50 errors/day
  3. Daily error reduction = 200 – 50 = 150 errors saved per day
Answer: The update eliminates 150 errors daily, reducing daily errors from 200 down to 50 errors/day.
Problem 12: Calculating Downtime Reduction from Incident Response Planning
An un-prepared CPS incident response averages 120 minutes of downtime per security disruption. Implementing an automated incident response plan cuts downtime by 40%. Calculate new downtime per incident and total time saved across 10 security incidents.
Solution:
  1. New downtime per incident = 120 minutes × (1 – 0.40) = 72 minutes/incident
  2. Time saved per incident = 120 – 72 = 48 minutes saved/incident
  3. Total time saved across 10 incidents = 48 minutes × 10 = 480 minutes (8 hours) saved
Answer: Incident response planning cuts downtime to 72 minutes per incident, saving a total of 480 minutes (8 hours) across 10 incidents.

Cyber-Physical Systems (CPS) Security — Summary & Wrap-Up

Cyber-Physical Systems security is vital for smart grids, autonomous vehicles, medical devices, and automated industrial manufacturing. By combining safety-informed design, hardware roots of trust, real-time protocol monitoring, and independent physical interlocks, organizations can protect connected infrastructure from catastrophic cyber-physical disruption.
Last updated: 22 Jul 2026