
Incident Response and Forensics Education is the discipline of staying clear-headed when the story is incomplete. The diagram shows how that clarity is built. Learners arrive with inputs—foundational knowledge and realistic scenarios—but their work is shaped by controls that protect both truth and fairness: response procedures, evidence rules, and legal/ethical boundaries that prevent “guessing” from becoming an official conclusion. With mechanisms like guided labs and investigation tools, students practice the real sequence: detect and triage, contain without destroying evidence, collect data carefully, reconstruct timelines, and separate what is known from what is merely suspected. The output is a learner who can respond with method rather than impulse—able to preserve evidence properly, explain findings without exaggeration, and help restore systems while keeping the investigation defensible if it must later be reviewed by auditors, management, or authorities.
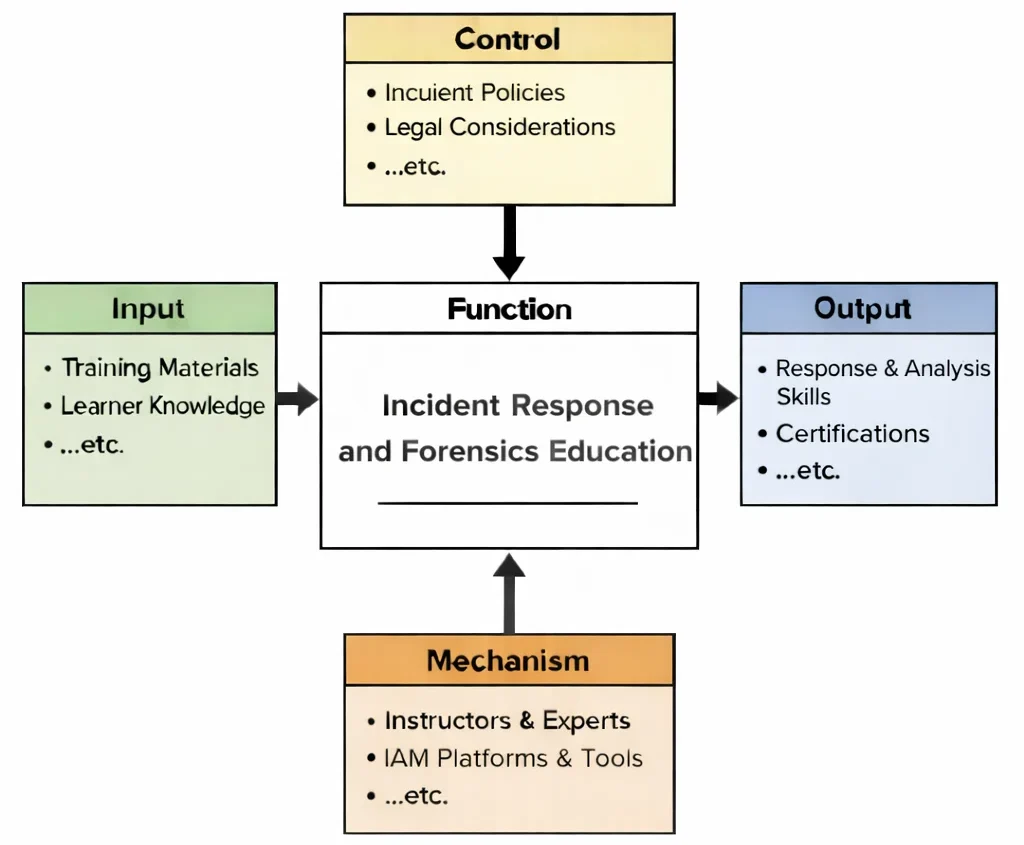
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Incident Response and Forensics Education as a structured transformation. Inputs include training materials, case scenarios, and baseline learner knowledge in systems and security. Controls include incident handling procedures, legal/ethical boundaries, evidence requirements, chain-of-custody rules, and organizational policies that govern what may be collected, how it must be preserved, and how conclusions should be justified. Mechanisms include instructors, experts, lab environments, forensic tools, logging/monitoring platforms, and investigation workflows that enable hands-on practice. Outputs include learners who can triage incidents, preserve and analyze evidence, document findings clearly, support recovery decisions, and communicate results in a defensible manner.
Interactive Check: Intro & System Concepts
Verify your understanding of how evidence preservation, chain of custody, and structured incident response procedures safeguard investigations:
Introductory Concept Verification
1. Why must incident responders and forensic investigators strictly adhere to chain-of-custody rules?
Answer: Chain-of-custody documentation proves that digital evidence was collected, handled, stored, and analyzed without tampering or alteration. Without strict evidence rules, technical findings can be challenged or rendered inadmissible during legal proceedings, regulatory audits, or management reviews.
2. What constitutes the primary operational output expected from Incident Response Education?
Answer: Methodological resilience: learners who can triage breaches calmly, contain threats without destroying volatile evidence, reconstruct precise attack timelines, and explain findings objectively without exaggeration.
Incident Response and Forensics plays a pivotal role in the broader domain of cybersecurity, focusing on the detection, investigation, and resolution of security breaches. As modern digital ecosystems grow more complex, effective response mechanisms are essential to contain threats and limit damage. By integrating practices from cybersecurity policy and operational frameworks, incident response provides structured protocols to react swiftly to malware outbreaks, insider threats, and targeted attacks.
The process begins with proactive preparation, often involving simulations and exercises led by ethical hacking teams to assess vulnerabilities across systems, including application security layers and cloud infrastructures. These drills align with insights gained from cybersecurity awareness programs and organizational policies, ensuring everyone knows how to respond when a breach occurs. Key stakeholders must also understand the role of identity and access management in controlling the scope of compromise.
The containment and eradication phase often leverages tools driven by AI and ML in cybersecurity to automate threat detection, identify suspicious behavior, and isolate affected systems. This is especially important for defending endpoints and network segments before damage spreads. Response teams also rely on up-to-date threat intelligence to attribute incidents and prevent future occurrences by understanding adversary techniques.
Once containment is complete, forensic analysis begins. Drawing on principles from cryptography, investigators recover and preserve digital evidence such as log files, access credentials, and data remnants. Insights derived from data analysis and visualization techniques help uncover attack vectors, timelines, and affected assets. These efforts support legal proceedings and regulatory compliance, especially in industries governed by strict data privacy and security requirements.
Modern incident response is deeply intertwined with data science and analytics, where tools facilitate real-time alerting, behavior baselining, and anomaly detection. Utilizing data cleaning and preprocessing improves signal quality, while advanced technologies allow rapid indexing and search across vast datasets. The ability to respond effectively depends on the integration of scalable analytics workflows and domain-specific security knowledge.
In sectors involving cyber-physical systems (CPS) and operational technology (OT), incident response must address safety implications alongside data integrity. Forensic teams examine not only digital artifacts but also the physical context, particularly in critical infrastructure like energy grids and healthcare systems. This growing need has led to increased focus on emerging areas in cybersecurity that blend real-world and virtual investigations.
The maturity of an organization’s response capability is a key metric of cybersecurity readiness. It is enhanced through ongoing training, integration of domain-specific analytics, and alignment with ethical and social considerations. As incidents become more frequent and complex, the ability to learn from each event and adapt policies ensures long-term resilience and trust in digital systems.
To support continuous improvement, teams should maintain access to historical event data stored through data collection and storage systems and informed by big data analytics. This data not only facilitates response but also serves as the foundation for threat modeling and strategic planning. In the end, incident response and forensics represent more than technical capabilities—they are key components of digital accountability and organizational resilience.
This image visualizes an incident response “war room” where a team monitors threats in real time. A luminous globe at the center suggests that incidents can spread across connected systems and regions, while surrounding screens show alert charts and threat indicators. Warning triangles, padlock symbols, and red malware-like icons communicate urgency and active risk. Workstations, servers, and stacked data blocks represent critical infrastructure and logs being analyzed. The words and visual cues for containment and recovery emphasize the incident response lifecycle: rapidly limiting damage, gathering evidence, restoring services, and learning from the event to prevent recurrence. Overall, it portrays incident response as a structured, team-based process that blends technology, procedures, and decision-making under pressure.
Building Cyber Resilience: Incident Response Navigation
Discover how Incident Response and Digital Forensics coordinate breach containment, evidence preservation, and root-cause analysis across the Cybersecurity cluster. Each card details SIEM log correlation, short-term containment, volatile memory acquisition, and post-incident reviews.
Cybersecurity Overview
Presents the overall system architecture, mapping how incident response workflows operationalize defensive monitoring and security policies during live breaches.
Network Security
Examines network traffic anomaly isolation, blocking malicious IP egress channels, and analyzing NetFlow capture logs during network intrusions.
Application Security
Focuses on analyzing web server access logs, investigating API exploitation attempts, and deploying hotfix code patches during active application compromises.
Cloud Security
Details cloud control-plane forensics (AWS CloudTrail / Azure Activity logs), revoking compromised IAM access keys, and snapshotting affected cloud storage volumes.
Endpoint Security
Covers automated EDR host network isolation, volatile RAM memory dump extraction, and forensic timeline reconstruction on compromised laptops.
Identity & Access Management
Governs emergency token revocation, forcing enterprise password resets, auditing Active Directory session persistence, and investigating credential stuffing.
Cryptography
Applies cryptographic hash verification (SHA-256) to ensure forensic disk image integrity and investigates compromised TLS private key rotation.
Incident Response & Forensics
Focuses on NIST incident response lifecycle (Preparation, Detection, Containment, Eradication, Recovery, Lessons Learned), chain of custody, and disk/memory forensics.
Threat Intelligence
Correlates forensic artifacts with adversary TTPs and threat actor feeds to perform accurate attribution and anticipate subsequent attack waves.
Ethical Hacking & Pen Testing
Utilizes insights from red-teaming and purple-team exercises to test incident detection rule coverage and validate SOC alert triage speed.
Cybersecurity Awareness
Trains employees to immediately report suspicious phishing emails or anomalous system behavior to the security operations center (SOC).
Policy & Governance
Enforces formal Incident Response Plans (IRP), regulatory breach notification timelines, and post-incident lessons-learned governance.
CPS Security
Orchestrates physical emergency shutdown procedures and PLC controller memory forensics for smart grids and autonomous transport.
OT Security
Safeguards industrial SCADA incident response, ensuring emergency containment preserves physical plant safety without causing catastrophic equipment damage.
AI & ML in Security
Leverages AI-powered SOAR platforms for automated log correlation, anomaly scoring, and instant playbook-driven threat containment.
Emerging Areas
Investigates cloud enclave forensics, analyzing AI deepfake attack artifacts, and responding to smart contract exploits.
Key Topics in Incident Response and Forensics
Structured methodologies for investigating security breaches and restoring operational integrity:
Incident Detection and Containment Strategies
- Detection: Monitoring SIEM platforms (Splunk, QRadar), IDS telemetry (Snort, Suricata), and server logs for abnormal behaviors in real time.
- Containment: Executing short-term isolation (disconnecting compromised VLANs, blocking malicious IPs) and long-term eradication (patching vulnerabilities, resetting credentials).
Digital Forensics for Analyzing Cyberattacks
- Evidence Preservation: Collecting disk images, memory dumps, and network packets while strictly maintaining a verifiable chain of custody using forensic tools (Autopsy, FTK).
- Timeline Reconstruction: Tracing attacker lateral movement, persistence mechanisms, and exfiltration pathways.
Root Cause Analysis and Mitigation
- Determining initial access vectors (phishing, unpatched CVEs) and deploying architectural hardening to prevent recurrence.
Applications of Incident Response and Forensics
Operational execution across enterprise and legal domains:
Building Incident Response Plans (IRPs)
- Establishing formal playbooks covering the NIST lifecycle: Preparation, Detection & Analysis, Containment, Eradication, Recovery, and Post-Incident Review.
Conducting Forensic Investigations for Legal Proceedings
- Uncovering attacker attribution and compiling forensically sound evidence packages to support legal action and regulatory compliance reporting.
Emerging Trends in Incident Response & Forensics
Next-generation incident handling technologies:
- AI-Powered SOAR: Automating alert triage, anomaly clustering, and initial threat containment playbooks.
- Cloud Incident Response: Adapting forensic acquisition tools to multi-tenant cloud architectures (AWS GuardDuty, Azure Security Center).
- IoT/OT Forensics: Developing specialized firmware and volatile memory extraction techniques for resource-constrained embedded hardware.
Why Study Incident Response and Forensics
Mastering incident investigation equips security professionals to manage high-pressure crises effectively:
- Minimizing Breach Damage: Teaches rapid containment strategies to halt active malware and ransomware propagation.
- Mastering Digital Evidence Collection: Provides hands-on experience with forensic suites (Autopsy, FTK, Wireshark) while maintaining legal chain of custody.
- Organizational Resilience: Transforms security incidents into actionable lessons that drive long-term architectural improvements.
Interactive Quick Review: Incident Response & Forensics
Reinforce key concepts regarding the NIST incident response lifecycle, evidence preservation, and chain of custody before reading the FAQ:
Quick Review Verification
1. What is the operational distinction between Short-Term Containment and Long-Term Eradication in incident response?
Answer: Short-term containment focuses on immediate emergency actions to halt active threats (e.g., isolating a compromised host or blocking malicious IP addresses). Long-term eradication removes the root cause of the breach (e.g., deleting malware, patching underlying software vulnerabilities, and resetting compromised credentials).
2. Why are write-blockers and cryptographic hashing (SHA-256) essential during forensic disk acquisition?
Answer: Write-blockers physically or logically prevent any data from being written to the evidence drive during connection, preserving bit-for-bit integrity. Cryptographic hashing creates a unique digital fingerprint of the drive before and after acquisition to mathematically prove no alterations occurred.
Incident Response and Digital Forensics – Frequently Asked Questions
What is incident response in cybersecurity?
Incident response is the structured process an organization follows when detecting, analyzing, containing, eradicating, and recovering from security breaches or malware outbreaks.
What are the typical phases of the incident response lifecycle?
1. Preparation; 2. Detection & Analysis; 3. Containment; 4. Eradication; 5. Recovery; 6. Post-Incident Review (Lessons Learned).
What is digital forensics and how does it relate to incident response?
Digital forensics is the disciplined preservation, collection, and analysis of digital evidence. It supports incident response by uncovering how an attacker gained access, what files were touched, and what traces were left behind.
Why is evidence preservation and chain of custody important?
Proper evidence preservation (using write-blockers and bit-stream imaging) and chain-of-custody documentation ensure digital evidence remains untampered and legally admissible in court or regulatory audits.
What data sources are commonly analyzed during a forensic investigation?
System and security event logs, network traffic packet captures (PCAP), endpoint telemetry, volatile RAM memory dumps, disk images, and application access records.
How do playbooks and runbooks improve incident handling?
Playbooks provide step-by-step instructions for specific incident types (ransomware, phishing), reducing confusion, accelerating triage, and ensuring consistent procedural execution under pressure.
Incident Response and Forensics: Conclusion
Incident response and forensics are essential for modern cybersecurity strategies, enabling organizations to manage threats effectively and learn from past incidents to prevent future occurrences.
- Structured Lifecycles: Follow the NIST incident handling stages from preparation to post-incident review.
- Forensic Rigor: Maintain strict chain of custody and bit-stream evidence preservation for legal defensibility.
- Continuous Learning: Turn every security incident into an actionable improvement for future organizational resilience.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is incident response in the context of cybersecurity?
Answer: Incident response is the structured process of identifying, managing, and recovering from cybersecurity incidents to minimize damage and restore normal operations.
2. Why is digital forensics important in handling cyber incidents?
Answer: It collects, preserves, and analyzes digital evidence to determine the exact cause and scope of a breach, supporting legal proceedings and preventing recurrence.
3. What are the key phases of an effective incident response plan?
Answer: Preparation, Identification (Detection & Analysis), Containment, Eradication, Recovery, and Post-Incident Analysis (Lessons Learned).
4. How do organizations prepare for potential cyber incidents through incident response planning?
Answer: By establishing IRP playbooks, conducting tabletop simulation drills, training staff, and deploying centralized logging and SIEM monitoring tools.
5. What role does communication play in incident response and forensics?
Answer: Ensures technical teams, executive management, legal advisors, and external regulators remain coordinated and informed throughout an active crisis.
6. How does evidence collection and preservation contribute to effective digital forensics?
Answer: Maintains forensic integrity and admissibility in court by securing data without alteration and documenting an unbroken chain of custody.
7. What challenges are commonly encountered during incident response, and how can they be addressed?
Answer: Limited network visibility, detection delays, and evidence contamination. Address via robust SIEM logging, automated containment playbooks, and forensic training.
8. How can automation improve the incident response process?
Answer: SOAR automation accelerates threat detection, enriches alerts with threat intelligence, and executes instant containment actions in milliseconds.
9. How do incident response and digital forensics contribute to organizational resilience?
Answer: By minimizing downtime, limiting financial and reputational losses, and turning post-incident reviews into permanent architectural defenses.
10. What future trends are expected to shape incident response and forensics?
Answer: AI-driven autonomous threat hunting, cloud-native XDR telemetry ingestion, blockchain evidence logging, and specialized IoT/OT forensic tooling.
Thought-Provoking Architectural Questions
1. How might the integration of artificial intelligence transform incident response in the near future?
Answer: AI will autonomously correlate multi-cloud telemetry, reconstruct attack timelines in seconds, and execute self-healing containment actions without human delay.
2. In what ways could emerging technologies challenge traditional digital forensic methods?
Answer: Encrypted multi-tenant cloud storage, ephemeral serverless functions, and decentralized IoT devices create volatile, distributed data stores that resist traditional static disk imaging.
3. How can organizations balance rapid incident response with meticulous forensic requirements?
Answer: By deploying automated volatile memory snapshot scripts and cloud instance isolation scripts that capture forensic evidence the moment an alert triggers, prior to active remediation.
4. What ethical considerations arise in digital forensics regarding privacy?
Answer: Forensic imaging of endpoints can inadvertently capture private employee communications or personal files unrelated to the security breach, requiring strict data minimization protocols.
5. How might increasing regulatory pressures influence incident response and forensic practices?
Answer: Strict breach reporting windows (e.g., 24–72 hours under SEC or GDPR rules) force organizations to maintain pre-configured forensic logging and rapid triage capabilities.
6. What are the potential benefits and drawbacks of automating incident response?
Answer: Benefits include lightning-fast MTTR and 24/7 coverage; drawbacks include the risk of false-positive automation accidentally isolating critical production business services.
7. How can continuous monitoring enhance incident response and forensic investigations?
Answer: Provides high-fidelity historical telemetry, eliminating blind spots and allowing forensic investigators to see exact attacker pre-compromise reconnaissance steps.
8. In what ways can incident response teams leverage threat intelligence?
Answer: By matching observed IOCs and adversary behaviors against global threat feeds, enabling rapid attribution and proactive hunting for secondary persistence mechanisms.
9. What challenges arise when performing digital forensics in cloud environments?
Answer: Lack of physical hardware access, reliance on cloud provider telemetry sharing, multi-tenant boundaries, and legal jurisdiction complexities across global cloud regions.
10. How can organizations measure the effectiveness of incident response capabilities?
Answer: Tracking Mean Time to Detect (MTTD), Mean Time to Respond (MTTR), tabletop drill scoring, and measuring post-incident control remediation velocity.
11. What strategies ensure forensic evidence is admissible in legal proceedings?
Answer: Enforcing strict chain-of-custody logging, utilizing write-blockers during acquisition, computing cryptographic file hashes (SHA-256), and using court-validated forensic software.
12. How might future developments alter cybersecurity defense landscapes?
Answer: Shift toward predictive incident response where AI neutralizes attacks during the reconnaissance phase before intrusion or data exfiltration occurs.
Numerical Engineering Problems & Solutions
Problem 1: Mitigated Impact Volume from Incident Response Plans
An organization records 250 security incidents per year. An incident response plan reduces overall impact severity by 40%. Calculate the equivalent number of incidents mitigated and overall impact reduction volume.
An organization records 250 security incidents per year. An incident response plan reduces overall impact severity by 40%. Calculate the equivalent number of incidents mitigated and overall impact reduction volume.
Solution:
- Total baseline incidents per year = 250
- Impact reduction percentage = 40% (0.40)
- Equivalent incidents mitigated = 250 × 0.40 = 100 incidents’ worth of impact
Problem 2: Forensic Investigation Time Savings via Automation
A forensic investigation requires an average of 12 hours per incident. Automation tools reduce investigation time by 35%. Calculate new average time per incident and total time saved across 20 incidents.
A forensic investigation requires an average of 12 hours per incident. Automation tools reduce investigation time by 35%. Calculate new average time per incident and total time saved across 20 incidents.
Solution:
- Original time per incident = 12 hours
- Time reduction per incident = 12 × 0.35 = 4.2 hours saved/incident
- New time per incident = 12 – 4.2 = 7.8 hours
- Total time saved across 20 incidents = 20 × 4.2 = 84.0 hours saved
Problem 3: Forensic Image Processing Daily Metrics
An incident response team acquires 15 forensic images daily, with each image taking 2.5 hours to process. Process improvements cut image processing time by 50%. Calculate new processing time per image and total daily processing time saved in hours.
An incident response team acquires 15 forensic images daily, with each image taking 2.5 hours to process. Process improvements cut image processing time by 50%. Calculate new processing time per image and total daily processing time saved in hours.
Solution:
- Original processing time per image = 2.5 hours
- Time reduction per image = 2.5 × 0.50 = 1.25 hours saved/image
- New processing time per image = 2.5 – 1.25 = 1.25 hours
- Total daily time saved = 15 images × 1.25 hours = 18.75 hours/day
Problem 4: Monthly Incident Response Time Acceleration
An incident response team responds to 8 incidents per month with an average response time of 45 minutes per incident. An improved protocol reduces response time by 20%. Calculate new response time per incident and total monthly time saved in minutes.
An incident response team responds to 8 incidents per month with an average response time of 45 minutes per incident. An improved protocol reduces response time by 20%. Calculate new response time per incident and total monthly time saved in minutes.
Solution:
- Original response time = 45 minutes
- Time reduction per incident = 45 × 0.20 = 9 minutes saved/incident
- New response time = 45 – 9 = 36 minutes/incident
- Total monthly time saved = 8 incidents × 9 minutes = 72 minutes/month
Problem 5: Digital Forensics Weekly Data Processing Capacity
A digital forensic lab processes 300 GB of evidence data per week. A new system increases processing speed by 60%. Calculate new weekly processing capacity and additional GB processed per week.
A digital forensic lab processes 300 GB of evidence data per week. A new system increases processing speed by 60%. Calculate new weekly processing capacity and additional GB processed per week.
Solution:
- Original weekly capacity = 300 GB/week
- Capacity increase = 300 × 0.60 = 180 GB added/week
- New weekly processing capacity = 300 + 180 = 480 GB/week
Problem 6: Annual Downtime Hours Saved from Incident Response
An organization’s incident response plan reduces average outage downtime from 120 minutes to 50 minutes per incident. For 10 incidents per year, calculate total annual downtime saved in hours.
An organization’s incident response plan reduces average outage downtime from 120 minutes to 50 minutes per incident. For 10 incidents per year, calculate total annual downtime saved in hours.
Solution:
- Time saved per incident = 120 min – 50 min = 70 minutes saved
- Total annual minutes saved = 10 incidents × 70 minutes = 700 minutes/year
- Convert minutes to hours = 700 / 60 ≈ 11.67 hours saved annually
Problem 7: Network Traffic Forensics Volume Reduction
Forensic analysis reveals that 8% (0.08) of network traffic (5,000 GB monthly total) is suspicious. Network security improvements reduce suspicious traffic volume by 75%. Calculate initial suspicious traffic volume, reduction in GB, and remaining suspicious traffic.
Forensic analysis reveals that 8% (0.08) of network traffic (5,000 GB monthly total) is suspicious. Network security improvements reduce suspicious traffic volume by 75%. Calculate initial suspicious traffic volume, reduction in GB, and remaining suspicious traffic.
Solution:
- Initial monthly suspicious traffic = 5,000 GB × 0.08 = 400 GB/month
- Reduction in suspicious traffic = 400 GB × 0.75 = 300 GB eliminated
- Remaining suspicious traffic = 400 – 300 = 100 GB/month
Problem 8: Forensic Investigation Cost Reduction Savings
A forensic team processes 50 incident cases per year at an average cost of $2,000 per case. Process improvements reduce investigation cost by 30%. Calculate initial annual cost, savings per case, total annual cost savings, and new annual cost.
A forensic team processes 50 incident cases per year at an average cost of $2,000 per case. Process improvements reduce investigation cost by 30%. Calculate initial annual cost, savings per case, total annual cost savings, and new annual cost.
Solution:
- Original annual investigation cost = 50 cases × $2,000 = $100,000/year
- Savings per case = $2,000 × 0.30 = $600 saved/case
- Total annual cost savings = 50 cases × $600 = $30,000/year
- New annual cost = $100,000 – $30,000 = $70,000/year
Problem 9: Incident Response Drill Time Reduction
An incident response drill takes 3 hours on average. A company conducts 4 drills per quarter. Calculate total annual drill time (16 drills). If improvements cut drill time by 25%, calculate new total drill time and annual hours saved.
An incident response drill takes 3 hours on average. A company conducts 4 drills per quarter. Calculate total annual drill time (16 drills). If improvements cut drill time by 25%, calculate new total drill time and annual hours saved.
Solution:
- Total drills per year = 4 quarters × 4 drills/quarter = 16 drills/year
- Original total annual drill time = 16 drills × 3 hours = 48 hours/year
- Annual hours saved (25% reduction) = 48 hours × 0.25 = 12 hours saved/year
- New total annual drill time = 48 – 12 = 36 hours/year
Problem 10: Weekly and Annual Investigation Cost Savings
An organization detects 2 incidents per week, with an average investigation cost of $5,000 per incident. Improved forensics reduce investigation costs by 40%. Calculate weekly baseline cost, weekly savings, and total annual savings (52 weeks).
An organization detects 2 incidents per week, with an average investigation cost of $5,000 per incident. Improved forensics reduce investigation costs by 40%. Calculate weekly baseline cost, weekly savings, and total annual savings (52 weeks).
Solution:
- Weekly baseline cost = 2 incidents × $5,000 = $10,000/week
- Savings per incident = $5,000 × 0.40 = $2,000 saved/incident
- Weekly cost savings = 2 incidents × $2,000 = $4,000/week
- Total annual savings (52 weeks) = $4,000 × 52 = $208,000/year
Problem 11: Critical Event Volume Reduction
An organization logs 250,000 events per year related to incident response. Telemetry analysis flags 0.5% (0.005) as critical events. A new AI filtering system reduces the critical flag rate by 80%. Calculate initial critical events per year, new critical events per year, and absolute reduction in critical events.
An organization logs 250,000 events per year related to incident response. Telemetry analysis flags 0.5% (0.005) as critical events. A new AI filtering system reduces the critical flag rate by 80%. Calculate initial critical events per year, new critical events per year, and absolute reduction in critical events.
Solution:
- Initial critical events per year = 250,000 × 0.005 = 1,250 critical events/year
- Critical events eliminated (80% drop) = 1,250 × 0.80 = 1,000 events prevented
- New annual critical events = 1,250 – 1,000 = 250 critical events/year
Problem 12: Forensic Reporting Speed Acceleration
An incident response team improves its forensic reporting speed from 10 days down to 4 days per case. Handling 30 cases annually, calculate total days saved and convert this into equivalent weeks saved (7 days/week).
An incident response team improves its forensic reporting speed from 10 days down to 4 days per case. Handling 30 cases annually, calculate total days saved and convert this into equivalent weeks saved (7 days/week).
Solution:
- Time saved per case = 10 days – 4 days = 6 days saved/case
- Total days saved annually = 30 cases × 6 days = 180 days saved/year
- Convert days to weeks = 180 days / 7 days/week ≈ 25.71 weeks saved per year
Incident Response and Forensics — Summary & Wrap-Up
Incident response and digital forensics provide the disciplined framework necessary to investigate security breaches, preserve evidence under strict legal chain-of-custody rules, contain active threats, and restore systems securely. By combining NIST incident handling lifecycles, volatile memory acquisition, SIEM log correlation, and post-incident reviews, security teams ensure digital accountability and long-term organizational resilience.