Prepare for University Studies & Career Advancement
Emerging Areas in Cyber Security
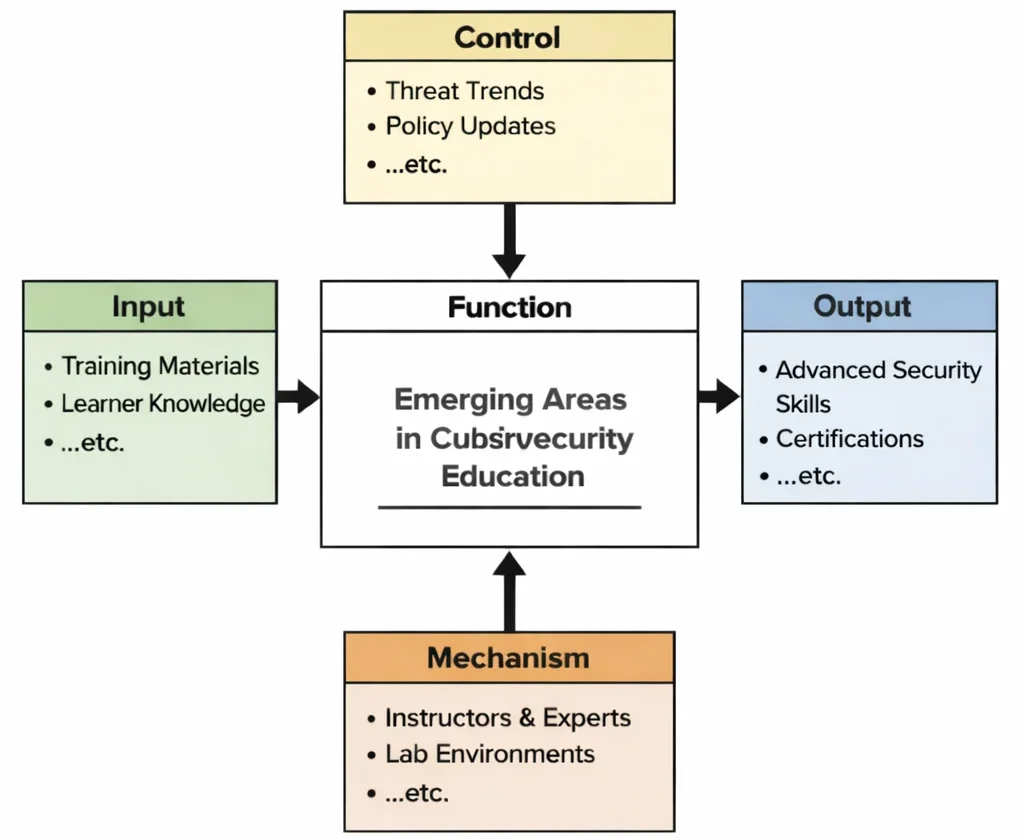
Emerging Areas in Cybersecurity is the study of a moving frontier—where yesterday’s “edge case” becomes tomorrow’s main threat. The diagram tells a simple truth: this subject is governed by change. Learners bring in the usual inputs—core concepts, examples, and practice tasks—but what shapes the learning most is the control layer: threat trends, policy updates, and the steady rewriting of what counts as safe, acceptable, and compliant. With mechanisms like experts and lab environments, students learn in a way that resembles the real world: testing assumptions, reading signals, updating defenses, and practicing response patterns as new attack surfaces appear. The output is not just advanced technique, but adaptive judgment—an ability to recognize what is genuinely new, to separate hype from risk, and to carry security thinking into unfamiliar technologies without waiting for a textbook to catch up.
Emerging Areas in Cybersecurity, mapped with IDEF0: evolving inputs and controls drive learning into advanced, future-ready security skills.
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Emerging Areas in Cybersecurity Education as a structured transformation process. Inputs include training materials and learner knowledge. Controls include threat trends, policy updates, and shifting standards that continually reshape what must be defended. Mechanisms such as instructors, experts, and lab environments enable hands-on practice with new tools and scenarios. Outputs include learners who build advanced security skills, understand emerging risks, and can evaluate novel attack surfaces—preparing them to adapt as technologies, adversaries, and regulations evolve.
Interactive Check: Intro & System Concepts
Verify your understanding of how shifting threat landscapes and technological innovation redefine defensive priorities:
Introductory Concept Verification
1. Why is adaptive judgment more crucial than memorizing specific attack tools in emerging cybersecurity domains?
Answer: Emerging technologies (such as generative AI, quantum computing, and serverless edge nodes) create novel attack surfaces faster than textbooks or static signatures can document. Adaptive judgment enables security engineers to evaluate risk fundamentals and design resilient defenses for un-documented attack vectors without relying on outdated playbooks.
2. What constitutes the primary “Control” layer in the IDEF0 model for Emerging Cybersecurity Areas?
Answer: Evolving threat trends, regulatory policy updates, and shifting compliance standards. These external forces continually rewrite what constitutes an acceptable security posture as new technologies emerge.
As the threat landscape evolves, emerging areas in cyber security are rapidly reshaping how organizations defend their digital assets. These developments go far beyond traditional network security and application security practices. They integrate cutting-edge disciplines like AI and machine learning, which detect anomalies and respond to threats with unprecedented speed and precision. The interplay of innovation and threat complexity also drives new use cases for data science and analytics, as cyber defense becomes increasingly data-driven.
Emerging fields such as cyber-physical systems (CPS) security and operational technology (OT) security underscore the importance of securing critical infrastructure, where attacks can have both digital and physical consequences. The convergence of information technology and operational systems also demands alignment with broader cybersecurity policies that support resilience and compliance. Similarly, emerging cloud architectures—like serverless computing and containerization—introduce new risks that require fresh approaches to policy and design.
Rapid adoption of edge computing further complicates cybersecurity. With data processing distributed across devices and locations, threats multiply and centralized control becomes impractical. This shift demands rethinking network connectivity and visibility strategies. To meet these challenges, professionals explore tools like threat intelligence platforms and proactive techniques such as ethical hacking to uncover blind spots.
Emerging areas also expand the notion of cybersecurity awareness. As attack vectors grow more sophisticated, educating users on phishing, social engineering, and privacy issues becomes as vital as deploying technical defenses. New frontiers in cryptography—including quantum-resistant algorithms—aim to future-proof secure communications. Likewise, improved practices in identity and access management enable organizations to enforce least-privilege principles at scale.
At the same time, advances in DevOps and Infrastructure as Code are transforming how security is implemented. Automation and continuous integration not only enhance speed, but also open new security challenges that must be addressed in development pipelines. To respond effectively to incidents in these agile environments, teams are bolstering capabilities in digital forensics and performance tuning to restore systems efficiently after attacks.
In sectors like finance, healthcare, and energy, emerging cybersecurity areas are increasingly governed by compliance frameworks and risk models that prioritize resilience. Leveraging big data analytics helps these industries forecast potential breach impacts and prioritize mitigation strategies. Meanwhile, robust cloud security controls are essential as workloads shift across hybrid and multi-cloud environments.
Overall, emerging areas in cybersecurity are about more than just technology—they reflect evolving philosophies of trust, transparency, and shared responsibility. They demand continuous adaptation and strategic alignment between technical controls, human behavior, and systemic resilience. Whether addressing endpoint protection, redefining policy for new attack surfaces, or exploring AI-powered defense, cybersecurity professionals must remain agile in an era of relentless innovation.
Emerging areas in cybersecurity: new architectures and intelligent defenses for a rapidly evolving threat landscape.
This image presents “emerging areas” in cybersecurity as a forward-looking, experimental frontier. A luminous central platform suggests a next-generation security core—where identity, access, and verification are continuously managed rather than assumed. Surrounding holographic padlocks, network nodes, and dashboard-like charts evoke modern approaches such as zero trust architecture, automated monitoring, and data-driven defense. The sci-fi colors and abstract terrain hint at how quickly the field is expanding into new domains: cloud-native security, AI-assisted detection, securing connected devices, and adapting to novel attack methods. Overall, the illustration communicates innovation, constant change, and the need for flexible security ideas that can keep pace with new technologies and new risks.
Building Cyber Resilience: Emerging Areas Navigation
Discover how frontier research domains, post-quantum cryptography, and zero trust paradigms evolve digital trust across the Cybersecurity cluster. Each card details quantum-safe algorithms, zero-trust micro-segmentation, smart contract auditing, and privacy-enhancing technologies.
Presents the overarching macro-architecture, mapping how emerging security domains integrate with baseline network, application, and identity controls.
Leverages generative AI for automated security orchestration while defending internal machine learning pipelines from data poisoning attacks.
Emerging Areas
Focuses on Post-Quantum Cryptography, Zero Trust Architecture, Blockchain & Smart Contract Security, Privacy-Enhancing Technologies, and AI Safety.
Key Topics in Emerging Cybersecurity Areas
Frontier disciplines redefining the boundaries of digital defense:
Post-Quantum Cryptography (PQC)
Quantum Vulnerabilities: Shor’s algorithm running on large-scale quantum computers will break RSA and ECC asymmetric key exchange algorithms.
Quantum-Resistant Algorithms: Developing lattice-based, code-based, and hash-based signature schemes (NIST PQC standards) to secure communications against future quantum decryption.
Hybrid Deployments: Pairing classical algorithms with post-quantum primitives during multi-year enterprise transition phases.
Zero Trust Architecture (ZTA)
Core Principles: Operating under “never trust, always verify” across identity, device health, and network traffic regardless of physical location.
Implementation: Micro-segmentation, continuous adaptive risk scoring, and Secure Access Service Edge (SASE) integration.
Blockchain & Decentralized Security
Consensus & Smart Contracts: Securing Proof of Stake (PoS) consensus mechanisms and executing formal verification on smart contracts to prevent reentrancy exploits.
Decentralized Identity (DID): Empowering users with verifiable cryptographic credentials without centralized identity provider dependencies.
The Role of Cybersecurity Education in Emerging Domains
Studying emerging areas equips security professionals to solve tomorrow’s architectural challenges:
Holistic Knowledge: Integrates technical, legal, and mathematical advances across quantum physics, AI algorithms, and distributed ledgers.
Future-Proofing Infrastructure: Prepares engineers to migrate legacy RSA implementations to post-quantum standards before quantum advantage occurs.
Adaptive Problem Solving: Fosters research-oriented mindsets required to evaluate novel attack vectors where static security playbooks do not yet exist.
Reinforce key concepts regarding post-quantum migration, zero trust verification, and decentralized ledgers before reading the FAQ:
Quick Review Verification
1. Why must organizations prepare for Post-Quantum Cryptography years before practical quantum computers exist?
Answer: Due to “Harvest Now, Decrypt Later” attacks. Adversaries are actively intercepting and storing encrypted high-value communications today, intending to decrypt the data once quantum computers capable of running Shor’s algorithm become operational. Migrating global cryptographic infrastructure requires years of transition time.
2. How does Micro-Segmentation support Zero Trust Architecture in cloud environments?
Answer: Micro-segmentation divides networks into granular, isolated zones down to individual workload containers. By enforcing strict security policies between internal microservices, it prevents lateral movement, containing a compromised workload within a tiny blast radius.
Emerging Areas in Cybersecurity – Frequently Asked Questions
What are “emerging areas” in cybersecurity, and why do they matter?
Emerging areas cover fast-evolving fields like AI-driven defense, post-quantum cryptography, zero-trust architectures, confidential cloud computing, and smart contract auditing. They matter because rapid digital evolution creates novel attack surfaces faster than traditional perimeter defenses can adapt.
Why are AI and ML becoming pivotal in cybersecurity?
Modern networks generate petabytes of telemetry that exceed human monitoring capacity. Machine learning automates high-speed anomaly detection, while security teams must simultaneously defend models against adversarial prompt injection and data poisoning.
What security challenges stem from IoT and Cyber-Physical Systems (CPS)?
Resource-constrained IoT microcontrollers lack processing power for heavy encryption, while CPS exploits trigger physical equipment destruction or safety hazards, blurring digital security with physical safety engineering.
What is quantum-safe cryptography?
Quantum-safe (post-quantum) cryptography uses mathematical problems (like high-dimensional lattice geometry) that remain computationally hard for both classical supercomputers and quantum computers to solve, replacing vulnerable RSA and ECC schemes.
How do Privacy-Enhancing Technologies (PETs) fit into cybersecurity?
PETs like Fully Homomorphic Encryption (FHE) and Zero-Knowledge Proofs (ZKPs) allow cloud analytics and identity checks on encrypted data without ever exposing underlying plaintext data secrets to processing servers.
How can students prepare for careers in emerging cybersecurity fields?
Build strong foundations in operating systems, networking, and applied mathematics, then layer specialized skills in cloud architecture, machine learning, reverse engineering, and hands-on lab experimentation.
Emerging Areas in Cybersecurity: Conclusion
Emerging areas such as post-quantum cryptography, zero trust architecture, and blockchain security represent the forefront of cybersecurity innovation. These fields address current and future challenges, ensuring that digital ecosystems remain robust and resilient in an era of rapid technological advancement. With comprehensive education and hands-on experience, cybersecurity professionals will continue to play a pivotal role in securing the digital future.
Continuous Adaptation: Upgrade cryptographic baselines and access policies as research standards evolve.
Zero Trust Enforcement: Eliminate assumed network perimeter trust across remote and multi-cloud environments.
Proactive Research: Evaluate early-stage technologies (PQC, AI safety, FHE) to build defensible long-term architectures.
1. What are emerging cybersecurity areas and why are they significant?
Answer: Emerging cybersecurity areas are rapidly developing sub-fields (AI defense, post-quantum crypto, zero trust, blockchain security) addressing novel technologies and threats. They are significant because they allow organizations to develop proactive defenses against next-generation attack vectors before legacy controls become obsolete.
2. How is artificial intelligence transforming the cybersecurity landscape in emerging areas?
Answer: AI enables real-time high-throughput log analysis, automated incident response orchestration (SOAR), and predictive threat scoring, while creating new security requirements to protect ML models against adversarial poisoning and prompt injection.
3. What role does the Internet of Things (IoT) play in shaping emerging cybersecurity trends?
Answer: IoT connects billions of resource-constrained hardware nodes, dramatically expanding corporate attack surfaces and driving demand for lightweight cryptography, edge AI monitoring, and zero-trust device access policies.
4. How does blockchain technology contribute to advancements in cybersecurity?
Answer: Blockchain provides immutable, tamper-resistant ledgers for recording decentralized identity credentials, verifying software supply chain provenance, and securing financial transactions without single points of failure.
5. What challenges does quantum computing pose to current cybersecurity measures?
Answer: Shor’s algorithm running on quantum hardware will efficiently solve prime factorization and discrete logarithms, breaking widespread public-key algorithms (RSA, ECC, Diffie-Hellman) and invalidating digital certificates.
6. How do emerging cybersecurity areas influence the development of future security policies?
Answer: They force governance frameworks to incorporate requirements for AI model safety, mandatory Software Bill of Materials (SBOM), zero-trust access controls, and post-quantum cryptographic migration timelines.
7. What innovative methods are being developed to secure cloud environments in emerging cybersecurity areas?
8. How can organizations leverage threat intelligence in the context of emerging cybersecurity areas?
Answer: By feeding dark web intelligence and active exploit feeds directly into automated SOAR playbooks and EDR agents, proactively blocking emerging threat actor TTPs before production systems are targeted.
9. What is the importance of research and development in driving emerging cybersecurity innovations?
Answer: R&D discovers mathematical primitives (post-quantum lattice ciphers, homomorphic encryption), designs new defensive architectures, and tests system resilience against novel attack vectors before adversaries exploit them.
10. How do emerging cybersecurity areas impact global digital transformation initiatives?
Answer: They establish the foundational digital trust required for societies to adopt cloud-native banking, autonomous transportation grids, telemedicine, and smart city automation safely.
Thought-Provoking Architectural Questions
1. How will the integration of AI and machine learning redefine threat detection in emerging domains?
Answer: Shifts detection from static rule matching to continuous autonomous reasoning. AI models will reconstruct full multi-hop attack timelines across cloud, network, and endpoint logs instantly, executing self-healing containment actions in milliseconds.
2. In what ways could quantum computing reshape current encryption methods?
Answer: Shor’s algorithm renders traditional public-key ciphers obsolete, forcing a global migration toward lattice-based Post-Quantum Cryptography (ML-KEM) and hardware Quantum Key Distribution (QKD) channels.
3. How might the growth of IoT devices create new vulnerabilities, and what strategies mitigate them?
Answer: Proliferation of unmanaged hardware nodes creates massive botnet recruitment pools. Mitigate using Zero Trust Network Access (ZTNA), lightweight hardware Roots of Trust (TPM), and automated edge firmware attestations.
4. What potential role does blockchain technology have in enhancing data integrity?
Answer: Provides decentralized append-only ledgers for recording cryptographically signed audit logs, verifying open-source package build provenance, and managing passwordless decentralized identities (DID).
5. How can emerging trends balance rapid innovation with robust privacy protections?
Answer: By embedding Privacy-Enhancing Technologies (PETs) like Differential Privacy and Fully Homomorphic Encryption (FHE) directly into software design, allowing analytics without exposing raw personal user data.
6. How will global regulatory changes influence the evolution of cybersecurity strategies?
Answer: Laws mandating software supply chain transparency (SBOMs) and strict AI safety compliance will compel companies to automate security governance via continuous Policy-as-Code pipelines.
7. What ethical considerations arise from using advanced surveillance technologies in cybersecurity?
Answer: Pervasive employee activity tracking and biometric monitoring risk infringing on personal privacy civil liberties. Organizations must enforce strict data minimization and transparent consent policies.
8. How might the convergence of cloud computing and emerging areas transform security architectures?
Answer: Replaces static perimeter firewalls with dynamic identity-bound micro-segmentation, confidential hardware enclaves, and automated cloud-native security orchestration engines.
9. What impact will autonomous systems have on the future of risk management?
Answer: Enables machine-speed incident containment, but requires robust guardrails to prevent autonomous defense agents from taking destructive actions due to false positive model hallucinations.
10. How can organizations prepare for cybersecurity challenges in critical infrastructure?
Answer: Conduct cyber-physical risk modeling, enforce strict air-gapped network segmentation between IT and OT, deploy passive anomaly sensors, and maintain manual mechanical safety overrides.
11. What role will workforce development play in supporting emerging cybersecurity areas?
Answer: Bridges the global talent deficit by training cross-disciplinary specialists in quantum algorithms, machine learning security, smart contract auditing, and cloud governance.
12. How can cross-industry collaboration accelerate innovation in emerging cybersecurity fields?
Answer: By pooling threat intelligence feeds across ISACs, standardizing open-source security tools, and collaborating on post-quantum cryptographic migration testbeds.
Numerical Engineering Problems & Solutions
Problem 1: Daily Expected Cyber Attacks & Poisson Zero-Attack Probability A cloud platform processes 10,000 network requests per day. Each request carries a 0.05% (0.0005) probability of containing a malicious attack payload. Calculate expected daily attacks, expected attacks over a 30-day month, and the Poisson probability P(0) of experiencing exactly 0 attacks on a given day.
Answer: Expected attacks total 5 daily (150 monthly), with a 0.67% probability of zero attacks occurring on any given day.
Problem 2: Classical Brute-Force Key Search Feasibility for 128-Bit Keys A symmetric cipher uses a 128-bit key (2^128 total space ≈ 3.4028 × 10^38 keys). A brute-force cluster tests 10^9 keys per second. Calculate total time required to search the entire key space in seconds and years (3.15 × 10^7 seconds/year).
Convert seconds to years: (3.4028 × 10^29) / (3.15 × 10^7) ≈ 1.08 × 10^22 years
Answer: Searching the key space requires 1.08 × 10^22 years, proving classical brute-force infeasibility.
Problem 3: Vulnerable IoT Node Reduction via Automated Patch Management An IoT fleet contains 2,000 connected devices, where 2% (40 devices) run outdated vulnerable firmware. An OTA firmware update resolves vulnerabilities on 80% of affected nodes. Calculate initial vulnerable nodes, remaining vulnerable nodes, and percentage reduction.
Answer: Patching reduces vulnerable nodes from 40 down to 8 devices (an 80% reduction).
Problem 4: Blockchain Transaction Verification Time Metrics A permissioned blockchain ledger processes 1,000 consensus transactions per day, with each transaction requiring 2 seconds of verification time. Calculate daily verification time in minutes and total annual verification duration in hours (365 days).
Answer: Verification requires 33.33 minutes per day, totaling 202.78 hours per year.
Problem 5: Calculating Phishing Click-Through Rate Reduction A security awareness program for 500 employees reduces phishing simulation click-through rates from 15% (75 clicks) down to 5% (25 clicks). Calculate initial clicks, post-training clicks, and overall percentage click reduction.
Answer: Phishing clicks dropped from 75 to 25 clicks, achieving a 66.67% reduction.
Problem 6: Calculating Annual Downtime Savings from Incident Response Automation Automated incident playbooks reduce average breach downtime from 120 minutes to 45 minutes per incident. For an enterprise experiencing 12 incidents per year, calculate time saved per incident, total annual downtime saved in minutes and hours.
Solution:
Time saved per incident = 120 minutes – 45 minutes = 75 minutes saved
Total annual time saved in minutes = 75 minutes × 12 incidents = 900 minutes/year
Convert to hours = 900 / 60 = 15.0 hours saved per year
Answer: Automation saves 75 minutes per incident, eliminating 15.0 hours of annual downtime.
Problem 7: Net Financial Savings from Cybersecurity Capital Upgrades A firm spends $200,000 annually on cybersecurity upgrades. Baseline breach losses average 4 breaches per year at $500,000 per incident ($2,000,000 baseline loss). Upgrades reduce breach severity costs by 70%. Calculate pre-upgrade breach cost, post-upgrade breach cost, and net annual savings.
Solution:
Baseline annual breach loss = 4 × $500,000 = $2,000,000/year
Answer: Upgrades reduce breach loss to $600,000, generating $1,400,000 in gross savings ($1,200,000 net annual savings).
Problem 8: Quantum Key Search Feasibility with Grover’s Algorithm A post-quantum symmetric cipher uses a 256-bit key (2^256 space ≈ 1.1579 × 10^77 keys). Grover’s quantum search reduces key evaluation complexity to 2^128 operations. A quantum computer evaluates 10^12 keys per second. Calculate search duration in seconds and years.
Search time in seconds = (3.4028 × 10^38) / 10^12 = 3.4028 × 10^26 seconds
Convert seconds to years: (3.4028 × 10^26) / (3.15 × 10^7) ≈ 1.08 × 10^19 years
Answer: Quantum key search requires approximately 1.08 × 10^19 years, confirming robust post-quantum security for 256-bit symmetric keys.
Problem 9: AI False Positive Log Alert Reduction A cloud SIEM processes 500,000 log entries daily, where 0.1% (500 logs) trigger potential threat alerts. An AI alert engine reduces false positives by 80%. Calculate initial daily alerts, final alert count, and percentage alert noise reduction.
Answer: AI filtering reduces daily alerts from 500 down to 100 actionable alerts (an 80% noise reduction).
Problem 10: Expected Risk Loss Savings from Zero-Trust Implementation Risk modeling evaluates an enterprise asset valued at $1,000,000. Implementing Zero Trust policies reduces annual breach probability from 8% (0.08) down to 3% (0.03). Calculate expected annual loss before and after policy implementation, annual dollar savings, and percentage risk reduction relative to baseline loss.
Solution:
Baseline expected annual loss = 0.08 × $1,000,000 = $80,000/year
Answer: Zero Trust lowers expected risk loss by $50,000 per year (a 62.5% reduction in expected loss).
Problem 11: Cumulative Loss Prevention & ROI for Security Awareness Training A cybersecurity training module lasts 90 minutes per employee (450 aggregate hours across 300 employees). Training costs $50 per employee ($15,000 total). Trained employees prevent an estimated $2,000 in breach losses per employee per year ($600,000 total annual prevention). Calculate cumulative annual loss prevention, net savings, and ROI percentage.
Solution:
Total training cost = 300 × $50 = $15,000
Cumulative annual loss prevention = 300 × $2,000 = $600,000/year
Net financial benefit = $600,000 – $15,000 = $585,000/year
ROI percentage = ($585,000 / $15,000) × 100 = 3,900.0%
Answer: The program generates $600,000 in annual loss prevention ($585,000 net benefit), achieving an ROI of 3,900%.
Problem 12: Daily False Alarm Reduction via SIEM Upgrade A network security system evaluates 1,000,000 events daily with an initial false alarm rate of 0.2% (2,000 false alarms). Upgrading the SIEM rule engine reduces false alarms by 75%. Calculate initial false alarms, new daily false alarm count, and daily alarms eliminated.
Answer: The SIEM upgrade eliminates 1,500 false alarms daily, reducing false alarms to 500 alarms per day.
Emerging Areas in Cybersecurity — Summary & Wrap-Up
Emerging cybersecurity areas—including post-quantum cryptography, zero trust architectures, AI-driven defense, and blockchain security—represent the moving frontier of digital defense. By understanding evolving attack surfaces, adapting governance frameworks, and mastering next-generation technical controls, security professionals build future-ready resilience across complex digital ecosystems.