
Cybersecurity Awareness and Training Education is the art of shaping tiny decisions—because tiny decisions scale. The diagram shows how awareness becomes habit. Learners bring in inputs such as basic digital familiarity and structured materials, but their learning is steered by controls: organizational rules, policy requirements, and clear expectations about what must never be done and what must always be checked. Mechanisms like guided instruction and training platforms provide repetition with realism—scenarios, examples, and practice that mirror everyday moments: an unexpected message, a suspicious link, a request for credentials, a “quick” workaround that feels convenient. The output is not technical wizardry; it is steady judgment. Learners begin to recognize social engineering cues, handle information more carefully, and respond consistently under pressure—so security becomes part of routine conduct rather than a poster on the wall.
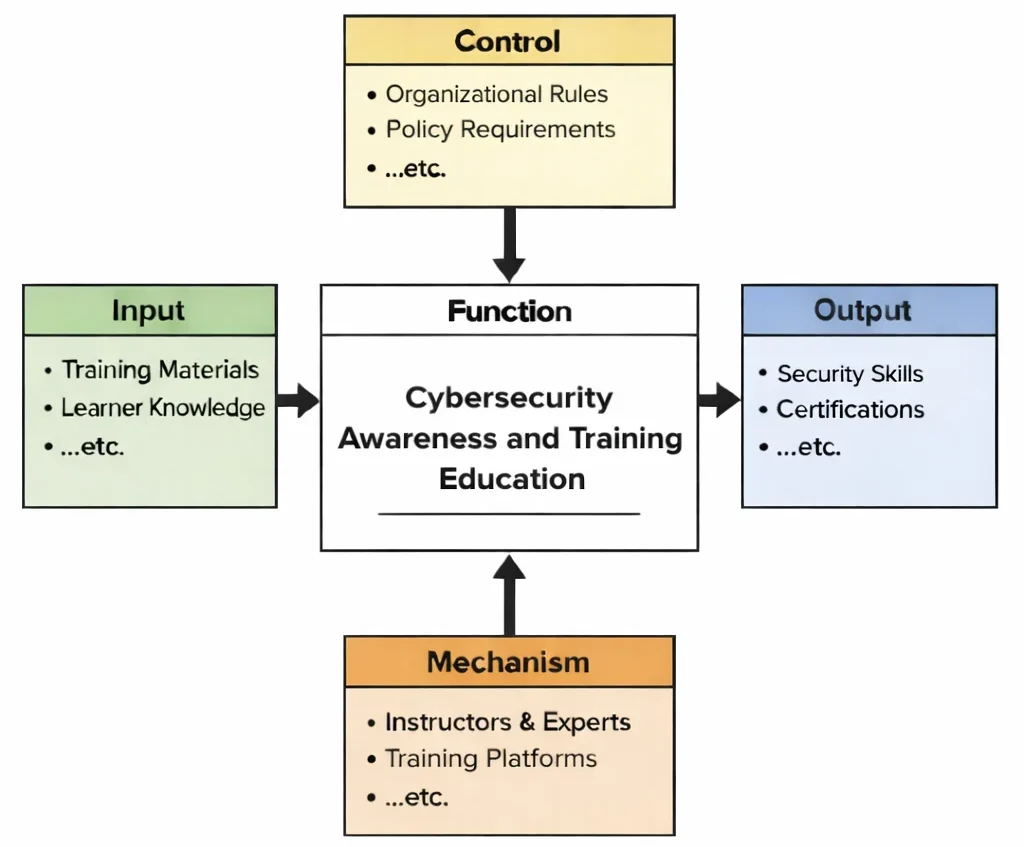
This IDEF0 (Input–Control–Output–Mechanism) diagram summarizes Cybersecurity Awareness and Training Education as a structured transformation. Inputs include training materials and learner baseline knowledge of common digital habits. Controls include organizational rules, policy requirements, and required behaviors that define what “secure conduct” looks like in daily work and study. Mechanisms include instructors, experts, training platforms, and practice activities (such as scenarios and simulations) that reinforce correct responses. Outputs include improved security skills, safer day-to-day behavior, and readiness for assessments or role-based certifications.
Interactive Check: Intro & System Concepts
Verify your understanding of how awareness programs transform everyday human behavior into reliable security habits:
Introductory Concept Verification
1. Why is human error considered one of the primary vectors in cybersecurity incidents?
Answer: Attackers frequently bypass complex technical firewalls by manipulating human trust through social engineering, urgency cues, and spear-phishing. Because people interact with digital systems daily, tiny decision errors can inadvertently grant attackers credential access or internal network footholds.
2. What is the intended practical output of Cybersecurity Awareness and Training Education?
Answer: Steady judgment and routine conduct: learners who recognize social engineering cues, handle information carefully under pressure, and instinctively follow security policies instead of taking risky shortcuts.
Cybersecurity awareness and training focus on equipping individuals and organizations with the knowledge and skills needed to identify, prevent, and respond to cyber threats. Since human error is one of the leading causes of cybersecurity incidents, creating a culture of security through education and awareness is crucial for minimizing risks.
This image visualizes cybersecurity awareness as a shared, human-centered responsibility. Learners sit at computer desks in a training-room setting while a luminous globe with a central padlock hovers above a digital platform, suggesting that modern security protects systems worldwide—and depends on informed users everywhere. The surrounding symbols (shields, alerts, network icons, and authentication imagery) represent common topics covered in training: safe passwords, phishing recognition, secure Wi-Fi use, data protection, and incident reporting. The composition emphasizes that good security is not only about tools and software, but also about habits, judgment, and teamwork—building a security-minded culture through education and practice.
Building Cyber Resilience: Security Awareness Navigation
Discover how Cybersecurity Awareness and Training mitigates human risk vectors across the Cybersecurity cluster. Each card details phishing simulation campaigns, password hygiene, social engineering defense, and security culture governance.
Cybersecurity Overview
Presents the overall system architecture, mapping how human behavior and security awareness complement technical defense-in-depth controls.
Network Security
Examines educating users on recognizing insecure public Wi-Fi networks, verifying VPN connections, and avoiding rogue wireless access points.
Application Security
Focuses on developer secure coding hygiene, training software teams to avoid hardcoded credentials and validate inputs against injection flaws.
Cloud Security
Details training cloud administrators to prevent storage bucket misconfigurations and avoid sharing long-lived IAM access keys.
Endpoint Security
Covers training users to enable automatic software updates, lock unattended workstations, and recognize device malware warnings.
Identity & Access Management
Governs user adoption of Multi-Factor Authentication (MFA), password manager utilization, and avoiding password reuse across accounts.
Cryptography
Explains the importance of end-to-end encrypted messaging, verifying HTTPS certificate validity, and protecting private recovery keys.
Incident Response & Forensics
Trains employees to immediately report suspicious phishing emails or anomalous system behavior to the security operations center (SOC).
Threat Intelligence
Translates active phishing campaigns and social engineering trends into engaging, timely awareness updates for staff members.
Ethical Hacking & Pen Testing
Utilizes controlled penetration testing and red-teaming findings to demonstrate real-world social engineering vulnerabilities to executives.
Security Awareness
Focuses on phishing simulation, social engineering defense, password hygiene, remote work security, gamified learning, and security culture development.
Policy & Governance
Aligns awareness training modules with organizational acceptable use policies, data handling rules, and mandatory regulatory compliance guidelines.
CPS Security
Educates plant operators and engineers to recognize physical tampering, USB drop attacks, and social engineering targeting industrial control panels.
OT Security
Trains operational technology personnel on air-gapped network boundaries, removable media hygiene, and physical safety protocol adherence.
AI & ML in Security
Addresses emerging AI-driven phishing threats (deepfake voice/video spear-phishing) and trains staff to verify high-stakes financial requests through out-of-band channels.
Emerging Areas
Explores cultivating security awareness across decentralized remote workforces and adapting training for next-generation digital interfaces.
Key Topics in Cybersecurity Awareness and Training
Effective awareness programs cover fundamental human-centric risk areas:
Recognizing Phishing and Social Engineering Attacks
- Phishing: Training users to identify deceptive emails or messages designed to harvest credentials. Common signs include misspelled sender domains, urgent financial demands, and suspicious hyperlinks.
- Social Engineering: Educating individuals to spot psychological manipulation tactics such as pretexting, baiting, and tailgating.
Secure Password Practices
- Enforcing strong, unique passwords across accounts using enterprise password managers to eliminate password reuse and predictable patterns.
Regular Security Awareness Campaigns
- Executing periodic simulated phishing tests, interactive gamified quizzes, and security newsletters to reinforce safe digital habits.
Understanding Security Policies
- Ensuring employees understand acceptable use policies, data classification rules, and mandatory incident reporting protocols.
Safe Internet & Device Security
- Enforcing VPN usage on public Wi-Fi, enabling automatic software updates, installing endpoint protection, and locking unattended workstations.
Interactive Quick Review: Human Risk Mitigation
Reinforce key concepts regarding phishing detection, social engineering defense, and password hygiene before reading the FAQ:
Quick Review Verification
1. Why are simulated phishing campaigns more effective than passive security lectures?
Answer: Simulated campaigns provide experiential learning in realistic environments. When an employee clicks a simulated phishing link, they receive immediate, contextual teachable moments rather than forgetting abstract lecture theory, transforming passive knowledge into active skepticism.
2. What role do enterprise password managers play in strengthening organizational security posture?
Answer: Password managers eliminate human password fatigue by generating long, cryptographically random, and unique passwords for every single application, stopping credential-stuffing and password-reuse attacks across third-party services.
Cybersecurity Awareness – Frequently Asked Questions
What is cybersecurity awareness, and why does it matter for everyday users?
Cybersecurity awareness is the understanding of common digital risks and the everyday behaviors that help protect devices, data, and online identities. It matters because most cyber incidents start with human error.
What are the most common online threats users should know about?
Phishing emails designed to steal credentials, malware, ransomware, identity theft, social engineering phone scams, and data leaks resulting from weak passwords or misconfigured accounts.
How do strong passwords and multi-factor authentication improve security?
Unique passwords generated by password managers stop credential reuse, while multi-factor authentication (MFA) requires a secondary code or passkey, preventing account access even if a password is stolen.
How can I recognize a phishing email or suspicious message?
Look for manufactured urgency, unfamiliar senders, grammar errors, mismatched destination URLs upon hovering, and unexpected requests for sensitive personal information.
What safe habits should be practiced on public Wi-Fi and shared devices?
Avoid accessing sensitive banking or work accounts on public Wi-Fi unless using a trusted VPN, always verify HTTPS, log out after use, and never save credentials in shared browser profiles.
Why are software updates and backups important?
Software updates patch known security vulnerabilities actively targeted by hackers, while offline or cloud backups ensure rapid recovery from ransomware attacks without paying extortion ransoms.
Cybersecurity Awareness and Training: Conclusion
Cybersecurity awareness and training are vital for reducing human-related vulnerabilities and strengthening an organization’s overall security posture. Regular, engaging, and up-to-date training ensures that employees and individuals remain vigilant and informed about evolving cyber threats.
- Continuous Reinforcement: Replace one-time annual compliance videos with ongoing micro-learning and monthly phishing simulations.
- Empower Reporting: Cultivate a blameless reporting culture where employees feel safe reporting accidental clicks instantly.
- Measure Behavior: Track click rates and reporting frequencies to gauge awareness program effectiveness over time.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is cybersecurity awareness and why is it essential for organizations?
Answer: Cybersecurity awareness refers to employee understanding of cyber threats and safe digital practices. It is essential because informed staff act as the organization’s first line of defense against social engineering and human error.
2. How do phishing simulations contribute to effective cybersecurity awareness?
Answer: Phishing simulations test staff readiness in controlled environments, exposing vulnerabilities and providing immediate contextual training moments to improve threat recognition.
3. What are some common social engineering tactics highlighted in awareness programs?
Answer: Tactics include spear-phishing, pretexting (impersonating authority figures), baiting (malicious USB drives), and tailgating (physically following staff into secure areas).
4. How does regular cybersecurity awareness training impact an organization’s security posture?
Answer: Regular training fosters a vigilant security culture, reducing human error, lowering breach susceptibility, and ensuring proactive reporting of suspicious communications.
5. Why is employee behavior considered a critical factor in cybersecurity defense?
Answer: Humans are often targeted because software firewalls are harder to penetrate than human trust and curiosity. A single careless click can compromise an entire corporate network.
6. How can organizations measure the effectiveness of their awareness training programs?
Answer: By tracking simulation click rates, measuring employee phishing report frequencies, evaluating quiz scores, and auditing incident response response times.
7. What role do digital communications and social media play in cybersecurity awareness?
Answer: They serve as channels for sharing real-time threat alerts and security tips, while also representing exposure vectors where oversharing aids social engineering reconnaissance.
8. How does cybersecurity awareness training help in mitigating data breach risks?
Answer: By teaching safe password hygiene, cautious email handling, and proper data storage, preventing unauthorized access resulting from credential compromise.
9. What are the long-term benefits of a strong cybersecurity awareness culture?
Answer: Reduced incident frequencies, lower financial losses, enhanced regulatory compliance, and increased customer trust in the organization’s data stewardship.
10. How do awareness initiatives integrate with broader IT security strategies?
Answer: They address the human layer, complementing technical firewalls and IAM policies to create a cohesive defense-in-depth posture.
Thought-Provoking Architectural Questions
1. How might evolving cyber threats reshape the future of cybersecurity awareness training?
Answer: The rise of AI-generated deepfake voice and video spear-phishing will require training to move beyond text emails toward real-time biometric and out-of-band verification protocols.
2. What impact does the rise of remote work have on cybersecurity awareness?
Answer: Remote work blurs personal and professional boundaries, increasing risks from unmanaged home Wi-Fi and personal device usage, demanding specialized home-office security training.
3. How can organizations balance robust awareness with the risk of employee information overload?
Answer: By replacing lengthy annual seminars with bite-sized, role-based micro-learning modules delivered continuously throughout the year.
4. In what ways can gamification enhance the effectiveness of awareness training?
Answer: Incorporating points, badges, and escape-room style phishing challenges increases engagement, making security education enjoyable and memorable.
5. How can artificial intelligence be integrated into awareness programs?
Answer: AI analyzes individual user simulation failure patterns to automatically assign customized, targeted micro-training modules addressing their specific weaknesses.
6. What are the long-term benefits of cultivating a strong cybersecurity culture?
Answer: Institutional resilience where security behavior becomes second nature, drastically lowering breach probabilities and fostering external customer trust.
7. How does the human factor contribute to vulnerabilities, and how can it be addressed?
Answer: Human fatigue and curiosity create openings. Address this by pairing continuous education with technical friction reducers (password managers, single sign-on).
8. In what ways can international collaboration enhance global security awareness?
Answer: Cross-border sharing of emerging social engineering trends and standardized awareness frameworks strengthens defensive postures globally.
9. How do digital channels influence threat perception among employees?
Answer: Frequent, transparent updates build healthy vigilance, whereas alarmist or overly technical warnings can breed employee apathy or distrust.
10. What ethical considerations arise when enforcing workplace awareness?
Answer: Balancing organizational monitoring and phishing simulation tracking against employee privacy rights, avoiding punitive naming-and-shaming tactics.
11. How can crisis simulation exercises enhance awareness and preparedness?
Answer: Tabletop crisis simulations test executive and staff decision-making under high-pressure simulated breach conditions, refining communication protocols.
12. What strategies ensure awareness training remains current with evolving threats?
Answer: Integrating real-time threat intelligence feeds into monthly curriculum updates and reviewing simulation metrics continuously.
Numerical Engineering Problems & Solutions
Problem 1: Calculating Phishing Simulation Click Rate and Reduction
An organization of 500 employees conducts a phishing simulation where 20% of staff click the malicious link. A follow-up targeted training module reduces this click rate by 50%. Calculate affected employees before and after training, and the overall percentage reduction.
An organization of 500 employees conducts a phishing simulation where 20% of staff click the malicious link. A follow-up targeted training module reduces this click rate by 50%. Calculate affected employees before and after training, and the overall percentage reduction.
Solution:
- Initial employees affected = 500 × 0.20 = 100 employees
- Employees affected after 50% reduction = 100 × 0.50 = 50 employees
- Overall percentage reduction = ((100 – 50) / 100) × 100 = 50.0% reduction
Problem 2: Estimating Training ROI for Phishing Breach Prevention
An awareness program costs $25 per employee for 600 employees ($15,000 total). The program reduces phishing breaches (costing $5,000 each) by 80% from an expected baseline of 10 breaches per year. Calculate annual savings and Return on Investment (ROI).
An awareness program costs $25 per employee for 600 employees ($15,000 total). The program reduces phishing breaches (costing $5,000 each) by 80% from an expected baseline of 10 breaches per year. Calculate annual savings and Return on Investment (ROI).
Solution:
- Total training cost = 600 × $25 = $15,000
- Baseline annual breach cost = 10 breaches × $5,000 = $50,000
- Annual savings (80% reduction) = $50,000 × 0.80 = $40,000/year
- Net financial gain = $40,000 – $15,000 = $25,000
- ROI percentage = ($25,000 / $15,000) × 100 ≈ 166.67%
Problem 3: Calculating Increase in Employee Phishing Confidence
In a security survey of 500 employees, 50% initially feel confident identifying phishing emails. After awareness training, 70% feel confident. Calculate employee counts before and after, and the percentage increase in confident staff.
In a security survey of 500 employees, 50% initially feel confident identifying phishing emails. After awareness training, 70% feel confident. Calculate employee counts before and after, and the percentage increase in confident staff.
Solution:
- Initial confident employees = 500 × 0.50 = 250 employees
- Post-training confident employees = 500 × 0.70 = 350 employees
- Absolute increase = 350 – 250 = 100 additional confident employees
- Percentage increase = (100 / 250) × 100 = 40.0%
Problem 4: Calculating Weeks Required to Lower Phishing Click Rate Below Threshold
A weekly phishing simulation campaign starts with a 20% click rate. The click rate decreases by 2 percentage points each week. Calculate the number of weeks required for the click rate to fall below 5%.
A weekly phishing simulation campaign starts with a 20% click rate. The click rate decreases by 2 percentage points each week. Calculate the number of weeks required for the click rate to fall below 5%.
Solution:
- Click rate equation after n weeks = 20% – 2% × (n – 1)
- Set inequality: 20 – 2(n – 1) < 5 → 20 – 2n + 2 < 5 → 22 – 2n < 5
- Solve for n: 2n > 17 → n > 8.5 weeks
Problem 5: Estimating Cost Savings from Faster Incident Response Due to Awareness
Awareness training improves employee reporting speed, decreasing average incident response time from 60 minutes to 30 minutes. If downtime costs $100 per minute, calculate cost savings per incident and total annual savings across 50 reported incidents.
Awareness training improves employee reporting speed, decreasing average incident response time from 60 minutes to 30 minutes. If downtime costs $100 per minute, calculate cost savings per incident and total annual savings across 50 reported incidents.
Solution:
- Time saved per incident = 60 min – 30 min = 30 minutes saved
- Cost saving per incident = 30 minutes × $100/min = $3,000 saved/incident
- Total annual savings (50 incidents) = 50 × $3,000 = $150,000/year
Problem 6: Calculating Incident Reduction from Phishing Awareness
Before training, 100 employees exhibit a 30% probability of falling for phishing scams. After training, the probability drops to 10%. Calculate expected incidents before and after training, and the percentage reduction.
Before training, 100 employees exhibit a 30% probability of falling for phishing scams. After training, the probability drops to 10%. Calculate expected incidents before and after training, and the percentage reduction.
Solution:
- Pre-training expected incidents = 100 × 0.30 = 30 incidents
- Post-training expected incidents = 100 × 0.10 = 10 incidents
- Net reduction = 30 – 10 = 20 incidents avoided
- Percentage reduction = (20 / 30) × 100 ≈ 66.67%
Problem 7: Calculating Net Economic Benefit of Employee Security Training
A security awareness session lasts 2 hours with an employee labor cost of $40 per hour. The training increases productivity and prevents mistakes, yielding a monetary value gain of $500 per employee on an annual salary basis. Calculate net benefit per employee.
A security awareness session lasts 2 hours with an employee labor cost of $40 per hour. The training increases productivity and prevents mistakes, yielding a monetary value gain of $500 per employee on an annual salary basis. Calculate net benefit per employee.
Solution:
- Training cost per employee = 2 hours × $40/hour = $80.00
- Productivity/risk gain value = $500.00
- Net benefit per employee = $500.00 – $80.00 = $420.00
Problem 8: Estimating Preventive Value from Security Newsletter Engagement
A company sends 1,000 security newsletters monthly. The open rate is 35%, and the click-through rate on opened emails is 10%. Each click represents an employee avoiding a risky link that prevents a breach worth $2,000. Calculate monthly clicks and total preventive value.
A company sends 1,000 security newsletters monthly. The open rate is 35%, and the click-through rate on opened emails is 10%. Each click represents an employee avoiding a risky link that prevents a breach worth $2,000. Calculate monthly clicks and total preventive value.
Solution:
- Newsletter opens = 1,000 × 0.35 = 350 opens
- Newsletter clicks (engagements) = 350 × 0.10 = 35 clicks
- Total preventive value = 35 clicks × $2,000 = $70,000/month
Problem 9: Calculating Absolute Increase in Reported Phishing Attempts
During Cybersecurity Awareness Month, reported phishing attempts increase by 150% from the previous month’s baseline of 40 reports. Calculate the new total number of reported attempts and absolute increase.
During Cybersecurity Awareness Month, reported phishing attempts increase by 150% from the previous month’s baseline of 40 reports. Calculate the new total number of reported attempts and absolute increase.
Solution:
- Absolute increase in reports = 40 reports × 1.50 = 60 new reports
- New total reported attempts = 40 + 60 = 100 reports
Problem 10: Calculating Relative Risk Reduction from Phishing Training
An untrained employee exhibits a 25% chance of clicking a phishing email. Security awareness training reduces this risk down to 5%. Calculate relative risk reduction percentage.
An untrained employee exhibits a 25% chance of clicking a phishing email. Security awareness training reduces this risk down to 5%. Calculate relative risk reduction percentage.
Solution:
- Absolute drop = 25% – 5% = 20 percentage points
- Relative risk reduction = (20% / 25%) × 100 = 80.0% reduction
Problem 11: Calculating Daily Phishing Email Volume and Click Reduction
A simulation notes that 1 out of every 20 emails received enterprise-wide is a phishing attempt. If an employee receives 200 emails per day, calculate phishing emails received. If the employee click rate drops from 15% to 3% after training, calculate expected daily clicks before and after training.
A simulation notes that 1 out of every 20 emails received enterprise-wide is a phishing attempt. If an employee receives 200 emails per day, calculate phishing emails received. If the employee click rate drops from 15% to 3% after training, calculate expected daily clicks before and after training.
Solution:
- Phishing emails per day = 200 emails / 20 = 10 phishing emails received
- Pre-training daily clicks = 10 × 0.15 = 1.5 clicks
- Post-training daily clicks = 10 × 0.03 = 0.3 clicks
Problem 12: Calculating Absolute Increase in Suspicious Email Reporting Rate
A cybersecurity program increases the suspicious email reporting rate from 5% to 20% among an employee base of 800 staff members. Calculate number of reports before and after training, and the absolute increase in reports.
A cybersecurity program increases the suspicious email reporting rate from 5% to 20% among an employee base of 800 staff members. Calculate number of reports before and after training, and the absolute increase in reports.
Solution:
- Pre-training reports = 800 employees × 0.05 = 40 reports
- Post-training reports = 800 employees × 0.20 = 160 reports
- Absolute increase in reports = 160 – 40 = 120 additional reports
Cybersecurity Awareness and Training — Summary & Wrap-Up
Cybersecurity awareness and training are vital for reducing human-related vulnerabilities and strengthening an organization’s overall security posture. Regular, engaging, and up-to-date training ensures that employees and individuals remain vigilant and informed about evolving cyber threats, transforming human instinct into a reliable defensive barrier.