
Application Security (AppSec) Education is the habit of building software as if it will be used in the real world—because it will. The diagram shows how that habit is formed. Learners arrive with inputs: programming knowledge, sample applications, and study resources. But AppSec is not learned by memorizing a list of flaws; it is shaped by controls—secure coding standards, policy requirements, and the discipline of “prove it works” through repeatable checks. With mechanisms like guided labs, code review practice, and security testing tools, students learn to see an application the way an attacker might: where inputs enter, where trust is assumed, and where mistakes become openings. The output is a practical kind of confidence: learners who can prevent vulnerabilities early, detect issues quickly, and design software that treats security as part of quality—not an emergency patch applied at the end.
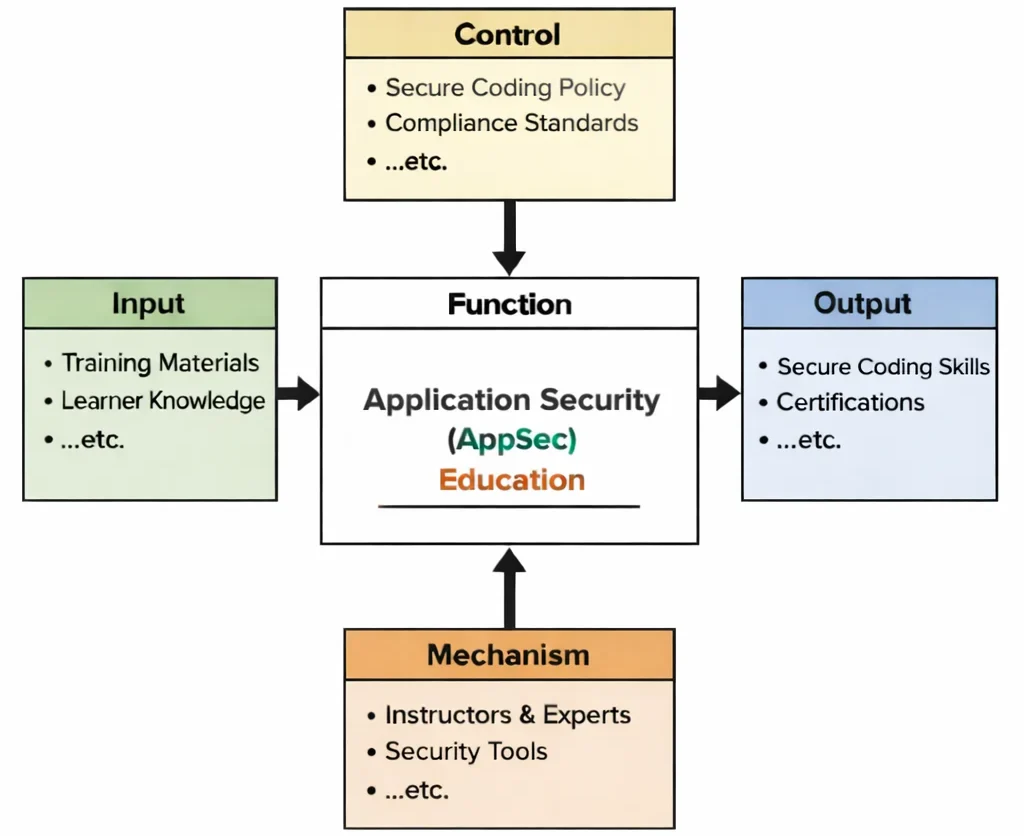
This IDEF0 (Input–Control–Output–Mechanism) diagram presents Application Security (AppSec) Education as a structured transformation. Inputs include training materials, code examples, and learner knowledge of software fundamentals. Controls include security standards, secure coding guidelines, organizational policies, and compliance expectations that define “acceptable risk” and required practices. Mechanisms include instructors, labs, testing tools (such as static/dynamic analysis), code review workflows, and practice environments that allow learners to learn by building and fixing. Outputs include practical AppSec capability: identifying common vulnerabilities, applying secure design principles, writing safer code, validating fixes, and integrating security into the development lifecycle.
Interactive Check: Intro & System Concepts
Verify your understanding of how secure development habits and controls transform raw software code into resilient applications:
Introductory Concept Verification
1. Why is Application Security considered a quality habit rather than an emergency patch?
Answer: Applying security controls late in the deployment cycle is exponentially more expensive and prone to missing architectural logic flaws. Integrating AppSec from the design phase (“Shift Left”) treats vulnerability prevention as an inherent component of software quality, ensuring security scales with release velocity.
2. In the IDEF0 AppSec framework, what distinguishes “Controls” from “Mechanisms”?
Answer: “Controls” define the rules and standards (secure coding guidelines, compliance frameworks, policy baselines), whereas “Mechanisms” are the operational tools and enablers (SAST/DAST scanners, code review platforms, instructors, and hands-on lab environments) used to execute those standards.
Application security (AppSec) is the first and last line of defense for modern software. As organizations ship continuously through DevOps and CI/CD, attackers increasingly target the application layer to steal data, interrupt services, or escalate privileges. Effective AppSec “shifts left” into design and coding and “stays right” in production—protecting the software throughout its lifecycle.
Practical AppSec blends people, process, and tooling. Teams use threat intelligence to prioritize real risks, apply cryptography correctly (keys, mTLS, at-rest/in-transit), enforce identity & access management for least privilege, and integrate controls with network security. This reduces exposure to injection, XSS, CSRF, IDOR, SSRF, and other common weaknesses, while meeting security & compliance obligations in regulated environments.
Architectures have changed, so defenses must too. Serverless functions, containers, cloud networking, and edge platforms dissolve the traditional perimeter—security must be embedded into code, configs, and runtime (policy-as-code, least-privileged roles, signed artifacts). AI-assisted tooling in AI & ML for cybersecurity now helps find flaws earlier and triage faster, while insights from emerging areas keep teams ahead of new techniques.
Resilience spans the whole stack and team. Incident response & forensics investigate anomalies and guide rapid containment; endpoint and OT controls protect the hosts your apps run on; security awareness, clear policies, and ethical hacking reduce human-error and validate defenses. Performance choices are evaluated alongside risk (see performance tuning), and safety-critical cyber-physical systems get extra safeguards to avoid real-world harm.
Finally, AppSec is increasingly data-driven. Using data science and big-data analytics, teams mine logs and telemetry to prioritize vulnerabilities, detect abuse, and measure what matters—fix rates, time-to-remediate, and exploit reduction. Supply-chain security (SBOMs, signature verification), secrets management, and policy automation turn best practices into repeatable guardrails that scale with your delivery pace.
This futuristic illustration presents application security as a shared, hands-on practice. At the center, a bright padlock symbol sits within a hexagonal frame above a digital platform, suggesting a secured application core or protected codebase. Around it, multiple screens display security dashboards, binary streams, and interface elements labeled with security themes, while shield and lock icons reinforce the idea of layered protection. People seated at workstations with laptops represent developers and security teams collaborating—reviewing code, monitoring risks, and applying safeguards throughout the software lifecycle. The overall scene conveys secure-by-design development: preventing vulnerabilities, strengthening authentication and access controls, and protecting user data as applications are built, deployed, and maintained.
Building Cyber Resilience: Application Security Navigation
Discover how Application Security embeds security gates, input validation boundaries, and runtime protection layers across the Cybersecurity cluster. Each card details static/dynamic scanning, API authorization, secrets rotation, and software supply chain integrity.
Cybersecurity Overview
Presents the overarching system framework, mapping how application-layer controls integrate with network perimeters, endpoint protection, and risk governance.
Network Security
Examines micro-segmentation, Web Application Firewalls (WAF), mutual TLS (mTLS) service-to-service communication, and ingress filtering for API endpoints.
Application Security
Focuses on SAST/DAST/SCA security gates, OWASP Top 10 mitigation (SQLi, XSS, CSRF, IDOR), secure SDLC automation, API authorization, and RASP defenses.
Endpoint Security
Covers host-level application isolation, runtime container security, EDR hook integration, and protecting client-side binaries from reverse engineering.
Cloud Security
Details securing cloud-native serverless functions, container image scanning, Cloud Security Posture Management (CSPM), and IAM workload identity federation.
Identity & Access Management
Governs OAuth2/OIDC token verification, fine-grained RBAC/ABAC/ReBAC permission evaluation, session cookie flags, and JWT claim validation.
Cryptography
Applies field-level payload encryption, AES-GCM envelope encryption for sensitive data, secure password hashing (Argon2/bcrypt), and KMS key rotation.
Incident Response & Forensics
Orchestrates application-level decision logging, auditing payload tampering, analyzing web server crash dumps, and executing rapid hotfix deployments.
Threat Intelligence
Feeds active CVE exploit feeds and known attack patterns into automated SCA scanners to prioritize third-party library patches dynamically.
Ethical Hacking & Pen Testing
Executes automated and manual dynamic application security testing (DAST), business logic abuse testing, and API fuzzing before production releases.
Cybersecurity Awareness
Trains software developers in secure coding hygiene, threat modeling workshops (STRIDE), and recognizing common web vulnerability patterns.
Policy & Governance
Enforces OWASP SAMM/ASVS benchmarks, mandatory CI/CD security gate thresholds, Software Bill of Materials (SBOM) tracking, and vulnerability patch SLAs.
CPS Security
Protects embedded application software running inside cyber-physical hardware, enforcing memory safety, signed firmware updates, and input bounds checking.
OT Security
Safeguards industrial HMI software applications and supervisory interfaces against unauthorized command injection and memory buffer overflows.
AI & ML in Security
Leverages AI transformers for automated code review, static vulnerability triage, and detecting anomalous API request payloads at the application boundary.
Emerging Areas
Investigates securing LLM application interfaces (OWASP Top 10 for LLMs), prompt injection defense, web-assembly sandboxing, and supply-chain attestations (SLSA).
Core Technical Domains in Application Security
Establishing robust application security requires embedding defensive controls across code construction, delivery pipelines, and runtime execution environments:
- Secure Coding Practices & Vulnerability Prevention:
- Input Validation & Injection Defense: Enforcing strict server-side type checking, parameterized SQL queries (prepared statements), and ORM abstraction to eliminate SQL, Command, and LDAP injection.
- Cross-Site Scripting (XSS) & Request Forgery (CSRF): Context-aware output encoding/escaping, enforcing strict Content Security Policies (CSP), and utilizing SameSite=Strict cookies with anti-CSRF synchronizer tokens.
- Insecure Direct Object References (IDOR): Validating user authorization context on every server-side data fetch rather than trusting client-supplied record keys or URL parameters.
- Secure SDLC & CI/CD Security Gates (DevSecOps):
- Static Application Security Testing (SAST): Automated source code analysis (Semgrep, SonarQube) running inside pull requests to flag insecure functions and hardcoded credentials.
- Software Composition Analysis (SCA) & SBOM: Scanning third-party dependencies for known vulnerabilities (Trivy, Snyk) and generating CycloneDX/SPDX Software Bill of Materials (SBOM) per build.
- Secret Detection & IaC Scanning: Scanning repository history for leaked API keys (Gitleaks, TruffleHog) and auditing infrastructure configuration files (Checkov).
- API Security & Authorization Architectures:
- Token Verification & Session Hygiene: Validating asymmetric JWT signatures (RS256), enforcing short-lived access tokens, and managing refresh token rotation inside HttpOnly/Secure cookies.
- Fine-Grained Authorization: Applying Role-Based Access Control (RBAC), Attribute-Based Access Control (ABAC), or Relationship-Based Access Control (ReBAC / Zanzibar model) at the resolver layer.
- Rate-Limiting & Idempotency: Rate-limiting public routes by IP/token and requiring unique
Idempotency-Keyheaders on POST requests to prevent double-submit resource duplication.
- Runtime Protection & Supply Chain Integrity:
- Runtime Application Self-Protection (RASP) & SSRF Guards: Wrapping outbound HTTP calls with strict IP/domain allowlists to block Server-Side Request Forgery (SSRF) targeting cloud IMDS endpoints (169.254.169.254).
- Artifact Signing: Digitally signing container images and build artifacts (Sigstore Cosign) to enforce keyless OIDC verification at cluster admission.
Secure SDLC CI/CD Workflow Specification
Below is a reference GitHub Actions workflow enforcing SAST, secret detection, SCA, container scanning, DAST baseline, and SBOM generation inside pull requests:
# AppSec pipeline: SAST + Secrets + SCA/IaC + Container + (optional) DAST + SBOM
name: appsec-pipeline
on:
  pull_request:
  push:
    branches: [ main, master ]
env:
  TARGET_URL: ${{ vars.ZAP_TARGET_URL }}
permissions:
  contents: read
  security-events: write
jobs:
  appsec:
    runs-on: ubuntu-latest
    steps:
      - name: Checkout
        uses: actions/checkout@v4

      # --- SAST (Semgrep) ---
      - name: SAST – Semgrep (OWASP Top 10)
        uses: returntocorp/semgrep-action@v1
        with:
          config: p/owasp-top-ten
          generateSarif: true

      # --- Secrets (Gitleaks) ---
      - name: Secret scan – Gitleaks
        uses: gitleaks/gitleaks-action@v2
        with:
          args: "--redact --no-git"

      # --- SCA & IaC (Trivy) ---
      - name: SCA/IaC – Trivy (filesystem)
        uses: aquasecurity/[email protected]
        with:
          scan-type: 'fs'
          ignore-unfixed: true
          format: 'table'
          severity: 'CRITICAL,HIGH'
          exit-code: '1'
          output: trivy-fs.txt

      # --- Container Scan (Trivy) ---
      - name: Container scan – Trivy (image)
        if: hashFiles('Dockerfile') != ''
        uses: aquasecurity/[email protected]
        with:
          image-ref: 'app:${{ github.sha }}'
          format: 'table'
          severity: 'CRITICAL,HIGH'
          exit-code: '1'
          output: trivy-image.txt

      # --- SBOM (CycloneDX via Syft) ---
      - name: SBOM – CycloneDX (Syft)
        uses: anchore/syft-action@v0
        with:
          output: 'cyclonedx-json=sbom.cdx.json'
Interactive Quick Review: AppSec Controls
Reinforce key concepts regarding secure pipeline gates, authorization models, and runtime defenses before reading the FAQ:
Quick Review Verification
1. How does Row-Level Security (RLS) in databases prevent Insecure Direct Object References (IDOR)?
Answer: RLS enforces tenant and user authorization rules directly at the database engine layer. Even if an application contains a bug or an attacker swaps record IDs in a URL, the database automatically filters out query rows that do not match the current session’s authenticated
tenant_id or user context.2. What is the difference between SAST (Static) and DAST (Dynamic) security testing?
Answer: SAST inspects un-executed source code inside repositories to find structural flaws (hardcoded keys, unsafe functions). DAST executes automated security tests against a live, running application in staging to discover runtime vulnerabilities (missing security headers, auth bypasses, active injection endpoints).
Application Security — Frequently Asked Questions
1) Authentication vs Authorization — what’s the difference and what goes wrong most often?
Authentication (AuthN) verifies *who* a user/service is (passwords, MFA, passkeys, OIDC). Authorization (AuthZ) determines *what* they are permitted to do (roles, attributes, policies).
- Common AuthN Pitfalls: Missing MFA on admin routes, storing JWTs in
localStorageinstead of HttpOnly cookies, and long-lived refresh tokens without rotation. - Common AuthZ Pitfalls: Missing server-side checks (IDOR), relying on hidden UI fields, over-broad roles, and lack of tenant isolation.
2) How should we manage secrets and API keys across code and CI/CD?
Never hardcode secrets or store them in Git. Inject secrets at runtime from a centralized key manager (KMS / HashiCorp Vault), use short-lived workload identity tokens (OIDC federation) in CI/CD pipelines, and enforce pre-commit secret scanning hooks.
3) How do we prevent the most common app-layer vulnerabilities (OWASP Top 10)?
Use parameterized SQL queries for Injection, context-aware output escaping and CSP headers for XSS, SameSite/HttpOnly cookies for CSRF, server-side tenant checks for IDOR, and domain/IP allowlists for SSRF mitigation.
4) What’s the right way to use JWTs safely?
Prefer asymmetric algorithms (RS256/ES256), explicitly reject
alg=none, validate iss/aud/exp/nbf claims, store access tokens in HttpOnly+Secure cookies, keep TTLs short (≤15 min), and rotate refresh tokens using short-lived revocation deny-lists.5) How do we isolate tenants in a multi-tenant SaaS?
Pass a verified
tenant_id claim from identity tokens down to backend queries, enforce database Row-Level Security (RLS) requiring tenant_id = current_setting('app.tenant_id'), and encrypt per-tenant data using separate KMS envelope keys.6) What should a secure SDLC include?
Design-phase threat modeling (STRIDE), automated SAST and secret scanning on commit, peer code reviews with security checklists, DAST and API fuzzing in staging environments, and signed container images with attached SBOMs at release.
7) What should we log without violating privacy or leaking secrets?
Log structured JSON containing correlation IDs, timestamps, actor IDs, route paths, and access decisions (allow/deny). Automatically redact passwords, JWT tokens, credit card numbers, and high-cardinality PII.
8) When an internal vulnerability is found, what are the first steps?
Triage severity, apply immediate short-term mitigations (WAF blocking rule, feature flag disable, or token revocation), patch source code with regression tests, deploy hotfix, and conduct a blameless post-incident review.
Application Security: Conclusion
Application security is not a one-time gate but a continuous practice that starts at design and follows the software through build, test, release, and operations. The strongest programs pair secure-by-default architecture (least privilege, strong authentication and authorization, tenant isolation) with automated controls in CI/CD and continuous runtime monitoring.
- Design for security: Threat model early; choose simple, well-understood patterns; prefer deny-by-default.
- Automate verification: SAST/SCA/secret scanning, IaC/container checks, and DAST as CI/CD gates.
- Harden access: Robust AuthN and fine-grained AuthZ (RBAC/ABAC/ReBAC) with least privilege and short-lived credentials.
- Protect data: Encrypt in transit/at rest, use KMS + envelope encryption, and rotate keys and tokens on schedule.
- Segment & isolate: Per-tenant keys/IDs, row-level security, and clear boundaries between services and environments.
- Observe & respond: Structured, privacy-aware logs; alerts mapped to playbooks; regular game days to prove resilience.
Keep iterating: measure what matters (time-to-detect, time-to-fix, percentage coverage of automated checks), fix classes of bugs once, and evolve guardrails as the stack and threat landscape change. Security that is built-in, automated, and measured is security that lasts.
End-of-Page Exercises: Review, Reflections & Analytics
Review Questions and Answers
1. What is application security and why is it critical for modern software development?
Answer: Application security involves the controls, tools, and processes protecting software throughout its development and operational lifecycle. It is critical because attackers increasingly target application-layer business logic and APIs to steal data and compromise enterprise systems.
2. How does secure coding contribute to the overall effectiveness of application security?
Answer: Secure coding prevents vulnerabilities at code construction time, eliminating common flaw patterns like SQL injection, buffer overflows, and improper error handling before code is ever compiled or deployed to production.
3. What are some common vulnerabilities found in web applications and how can they be mitigated?
Answer: Common flaws include SQLi (mitigated by parameterized queries), XSS (mitigated by context-aware output encoding and CSP), CSRF (mitigated by SameSite cookies and anti-CSRF tokens), and IDOR (mitigated by server-side authorization checks).
4. How do penetration testing and vulnerability assessments improve application security?
Answer: Vulnerability assessments automate scanning for known CVE flaws, while penetration testing simulates real-world adversary attacks to uncover complex business logic flaws that automated tools miss.
5. What role does encryption play in protecting application data?
Answer: Encryption converts plaintext data into unreadable ciphertext using cryptographic algorithms (AES-256 at rest, TLS 1.3 in transit), ensuring data confidentiality even if physical disks or network streams are intercepted.
6. How do identity management and access control mechanisms enhance application security?
Answer: Identity management verifies actors via strong authentication (MFA/OAuth2), while access controls (RBAC/ABAC) enforce least-privilege permissions, ensuring users access only authorized application resources.
7. What is the significance of regular security audits in maintaining robust application security?
Answer: Security audits systematically evaluate codebases, CI/CD pipeline configurations, and access logs against frameworks like OWASP ASVS or SOC 2, identifying configuration drift and compliance gaps over time.
8. How can organizations mitigate risks associated with third-party software and supply chain attacks?
Answer: By generating Software Bill of Materials (SBOM), running automated SCA dependency scanners, pinning package lockfile versions, signing container images (Cosign), and enforcing strict dependency patch SLAs.
9. How do security frameworks and compliance standards influence application security practices?
Answer: Frameworks (NIST SSDF, OWASP ASVS, ISO 27001) establish formal security requirements, guiding organizations on mandatory controls like audit logging, encryption, threat modeling, and vulnerability remediation cadences.
10. How does integrating security into CI/CD pipelines benefit application development and deployment?
Answer: DevSecOps integration automates vulnerability detection inside PRs, blocking vulnerable code builds automatically before production release, accelerating deployment velocity while reducing remediation costs.
Thought-Provoking Architectural Questions
1. How might the convergence of artificial intelligence and application security revolutionize vulnerability detection?
Answer: Transformer-based LLMs analyze AST code structures to detect complex multi-file business logic flaws, auto-generate contextual security patches, and filter SAST false positives automatically inside CI pipelines.
2. What are the potential impacts of a Zero-Trust security model on application development and maintenance?
Answer: Forces developers to eliminate implicit internal network trust. Every internal API microservice call must explicitly authenticate via mTLS, verify short-lived JWT tokens, and enforce least-privilege authorization at every layer.
3. How can organizations balance rapid application development with the need for stringent security measures?
Answer: By deploying automated guardrails (pre-commit linters, PR security gates) rather than manual security review bottlenecks, providing developers with pre-approved secure library components, and standardizing threat modeling runbooks.
4. What future trends do you anticipate in application security, and how should organizations prepare?
Answer: Mandatory SBOM compliance, AI-driven prompt injection defenses, keyless cryptographic signing, and eBPF-based runtime observability. Prepare by adopting declarative policy-as-code and automating build artifact attestations.
5. How might regulatory developments influence the future landscape of application security in global markets?
Answer: Strict global laws (EU Cyber Resilience Act) make shipping software with unpatched critical vulnerabilities illegal, holding executives liable and mandating automated SBOM tracking and rapid 24-hour vulnerability disclosure workflows.
6. How can predictive analytics be utilized to enhance risk management in application security?
Answer: Correlates code churn metrics, developer experience levels, and historical bug locations to predict which application modules are statistically most likely to introduce security vulnerabilities during active feature sprints.
7. What role does continuous monitoring play in maintaining application security, and what are its long-term benefits?
Answer: RASP and SIEM logging provide real-time visibility into post-deployment exploit attempts, enabling instant automated containment (blocking malicious IPs or revoking tokens) and cutting mean time to detect (MTTD) from months to seconds.
8. How can organizations foster a culture of security awareness among developers?
Answer: Establish Security Champions programs inside development squads, integrate real-time IDE linting feedback, run hands-on capture-the-flag (CTF) workshops, and celebrate security improvements rather than placing blame.
9. What potential benefits and challenges do open-source security tools present for application security?
Answer: Benefits include zero licensing fees, community transparency, and customization flexibility. Challenges include maintaining custom rule sets, managing false positives, and lack of enterprise support SLAs.
10. How might the increasing complexity of modern applications influence the evolution of application security strategies?
Answer: Microservices, serverless, and multi-cloud environments dissolve traditional network firewalls, shifting security focus to service mesh mutual TLS (mTLS), standardized OAuth tokens, and programmatic policy-as-code enforcement.
11. How can organizations leverage threat intelligence to enhance proactive application security measures?
Answer: By feeding CISA Known Exploited Vulnerabilities (KEV) lists directly into SCA tools, automatically raising the fix priority of vulnerable open-source dependencies that are actively exploited in production environments globally.
12. How might advancements in quantum computing impact the future of application security, particularly regarding encryption?
Answer: Quantum algorithms (Shor’s algorithm) will break traditional RSA and ECC asymmetric encryption. Applications must adopt Post-Quantum Cryptography (PQC) standards (such as ML-KEM/Lattice-based algorithms) for TLS handshakes and token signing.
Numerical Engineering Problems & Solutions
Problem 1: Calculating Annual Financial Savings from Automated SAST Code Audits
Manual external code audits cost an organization $80,000 per year. Implementing automated SAST (Semgrep) and pre-commit secret scanning reduces manual security audit requirements by 50%. Calculate total annual financial savings.
Manual external code audits cost an organization $80,000 per year. Implementing automated SAST (Semgrep) and pre-commit secret scanning reduces manual security audit requirements by 50%. Calculate total annual financial savings.
Solution:
- Original manual audit cost = $80,000/year
- Cost reduction percentage = 50%
- Annual financial savings = $80,000 × 0.50 = $40,000/year
Problem 2: Estimating ROI for an AI-Driven Application Vulnerability Scanner
Deploying an AI-driven DAST and SAST security scanner costs $250,000 in software setup fees. The system generates $75,000 per year in reduced developer remediation labor and breach mitigation savings. Calculate payback period in years and 5-year Return on Investment (ROI) percentage.
Deploying an AI-driven DAST and SAST security scanner costs $250,000 in software setup fees. The system generates $75,000 per year in reduced developer remediation labor and breach mitigation savings. Calculate payback period in years and 5-year Return on Investment (ROI) percentage.
Solution:
- Payback period = Initial Investment / Annual Savings = $250,000 / $75,000 ≈ 3.33 years (3 years and 4 months)
- Total 5-year gross savings = $75,000 × 5 years = $375,000
- Net financial gain = $375,000 – $250,000 = $125,000
- 5-Year ROI = ($125,000 / $250,000) × 100 = 50.0%
Problem 3: Calculating Reduction in Incident Response Time via DevSecOps Automation
A manual incident response process takes an average of 60 minutes to analyze and patch a vulnerable production API route. Integrating automated CI/CD security pipelines reduces mean response containment time to 35 minutes. Calculate time saved per incident and percentage performance improvement.
A manual incident response process takes an average of 60 minutes to analyze and patch a vulnerable production API route. Integrating automated CI/CD security pipelines reduces mean response containment time to 35 minutes. Calculate time saved per incident and percentage performance improvement.
Solution:
- Time saved per incident = 60 minutes – 35 minutes = 25 minutes saved
- Percentage response time improvement = (25 / 60) × 100 ≈ 41.67%
Problem 4: Determining Cost Savings from Fewer Application Security Breaches
The average cost of a data breach resulting from an application-layer vulnerability is $500,000. Implementing Shift-Left SAST security gates reduces production breach occurrences by 2 incidents per year. Calculate total annual financial loss reduction.
The average cost of a data breach resulting from an application-layer vulnerability is $500,000. Implementing Shift-Left SAST security gates reduces production breach occurrences by 2 incidents per year. Calculate total annual financial loss reduction.
Solution:
- Cost per individual breach avoided = $500,000
- Breaches prevented per year = 2 incidents
- Total annual savings = 2 × $500,000 = $1,000,000/year
Problem 5: Calculating Average Cost Per Employee for Developer Secure Coding Training
A developer AppSec training curriculum costs an engineering department $20,000 per year and trains 250 software engineers. Calculate average cost per trained developer and projected cost to expand training to 500 developers.
A developer AppSec training curriculum costs an engineering department $20,000 per year and trains 250 software engineers. Calculate average cost per trained developer and projected cost to expand training to 500 developers.
Solution:
- Cost per individual developer = $20,000 / 250 developers = $80.00 per developer
- Projected cost for 500 developers = 500 × $80.00 = $40,000.00
Problem 6: Estimating Reduction in False Positive Alerts with Contextual SAST Rules
A legacy static code analysis scanner exhibits a 25% false positive alert rate across 1,000 PR scans (250 false alerts). Fine-tuning rule sets with custom Semgrep patterns lowers the false positive rate down to 10% (100 false alerts). Calculate net false alerts eliminated and relative percentage noise reduction.
A legacy static code analysis scanner exhibits a 25% false positive alert rate across 1,000 PR scans (250 false alerts). Fine-tuning rule sets with custom Semgrep patterns lowers the false positive rate down to 10% (100 false alerts). Calculate net false alerts eliminated and relative percentage noise reduction.
Solution:
- Initial false positive alerts = 1,000 × 0.25 = 250 alerts
- Fine-tuned false positive alerts = 1,000 × 0.10 = 100 alerts
- False alerts eliminated = 250 – 100 = 150 false alerts saved
- Relative percentage reduction = (150 / 250) × 100 = 60.0%
Problem 7: Calculating Threat Detection Accuracy Increase
A baseline DAST tool exhibits an 85% accuracy rate in detecting OWASP Top 10 vulnerabilities. Upgrading to a modern interactive security testing engine (IAST) increases vulnerability detection accuracy to 95%. Calculate absolute accuracy increase and relative percentage gain.
A baseline DAST tool exhibits an 85% accuracy rate in detecting OWASP Top 10 vulnerabilities. Upgrading to a modern interactive security testing engine (IAST) increases vulnerability detection accuracy to 95%. Calculate absolute accuracy increase and relative percentage gain.
Solution:
- Absolute accuracy gain = 95% – 85% = 10 percentage points
- Relative percentage improvement = (10% / 85%) × 100 ≈ 11.76%
Problem 8: Determining Total Annual Security Code Review Hours Saved
Manual peer security code reviews consume 300 engineering hours per month. Deploying automated CI/CD security linters automates standard checks, reducing manual review labor by 70%. Calculate monthly engineering hours saved and total annual hours saved.
Manual peer security code reviews consume 300 engineering hours per month. Deploying automated CI/CD security linters automates standard checks, reducing manual review labor by 70%. Calculate monthly engineering hours saved and total annual hours saved.
Solution:
- Monthly review hours saved = 300 hours × 0.70 = 210 hours saved/month
- Total annual hours saved = 210 hours × 12 months = 2,520 hours/year
Problem 9: Calculating Average Cost of an Application Data Breach per Incident
An enterprise records $4,000,000 in total annual losses across 8 independent application-layer data breach incidents. Calculate average financial cost per individual breach incident.
An enterprise records $4,000,000 in total annual losses across 8 independent application-layer data breach incidents. Calculate average financial cost per individual breach incident.
Solution:
- Average cost per breach = Total Annual Loss / Incident Count = $4,000,000 / 8 = $500,000 per incident
Problem 10: Estimating Savings from Improved API Authorization Controls
Implementing fine-grained API authorization checks (ABAC + IDOR guards) prevents an estimated 3 data leak incidents per year. Each leak incurs an average loss of $600,000. Calculate total annual financial risk reduction.
Implementing fine-grained API authorization checks (ABAC + IDOR guards) prevents an estimated 3 data leak incidents per year. Each leak incurs an average loss of $600,000. Calculate total annual financial risk reduction.
Solution:
- Incidents prevented = 3 breaches/year
- Cost per incident = $600,000
- Total annual savings = 3 × $600,000 = $1,800,000/year
Problem 11: Calculating Cost Efficiency & ROI of an AppSec Awareness Program
An internal developer security awareness program costs $15,000 per year. By training engineers in input validation, the program reduces web injection vulnerabilities, saving an estimated $50,000 per year in bug bounty payouts and emergency hotfixes. Calculate net annual savings and ROI percentage.
An internal developer security awareness program costs $15,000 per year. By training engineers in input validation, the program reduces web injection vulnerabilities, saving an estimated $50,000 per year in bug bounty payouts and emergency hotfixes. Calculate net annual savings and ROI percentage.
Solution:
- Net annual savings = $50,000 (losses avoided) – $15,000 (program cost) = $35,000/year
- ROI percentage = ($35,000 / $15,000) × 100 ≈ 233.33%
Problem 12: Break-Even Analysis for an AppSec Infrastructure Upgrade
Upgrading an enterprise to an automated DevSecOps platform (Snyk + Semgrep + Cosign) requires a $400,000 initial implementation investment. The system saves $35,000 per month in developer labor and vulnerability remediation costs. Calculate break-even payback period in months and total net operational savings over 5 years (60 months).
Upgrading an enterprise to an automated DevSecOps platform (Snyk + Semgrep + Cosign) requires a $400,000 initial implementation investment. The system saves $35,000 per month in developer labor and vulnerability remediation costs. Calculate break-even payback period in months and total net operational savings over 5 years (60 months).
Solution:
- Payback break-even period = $400,000 / $35,000 ≈ 11.43 months (rounded to 12th month)
- Total 60-month gross savings = 60 months × $35,000 = $2,100,000
- Net financial savings = $2,100,000 – $400,000 = $1,700,000